Hackers Begin Exploiting Critical Atlassian Data Center Flaw Within Hours of Disclosure
Hackers begin exploiting critical Atlassian Data Center vulnerability CVE-2026-21589 within hours of disclosure. Eight products affected, with patches available.
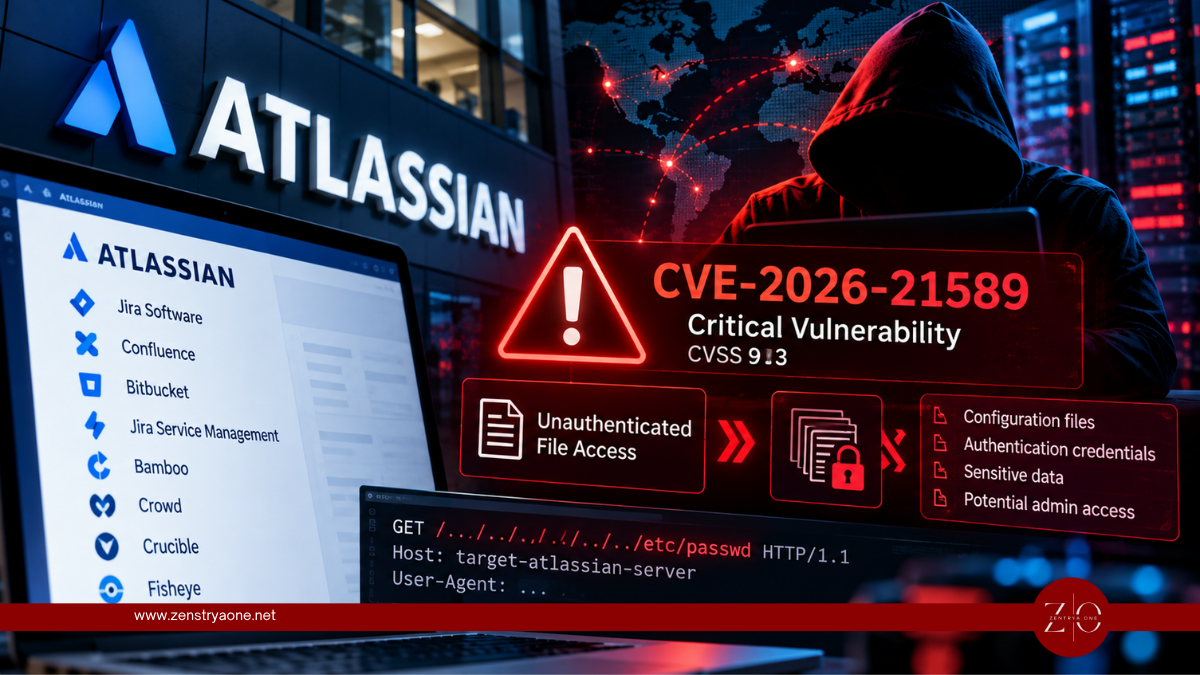
Security researchers have detected active exploitation attempts targeting a critical vulnerability affecting eight Atlassian Data Center products, just two hours after technical details became publicly available.
The vulnerability, tracked as CVE-2026-21589, carries a CVSS severity score of 9.3 (Critical) and allows unauthenticated attackers to access sensitive files stored within affected applications.
The flaw could expose configuration files, authentication credentials and other sensitive information, potentially enabling further attacks against enterprise environments.
What Is CVE-2026-21589?
CVE-2026-21589 is an arbitrary file access vulnerability affecting several widely used Atlassian products.
The vulnerability results from improper handling of resource paths, allowing specially crafted requests to access files that should not be publicly accessible.
Attackers do not need valid credentials to exploit the vulnerability. However, they must know the exact filename and path of the targeted resource.
The vulnerability does not allow attackers to browse entire directories or automatically execute malicious code.
Eight Atlassian Products Affected
The vulnerability affects the following products, with security updates now available:
| Product | Fixed Versions |
|---|---|
| Bitbucket Data Center | 9.4.26, 10.2.8, 10.5.1 |
| Confluence Data Center | 9.2.26, 10.2.19 |
| Jira Software Data Center | 9.12.40, 10.3.26, 11.3.12 |
| Jira Service Management | 5.12.40, 10.3.26, 11.3.12 |
| Bamboo Data Center | 10.2.24, 12.1.12 |
| Crowd Data Center | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible | 4.9.15 |
| Fisheye | 4.9.15 |
Organizations should upgrade to an appropriate fixed release or a newer supported version.
Atlassian Cloud products have already received the necessary fixes.
Exploitation Attempts Detected Within Two Hours
Security company Previdian reported detecting 15 exploitation attempts originating from three IP addresses in Japan and the United States.
The activity began approximately two hours after security researchers at watchTowr released additional technical details about the vulnerability.
The observed IP addresses were:
38.60.157[.]86146.70.187[.]234159.26.119[.]225
These addresses are useful indicators for investigation, although IP-based blocking alone is not sufficient protection.
watchTowr also confirmed observing exploitation attempts in the wild. Most observed activity involved identifying vulnerable installations and requesting known configuration files.
At the time of reporting, researchers had not observed subsequent malicious activity using credentials potentially obtained through exploitation.
How Attackers Could Gain Administrative Access
The vulnerability can expose sensitive application configuration files.
In certain Jira and Crowd deployments, attackers may be able to retrieve a file containing Crowd authentication credentials.
If those credentials are valid and sufficiently privileged, attackers could potentially use them to gain administrative access, create unauthorized accounts or modify existing user privileges.
The potential attack sequence is:
Unauthenticated Request → Sensitive File Access → Credential Exposure → Account Compromise → Privilege Escalation
Importantly, administrative compromise is a possible consequence of exposed credentials, not a direct capability of the vulnerability itself.
What Organizations Should Do Immediately
Atlassian recommends that organizations prioritize remediation of affected Data Center deployments.
Security teams should:
- Apply security patches to all affected Atlassian products.
- Restrict public internet access until systems are patched.
- Implement Atlassian-recommended WAF rules to block malicious path traversal requests.
- Review web server access logs for suspicious resource requests.
- Investigate possible credential exposure and rotate affected secrets where necessary.
- Monitor privileged account activity for unexpected account creation or permission changes.
Organizations unable to patch immediately should implement the temporary mitigations published in Atlassian's security advisory.
Security Takeaway
The rapid exploitation attempts against CVE-2026-21589 demonstrate how quickly attackers can act after technical vulnerability details become public.
Although the flaw primarily enables unauthorized file access, exposed configuration files and credentials can create opportunities for broader compromise.
Organizations using Atlassian Data Center products should treat remediation as an immediate priority, particularly where applications are accessible from the public internet.
Related reporting
Weekly Cybersecurity Recap: Atlassian Exploits, Helpdesk Zero-Days, Rogue Certificates and ShinyHunters Arrests
Weekly cybersecurity recap covering Atlassian CVE-2026-21589 exploitation, Zammad zero-days, ShinyHunters arrests, rogue Google certificates, DarkSword malware and emerging AI security threats.
Anthropic Expands Claude Access for Cybersecurity Teams After Discovering 129,000 Software Vulnerabilities
Anthropic expands Claude AI access for cybersecurity teams after Project Glasswing identifies over 129,000 verified software vulnerabilities, including thousands of critical and high-severity flaws.
LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Execute Code Without Macro Warnings
Critical LibreOffice and Apache OpenOffice vulnerabilities allow malicious spreadsheets to execute Java code without macro warnings. LibreOffice users should update, while OpenOffice users should disable Java until a fix is released.