 Live
Cloud & AppSec
MI5 Says China’s MSS Funded Research Involving More Than 100 U.K.-Linked Academics
MI5 says China's Ministry of State Security used CGTRI-linked funding for research involving more than 100 U.K.-linked academics in AI, cybersecurity and other technologies with potential espionage applications.
Android 17 Advanced Protection Blocks Unverified Apps From Accessibility Services
Police Disrupt KillSec Ransomware Group and Arrest Suspected 16-Year-Old Operator
Apple CoreGraphics Zero-Day PoC Emerges as WhatsApp PDF Checks Raise Delivery Questions
Latest reports
Page 1 of 13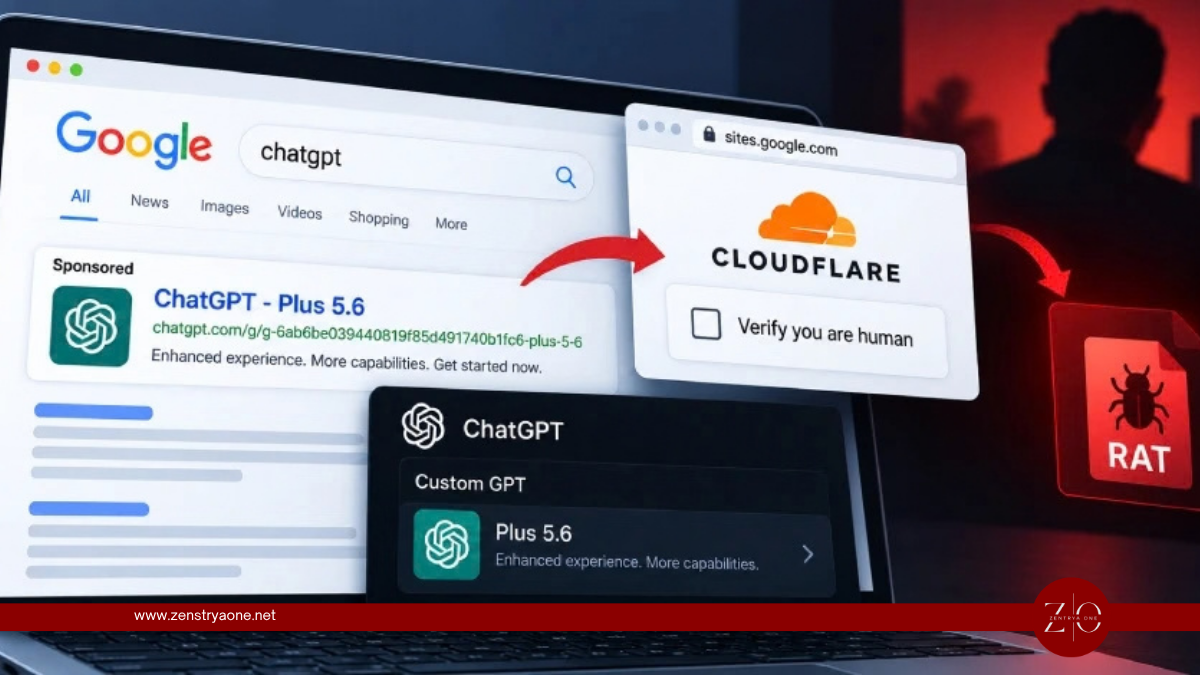
Malware
Attackers Abuse ChatGPT Custom GPTs to Deliver RAT Malware via ClickFix
Attackers abuse ChatGPT Custom GPTs and sponsored Google results to redirect victims to ClickFix pages that execute PowerShell and install remote access trojan malware.
Malware
Star Blizzard Targets 100+ Organizations With Fake Event Invites and CosmicPulse Backdoor
Russia-linked Star Blizzard targets more than 100 organizations using fake event invitations, the new RedFlick malware delivery technique and the CosmicPulse Windows backdoor.
critical
Vulnerabilities
Kiteworks Fixes Critical Vulnerability Discovered During Emergency Shutdown
Kiteworks patched a previously unknown critical vulnerability discovered during a nine-hour precautionary shutdown prompted by intelligence about a potential cyberattack, with no evidence of exploitation.
Malware
101 Malicious npm Packages Secretly Add Developers to WhatsApp Groups
Researchers uncover 101 malicious npm packages in the PhantomSub campaign that abuse authenticated WhatsApp sessions to secretly add developers to attacker-controlled groups and channels.
critical
Data Breaches
Rs. 2.87 Million Vanishes in 14 Minutes: Sri Lanka Banking Incident Raises Digital Fraud Questions
A Bank of Ceylon customer disputes 30 transactions totaling Rs. 2.869 million completed within 14 minutes. BOC says its systems were not breached, raising questions about credential theft, OTP security and digital banking fraud.
critical
Vulnerabilities
TeamFiltration Campaign Compromises Microsoft 365 Service Accounts Using Default Passwords
TeamFiltration attackers targeted over 5,700 Microsoft 365 accounts across 28 tenants, compromising seven unmanaged service accounts using default or unrotated passwords without MFA.
critical
CVE-2026-87902
Vulnerabilities
Attackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure
Attackers are actively exploiting WordPress CVE-2026-87902, a critical CVSS 9.2 flaw that enables unauthenticated local PHP file inclusion and conditional remote code execution.
Malware
Attackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp Registry
Researchers uncover malicious Terraform providers and Go modules delivering Graphalgo-linked Go malware using Slack and Ethereum blockchain infrastructure for command and control.
Vulnerabilities
Leaked GitLab Issue Email Address Can Let Attackers Push Code and Run CI Jobs
A leaked GitLab incoming email address can let attackers impersonate users, push code to permitted branches and trigger CI/CD pipelines without passing normal 2FA or IP restrictions.