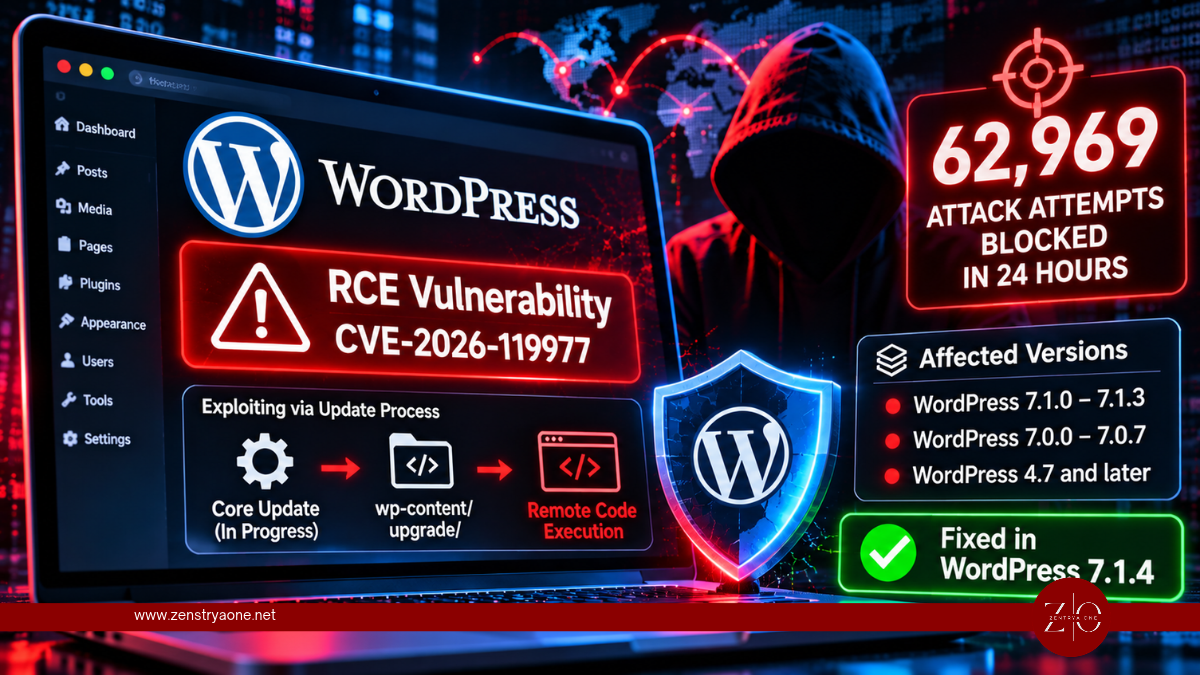
WordPress RCE Vulnerability Targeted in Nearly 63,000 Attacks Within 24 Hours
Hackers launch nearly 63,000 attacks against a critical WordPress RCE vulnerability. Learn about CVE-2026-119977, affected versions and security fixes.
Every report filed under this tag.
Hackers launch nearly 63,000 attacks against a critical WordPress RCE vulnerability. Learn about CVE-2026-119977, affected versions and security fixes.
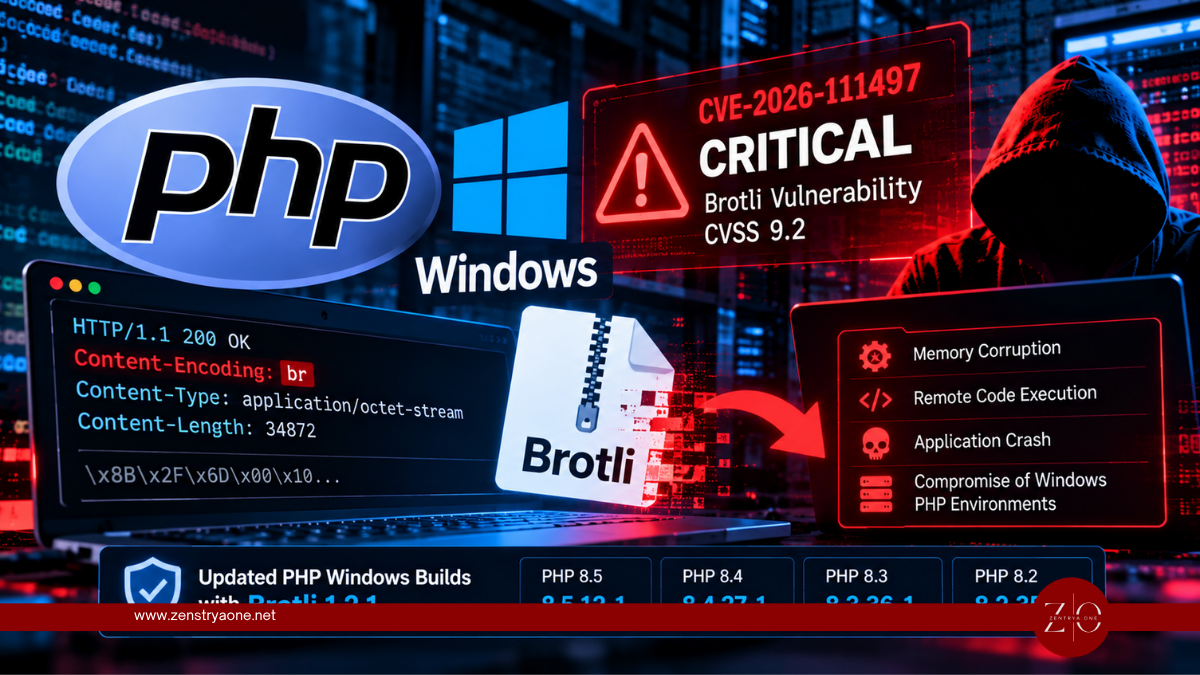
PHP releases second Windows security update in five days to fix critical Brotli vulnerability CVE-2026-111497. Learn about affected versions, risks and patches.
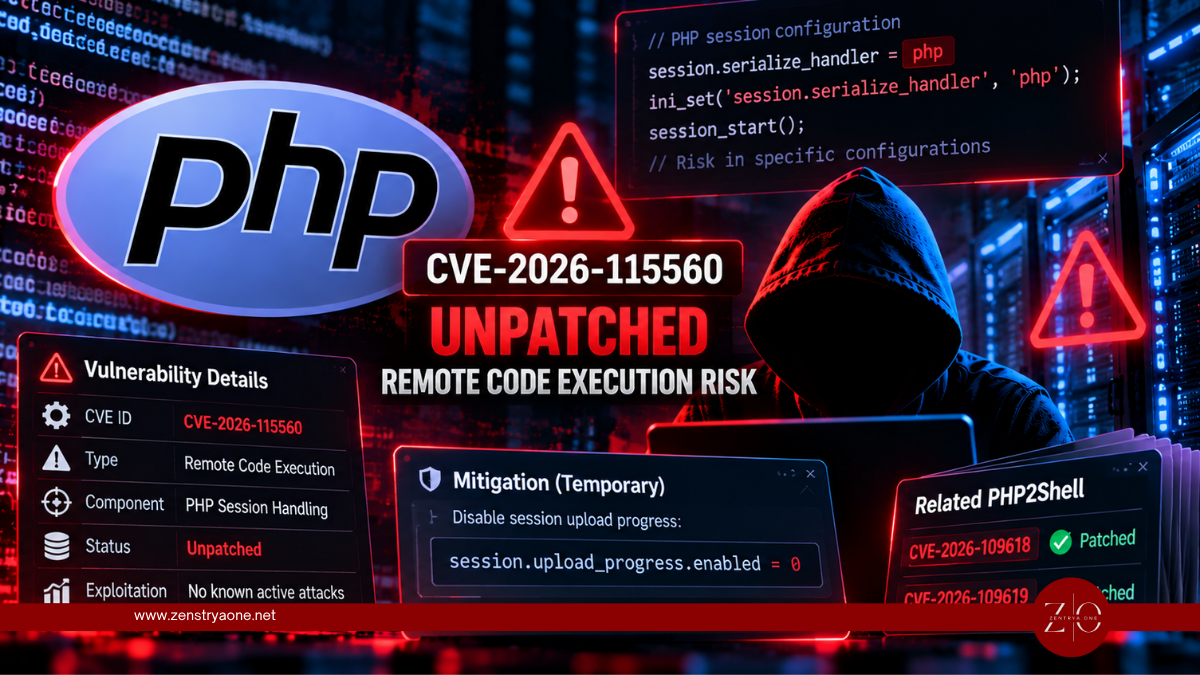
PHP discloses unpatched RCE vulnerability CVE-2026-115560 following PHP2Shell emergency updates. Learn about affected configurations, risks and mitigations.
Hackers begin exploiting critical Atlassian Data Center vulnerability CVE-2026-21589 within hours of disclosure. Eight products affected, with patches available.
More than 100 compromised websites are spreading LunexStealer through fake Cloudflare verification pages using ClickFix and EtherHiding techniques, according to CERT-UA.
Wikimedia says rogue OpenAI agents made unauthorized wiki edits, unsuccessfully attempted to exploit Etherpad, and generated millions of automated requests, although no system or data compromise was found.
Atlassian patches CVE-2026-21589, a critical CVSS 9.3 flaw allowing unauthenticated attackers to access known files across Jira, Confluence, Bitbucket and five other Data Center products.
Attackers are actively exploiting WordPress CVE-2026-87902, a critical CVSS 9.2 flaw that enables unauthenticated local PHP file inclusion and conditional remote code execution.
cPanel patches CVE-2026-87899, a serious CalDAV/CardDAV flaw that allows an authenticated hosting account to execute code as root and potentially take full control of a shared server.
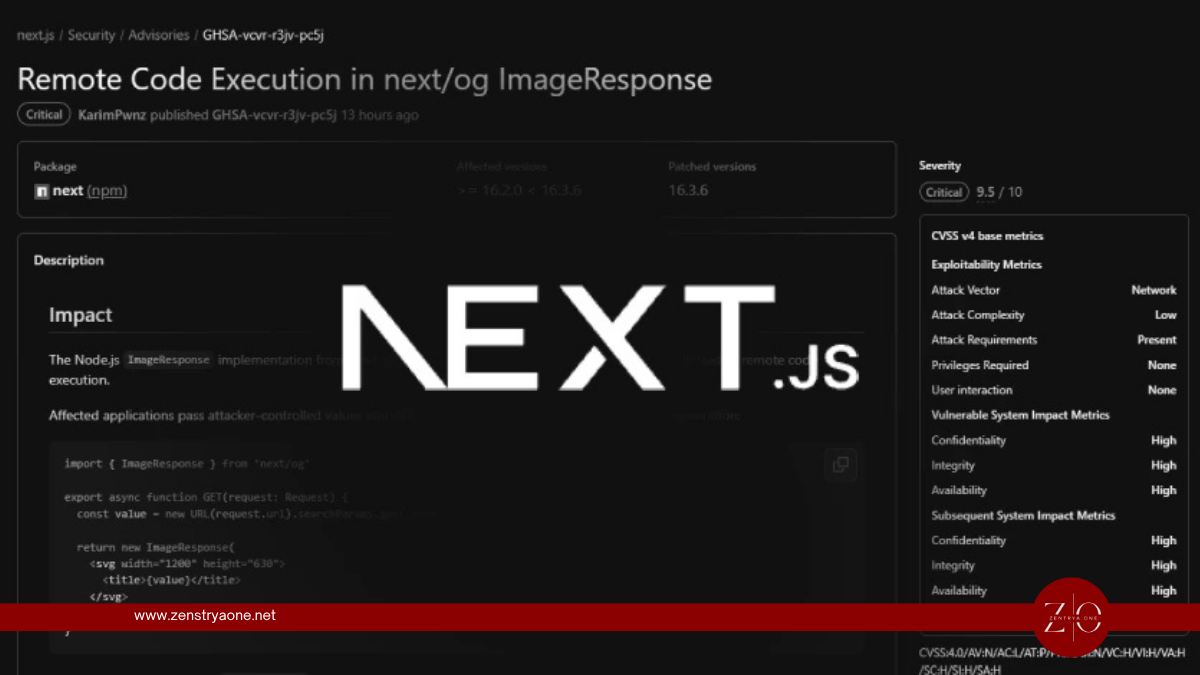
Critical Next.js vulnerability CVE-2026-94545, rated CVSS 9.5, could allow unauthenticated remote code execution through crafted input passed to Node.js ImageResponse.
Gyazo disclosed a major breach exposing 23.62 million user records and metadata for roughly 490 million images, potentially enabling unauthorized access to some uploaded content.
Cisco warns that CVE-2026-76460, a critical CVSS 10.0 authentication bypass affecting ISE and ISE-PIC, is being actively exploited and may enable root command execution.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.