ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
ShinyHunters claims it breached FBI systems and stole sensitive data on agents, employees and job applicants, while the FBI investigates unauthorized activity affecting FBIJobs.gov.
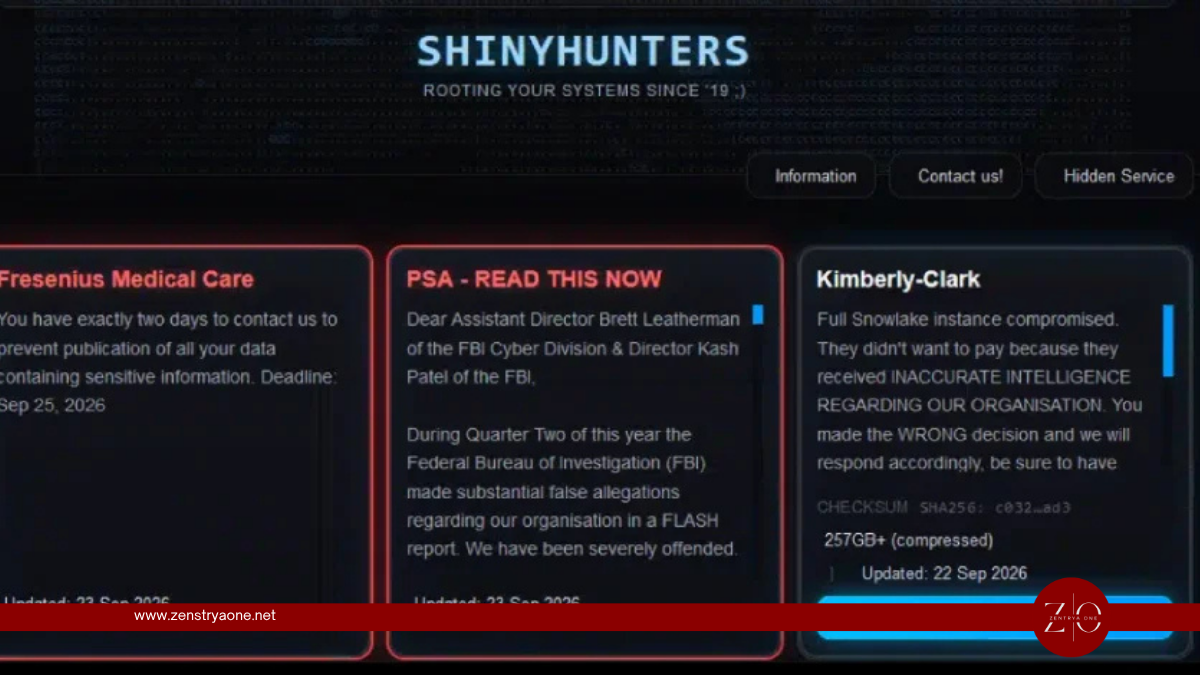
Cyber extortion group ShinyHunters claims it breached systems associated with the U.S. Federal Bureau of Investigation (FBI) and stole sensitive information belonging to current and former employees, agents, and job applicants.
The FBI has acknowledged unauthorized activity affecting FBIjobs.gov and says it is actively investigating. However, the bureau has not confirmed the full scope of ShinyHunters' claims or whether the attackers compromised the FBI's wider internal network.
What ShinyHunters Claims
ShinyHunters claims it obtained approximately 2–3 TB of data, potentially covering thousands of current and former FBI personnel and applicants.
The group says the compromised information includes data associated with systems involving:
- Human resources
- Criminal justice
- Medical information
- Current and former employees
- FBI job applicants
- Contact and other personally identifiable information
Reuters examined data allegedly stolen in the incident and found records containing detailed information about FBI personnel and some of their assignments, including work involving foreign intelligence and criminal investigations.
Other reporting says samples provided by the attackers contained information corresponding to real FBI or Justice Department personnel, although the source, completeness, and full scale of the dataset remain under investigation.
FBIJobs.gov Targeted
The incident visibly affected the FBI's recruitment infrastructure.
ShinyHunters reportedly defaced the FBI jobs website with its own message, while the application portal was subsequently made unavailable. The FBI confirmed it is investigating activity affecting the service.
The group claims the initial compromise involved a previously unknown Oracle PeopleSoft pre-authentication remote code execution vulnerability.
However, no technical details or independent confirmation of this claimed zero-day have been publicly released. Therefore, the alleged PeopleSoft zero-day should currently be treated as an attacker claim rather than an established cause of the breach.
The reported attack path is therefore:
Claimed PeopleSoft Zero-Day → FBIJobs.gov Compromise → Website Defacement → Alleged Lateral Movement → Alleged Bulk Data Theft
Only parts of this chain have been independently supported by public reporting.
Why the Stolen Data Could Be Serious
If the reported personnel information is authentic and extensive, its exposure could create significant risks for affected individuals.
Potential threats include:
- Highly targeted phishing
- Identity theft
- Social engineering
- Credential attacks
- Harassment or impersonation
- Targeting of employees' family members
- Intelligence gathering against personnel
- Follow-on cyberattacks
The concern becomes greater when leaked records identify not only individuals but also their roles, assignments, contact information, or relationships.
Reuters reported that some records contained granular information concerning FBI employees' work, increasing the sensitivity of the alleged exposure.
Why ShinyHunters Says It Targeted the FBI
ShinyHunters says the operation was conducted in response to an FBI advisory published earlier in 2026 concerning the group's activities and tactics.
The group disputes portions of the FBI's characterization and says it wants the agency to correct or withdraw those statements. This is ShinyHunters' stated explanation for the attack, not an independently established motive.
Investigation Continues
The FBI says the point of compromise remains undetermined, including whether the intrusion originated through a third-party provider or FBI-managed infrastructure.
The agency says it is working with third parties supporting FBIJobs.gov to investigate the incident and mitigate potential risks.
This distinction is important: compromise of the recruitment platform does not by itself prove that the attackers penetrated the FBI's broader enterprise network.
Security Takeaway
The ShinyHunters incident demonstrates the security risks created by externally accessible recruitment, HR, and third-party enterprise platforms.
Organizations should treat these systems as high-value targets because they can contain extensive employee and applicant PII while also maintaining integrations with identity, HR, cloud, and internal business systems.
For now, the confirmed picture is narrower than ShinyHunters' claims:
FBIJobs.gov Unauthorized Activity → FBI Investigation → Personnel Data Samples Reported → Full Breach Scope and Initial Access Still Under Investigation
The alleged 2–3 TB data theft, compromise of nearly all FBI personnel records, and exploitation of a new PeopleSoft zero-day have not yet been fully independently confirmed.
Related reporting
Rs. 2.87 Million Vanishes in 14 Minutes: Sri Lanka Banking Incident Raises Digital Fraud Questions
A Bank of Ceylon customer disputes 30 transactions totaling Rs. 2.869 million completed within 14 minutes. BOC says its systems were not breached, raising questions about credential theft, OTP security and digital banking fraud.
Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Entries
Gyazo disclosed a major breach exposing 23.62 million user records and metadata for roughly 490 million images, potentially enabling unauthorized access to some uploaded content.
Revolut Data Breach Exposes Passports and Full Transaction Histories After Fake Government Request
Fintech giant Revolut has confirmed a data-security incident in which an unauthorized party obtained sensitive customer information after submitting fraudulent requests that appeared to come from a legitimate government agency.