MI5 Says China’s MSS Funded Research Involving More Than 100 U.K.-Linked Academics
MI5 says China's Ministry of State Security used CGTRI-linked funding for research involving more than 100 U.K.-linked academics in AI, cybersecurity and other technologies with potential espionage applications.
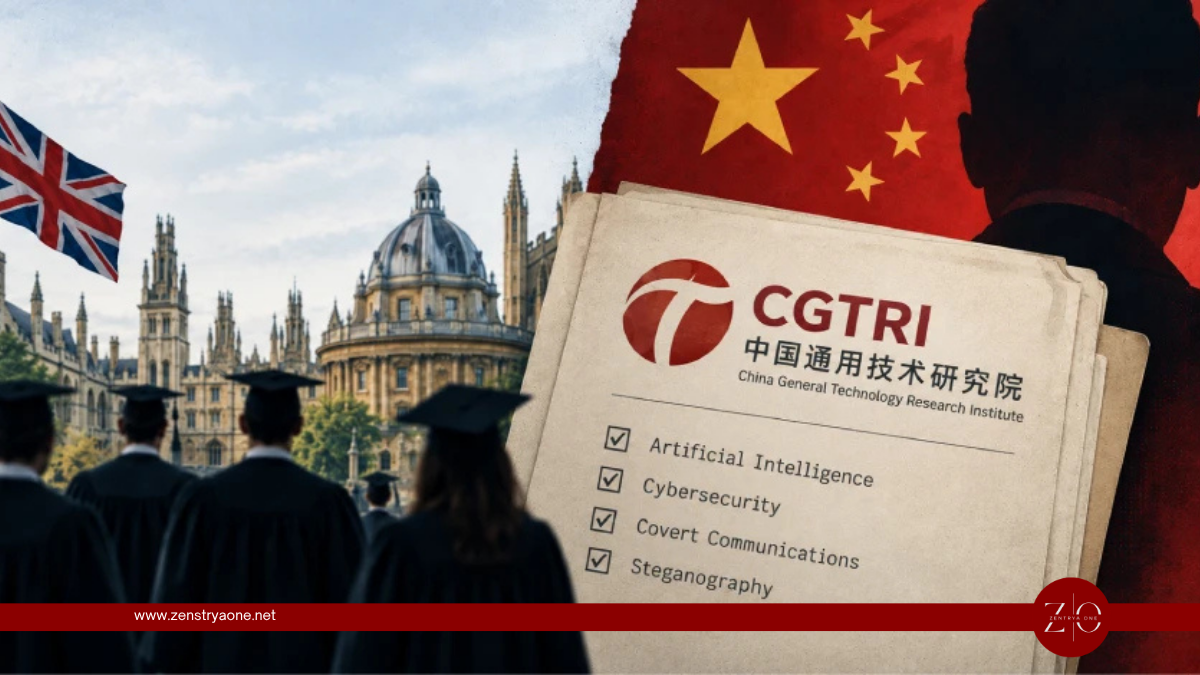
The U.K.'s domestic intelligence agency MI5 has issued an unusual public espionage warning claiming that more than 100 U.K.-linked academics contributed to research projects ultimately funded by China's Ministry of State Security (MSS).
MI5 says the research was funded through the China General Technology Research Institute (CGTRI), also known as the China Academy of General Technology (CAGT), which the agency assesses as having strong links to the MSS.
What MI5 Says Happened
According to MI5's September 30 Espionage Alert, CGTRI funds academic research in China covering technologies with potential intelligence applications, including:
- Artificial intelligence
- Cybersecurity
- Covert communications
- Steganography
- Other advanced technologies
MI5 says the organization's primary purpose is to fund research that directly improves the MSS's technical capabilities for espionage.
More than 100 academics linked to the U.K. are believed to have contributed to projects receiving funding through CGTRI.
Importantly, MI5 acknowledged that some researchers may not have known the ultimate source or intended purpose of the funding.
Research Could Support Cyber Operations
The Hacker News reports that some CGTRI-linked research involved vulnerabilities affecting widely deployed technologies, including products from Microsoft and VMware.
The concern is that legitimate vulnerability research and advanced cybersecurity expertise could potentially be used to improve offensive cyber capabilities when transferred to organizations linked to intelligence services.
The broader risk can be summarized as:
Academic Collaboration → Foreign Research Funding → Advanced Cyber Research → Intelligence Capability Development
This does not mean the academics themselves were conducting espionage. MI5 specifically noted that researchers may have participated without knowing who ultimately funded or benefited from their work.
Universities Told to Review Research Partnerships
MI5 is advising U.K. universities and researchers to immediately review existing or planned collaboration involving CGTRI.
Institutions are being encouraged to:
- Identify the ultimate source of research funding.
- Conduct stronger due diligence on overseas research partners.
- Review existing relationships involving CGTRI.
- Evaluate sensitive cybersecurity and AI research before sharing it.
- Seek independent legal advice where necessary.
MI5 also warned institutions and researchers to understand their obligations under the U.K. National Security Act 2023, particularly where collaboration could provide material assistance to a foreign intelligence service.
China Rejects the Allegations
The Chinese Embassy in London rejected MI5's accusations, describing them as unfounded and saying China opposes what it characterized as interference with normal academic exchanges.
The embassy urged the U.K. government not to undermine academic cooperation between the two countries.
Security Takeaway
The MI5 warning highlights a growing research-security and technology-transfer risk for universities working in cybersecurity, AI and other sensitive technical fields.
Organizations should therefore consider not only their immediate research partner but also:
Who Funds the Research → Who Controls the Partner → Where the Results Go → How the Technology Could Be Used
The case also demonstrates why universities increasingly need security and compliance reviews around sensitive international research collaborations, particularly when projects involve vulnerability research, artificial intelligence or technologies with potential dual-use applications.
Related reporting
Android 17 Advanced Protection Blocks Unverified Apps From Accessibility Services
Android 17 Advanced Protection restricts AccessibilityService access to verified accessibility tools, helping block banking malware, spyware and financial fraud while adding USB, WebGPU and intrusion-logging defenses.
Attacker Hijacks AI Coding Assistant Session and Spreads Shai-Hulud Across 100 Repositories
An attacker hijacked an AI coding-assistant session at a SaaS provider, stole GitHub OAuth tokens and spread the Shai-Hulud worm across about 100 internal code repositories.
N0va Phishkit Targets US and European Businesses With Device-Code Authentication Attacks
N0va phishing attacks target US and European organizations by abusing Microsoft device-code authentication to obtain access and refresh tokens, potentially enabling SSO account takeover even after MFA.