State Bank of India Confirms Data Leak as 3,897 Customer Records Appear on Dark Web
State Bank of India confirms a data leak involving 3,897 customer records found on the dark web. SBI investigates the source and extent of the exposure.
October 22, 2026 | Data Breach & Banking Security
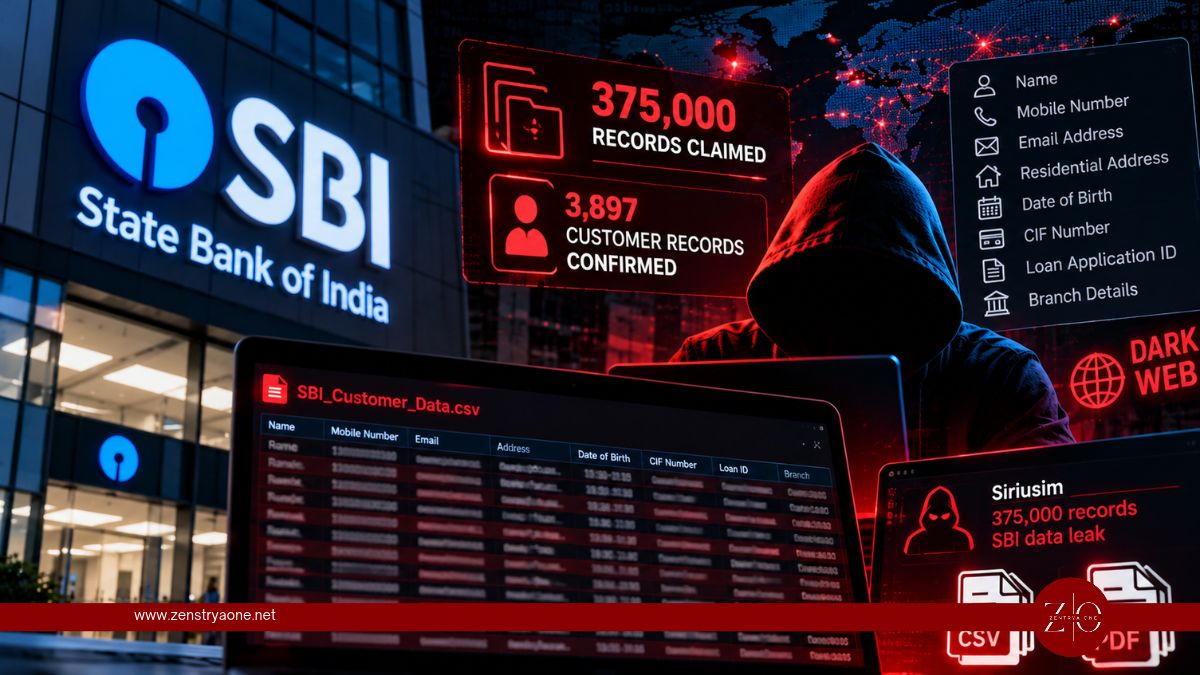
India's largest public-sector bank, State Bank of India (SBI), has disclosed a data security incident after identifying 3,897 customer records containing personally identifiable information (PII) within a larger dataset circulating on the dark web.
The bank confirmed the incident in a regulatory filing dated October 21, 2026, but said the source, authenticity and full extent of the exposed information remain under investigation.
What Customer Information Was Exposed?
SBI's preliminary assessment examined approximately 375,000 records, identifying 3,897 records containing customer information.
The reportedly exposed data includes:
- Customer names and registered mobile numbers
- Email addresses and residential addresses
- Dates of birth and gender
- Bank branch identifiers
- Customer Information File (CIF) numbers
- Loan application identifiers
- Metadata associated with loan records
The bank has not confirmed that all 375,000 records belong to SBI customers.
How Was the Data Leak Discovered?
On October 16, 2026, SBI received security alerts from its threat intelligence service provider, India's Computer Emergency Response Team (CERT-In), and the Defence Cyber Agency.
The alerts indicated that customer information associated with the bank might be circulating on the dark web.
Following the notification, SBI activated its cybersecurity incident response procedures and launched an investigation.
The bank also appointed an independent CERT-In-approved cybersecurity firm to determine the origin, authenticity and potential impact of the exposed data.
Hacker Claims to Possess 375,000 Records
A threat actor using the name Siriusim reportedly claimed to have released approximately 375,000 records in CSV format and 2,722 PDF documents associated with SBI.
The allegedly leaked documents include customer information, loan applications and account-opening records.
However, the claims have not been independently verified in full.
Investigators have not established whether the information originated directly from SBI's infrastructure, a subsidiary or an external service provider.
SBI Says Banking Operations Remain Unaffected
Despite the reported exposure, SBI stated that the incident has not materially affected its core banking operations, financial performance or business continuity.
The bank's critical services continue to operate normally.
SBI has not publicly identified the attacker or confirmed the technical method used to obtain the information.
The investigation is ongoing, with additional security and preventive measures being implemented as necessary.
Potential Risks to Customers
Although the bank's disclosure does not identify passwords, payment card information or account balances among the exposed data categories, the reported personal information could still create cybersecurity risks.
Attackers could potentially use the information for:
- Targeted phishing emails and SMS messages
- Banking impersonation scams
- Social engineering attacks
- Identity fraud
- Fraudulent loan-related communications
Criminals may use accurate personal details to make fraudulent messages appear legitimate.
Security Recommendations
Customers should remain cautious about unexpected banking communications and avoid sharing passwords, PINs or one-time passwords with anyone claiming to represent the bank.
Financial institutions should strengthen:
- Dark web monitoring and threat intelligence
- Third-party security assessments
- Sensitive customer data protection
- Data loss prevention controls
- Incident response and investigation procedures
- Access monitoring and data exfiltration detection
Security Takeaway
The SBI incident highlights the continuing risks associated with the exposure of customer information in the financial sector.
While the bank has identified 3,897 customer records in its preliminary analysis, the complete scale and origin of the reported leak remain unknown.
The incident reinforces the importance of proactive threat intelligence, third-party risk management and continuous monitoring of sensitive banking information.
Related reporting
EY Data Breach Exposes Sensitive Information of Goldman Sachs and Man Group Clients
EY data breach exposes sensitive tax and financial information belonging to Goldman Sachs, Man Group and Tishman Speyer clients following unauthorized access to a third-party IT support platform.
FBI Removes Accenture Contractor After Missed Patch Linked to ShinyHunters Breach
The FBI removed an Accenture contractor after a missed security patch contributed to a ShinyHunters-linked breach that exposed sensitive personal information belonging to thousands of FBI employees.
Denmark Says Attackers Accessed CPR Data of 8.8 Million People Through Company Account
Denmark investigates unauthorized access to CPR data linked to about 8.8 million people after attackers abused a private company's legitimate access to the national population register.