Telegram Desktop Flaw Lets Hidden JavaScript Steal Messages From HTML Chat Exports
Security researchers have disclosed a high-severity vulnerability in Telegram Desktop that could allow malicious JavaScript hidden inside a seemingly normal chat message to execute when a conversation is exported as HTML and opened in a web browser.
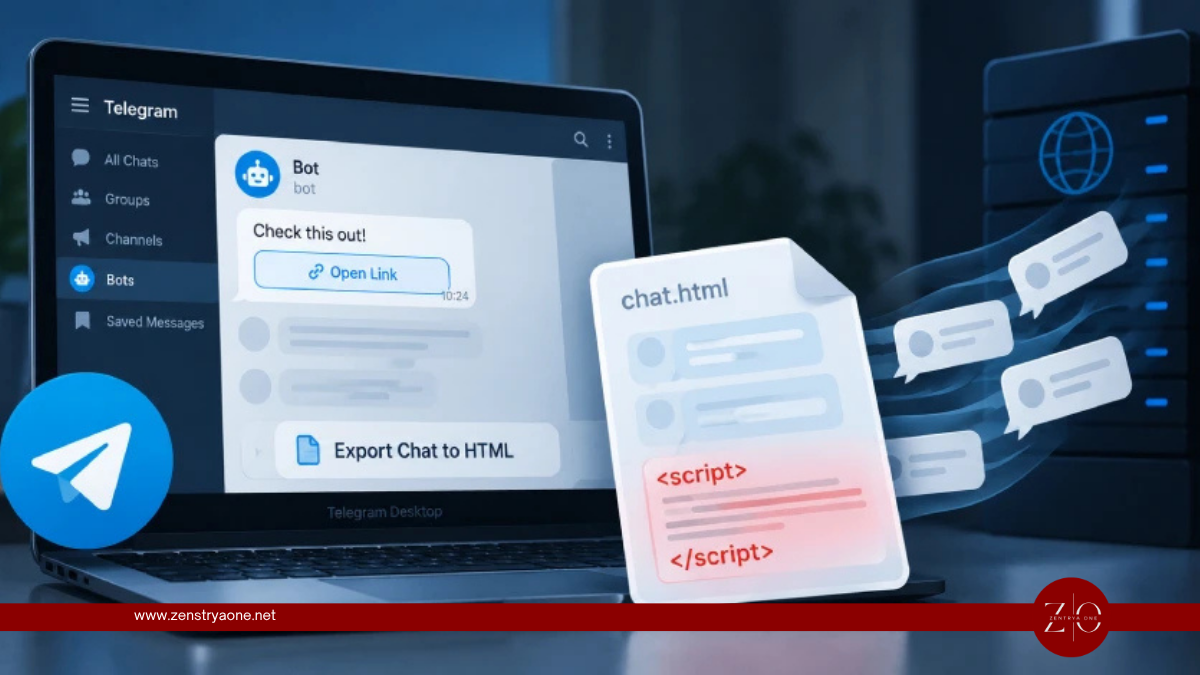
The flaw affected Telegram Desktop's HTML export functionality and could potentially expose messages, sender information, timestamps and other conversation metadata contained within the exported file.
Telegram fixed the vulnerability in July 2026. However, previously generated HTML exports are not automatically repaired by updating Telegram, meaning older archive files may continue to contain dormant malicious JavaScript.
How the Vulnerability Worked
The vulnerability was discovered by security researchers Denis Rostilov and Aleksander Rostilov of ExPatch Vulnerability Research.
Telegram bots can attach interactive buttons, known as inline keyboards, beneath messages. The researchers discovered that when Telegram Desktop exported conversations to HTML, the text associated with these buttons was inserted into the resulting HTML without being properly escaped.
Other information, including normal message text and sender names, was sanitized before being added to the HTML.
The missing sanitization for button text created a stored cross-site scripting (XSS) condition.
An attacker could therefore construct a bot message containing JavaScript within the inline button text and use invisible characters to make the malicious content appear harmless inside Telegram.
Attack Can Remain Dormant Inside Chat History
One of the more concerning aspects of the vulnerability is that the attacker's bot does not necessarily need to join the targeted group.
Researchers found that bot messages containing web-link buttons could retain those buttons when forwarded.
A malicious message could therefore be created by an attacker-controlled bot and subsequently forwarded into another Telegram conversation.
The attack sequence could look like:
Attacker creates malicious bot message
↓
JavaScript embedded inside inline-button text
↓
Message forwarded into another Telegram chat
↓
Payload remains dormant in chat history
↓
Victim exports conversation using vulnerable Telegram Desktop
↓
Telegram generates poisoned HTML archive
↓
Victim opens HTML file in browser
↓
JavaScript automatically executes
The malicious message could theoretically remain inside the conversation for months or years before someone eventually exports the chat.
What Could Attackers Steal?
Once an affected HTML export was opened in a browser with JavaScript enabled, the injected script could access information rendered within that document.
Researchers demonstrated that the script could obtain information including:
- Chat messages
- Sender names
- Message timestamps
- Chat name
- Conversation type
- Member count
- Local file path information
The information could then potentially be transmitted to an attacker-controlled server.
However, Telegram divides large HTML exports into files containing up to 1,000 messages each. As a result, JavaScript executing within one exported page would have access to that page's contents rather than automatically gaining access to the victim's entire Telegram account.
Exported Conversations Could Also Be Manipulated
Data theft was not the only potential consequence.
Because the attacker-controlled JavaScript executed inside the exported page, it could also modify what the user saw.
In one demonstration, researchers replaced the exported conversation interface with a fake Telegram verification page.
The technique could potentially alter displayed:
- Messages
- Sender information
- Dates
- Timestamps
- Other elements within the exported conversation
This creates an additional integrity concern when HTML exports are being retained as records or archives.
Importantly, such manipulation affects what is displayed in the browser. It does not modify the original conversation stored by Telegram, and researchers said it did not rewrite the saved export file itself.
Multiple Conditions Required for Exploitation
The vulnerability does not allow an attacker to compromise someone simply by sending them a Telegram message.
Several conditions must be satisfied:
| Requirement | Description |
|---|---|
| Malicious message | Attacker-controlled content must exist in the conversation |
| Vulnerable Telegram version | HTML must be exported using an affected Telegram Desktop build |
| HTML export | User must export the affected conversation |
| Browser execution | Exported HTML must be opened in a browser |
| JavaScript enabled | Browser must permit the embedded JavaScript to execute |
This makes the vulnerability different from a traditional zero-click messaging exploit.
The malicious code executes outside Telegram itself, when the vulnerable export is opened as an HTML document in a web browser.
Telegram Desktop Versions Affected
The vulnerable export behavior had reportedly existed in stable Telegram Desktop releases since version 4.15.1, released in March 2024.
| Status | Telegram Desktop Version |
|---|---|
| Affected | 4.15.1 through 6.9.3 |
| Fixed Beta | 6.9.4 or later |
| Fixed Stable | 7.0.1 or later |
The fix adds the missing escaping mechanism to the inline-button text before Telegram writes the content into exported HTML.
Old HTML Exports Remain a Security Risk
Updating Telegram Desktop prevents newly generated HTML exports from containing the vulnerability.
But it does not modify HTML files that were created previously.
This means a user could update to the latest Telegram Desktop version today but still possess an old HTML archive containing malicious JavaScript.
Those files could remain dangerous whenever they are opened in a browser with JavaScript enabled.
For organizations that maintain Telegram exports for investigations, compliance, legal evidence or archival purposes, this distinction is particularly important.
What Users Should Do
Users of Telegram Desktop should:
- Upgrade to Telegram Desktop 7.0.1 or later.
- Treat HTML chat exports generated with older versions as potentially untrusted.
- Re-export important conversations after updating Telegram.
- Delete outdated HTML exports when they are no longer required.
- Avoid opening old Telegram HTML exports with JavaScript enabled.
- Security teams should consider scanning archived HTML files for unexpected script elements before opening them.
Users running Telegram Desktop's beta channel should use version 6.9.4 or later.
No Evidence of Active Exploitation
The researchers reported the vulnerability to Telegram on June 3, 2026, after discovering it earlier that month.
Telegram confirmed the issue and developed a fix, which reached Telegram Desktop 6.9.4 Beta on July 3 and stable 7.0.1 on July 14.
The vulnerability was publicly disclosed by ExPatch on September 12 after the fixes had already been released.
The researchers said their testing was conducted using their own accounts and test groups, and their report does not indicate that the vulnerability was exploited against real Telegram users.
As of the public disclosure, the vulnerability had not been assigned a CVE identifier. ExPatch assessed the issue at CVSS 8.2, but this is the researchers' rating rather than an official Telegram or NVD score.
Security Takeaway
The Telegram Desktop vulnerability demonstrates how seemingly harmless archived data can become an attack vector when it is converted into an executable format such as HTML.
The malicious JavaScript did not execute while users normally viewed messages inside Telegram. Instead, the security boundary changed when Telegram transformed the conversation into an HTML document and the browser interpreted improperly sanitized content as executable code.
The incident also highlights a broader security concern surrounding exported data. Backups, reports and archives are often considered passive files, but formats such as HTML can contain active content capable of executing inside a browser.
For Telegram users, updating the application is therefore only part of the remediation. Previously generated HTML exports should also be considered potentially unsafe and recreated using a patched Telegram Desktop version.
SEO Meta Description:
A Telegram Desktop stored XSS flaw allowed hidden JavaScript in bot messages to execute inside HTML chat exports, potentially stealing messages and manipulating archived conversations.
Related reporting

Hackers Exploit Critical WSO2 API Manager JWT Flaw Using Forged Admin Tokens
Security researchers have detected active exploitation attempts targeting a critical authentication-bypass vulnerability in WSO2 API Manager, with attackers sending forged JSON Web Tokens (JWTs) containing administrator privileges.

Nintendo Switch Vulnerability Lets Nearby Attackers Run Unauthorized Code via QR Code Feature
Nintendo has patched a high-severity vulnerability in the original Nintendo Switch that could allow a nearby attacker to execute unauthorized code or access information stored on the console.

China-Linked Hackers Chain Chrome and Windows Zero-Days to Deploy GRIMWEDGE Backdoor
China-linked threat actors have been observed chaining multiple vulnerabilities in Google Chrome and Microsoft Windows as part of sophisticated cyber-espionage campaigns targeting non-governmental organizations and other high-value organizations.