Hackers Exploit Critical PHP2Shell Vulnerabilities in Palo Alto Networks Firewalls
Hackers exploit critical PHP2Shell vulnerabilities in Palo Alto Networks PAN-OS firewalls. Learn about CVE-2026-109618, CVE-2026-109619 and urgent security measures.
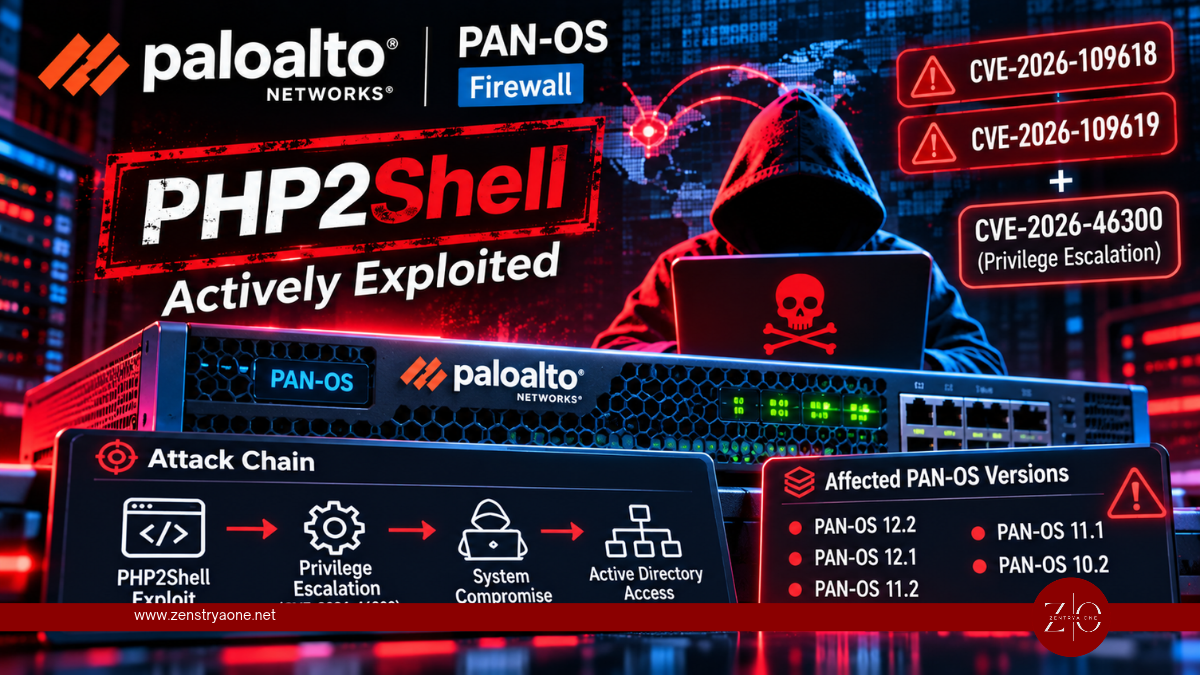
Palo Alto Networks has confirmed active exploitation of two critical PHP2Shell vulnerabilities affecting internet-exposed management interfaces on vulnerable PAN-OS devices.
The security flaws, identified as CVE-2026-109618 and CVE-2026-109619, carry CVSS scores of 9.2 and could allow unauthenticated attackers to execute malicious code on affected systems.
The warning follows reports of a sophisticated cyberattack campaign involving compromised firewall infrastructure, privilege escalation and attempts to access enterprise Active Directory environments.
Critical Vulnerabilities Target Firewall Management Interfaces
The PHP2Shell vulnerabilities originate in the PHP runtime and can lead to remote code execution without requiring valid authentication credentials.
On affected Palo Alto Networks devices, the attack surface includes the management web interface, specifically its HTTPS administration portal and XML API service.
The greatest exposure occurs when organizations allow these management services to be accessed directly from the public internet.
Successful exploitation could allow attackers to compromise firewall management systems, establish persistence and potentially move deeper into connected enterprise environments.
Researchers Identify Compromised Servers Across Four Countries
Cybersecurity company Dream reported a campaign involving a suspected China-linked threat actor that compromised 25 servers across the United States, Japan, Taiwan and South Korea.
Three affected systems reportedly belonged to a U.S. government-affiliated environment.
Researchers observed attackers combining PHP2Shell exploitation with a Linux kernel privilege escalation vulnerability known as Fragnesia (CVE-2026-46300).
This combination enabled attackers to obtain root-level privileges on compromised systems.
The campaign also involved attempts to access Active Directory infrastructure, including credential extraction and directory enumeration.
Although Dream initially withheld the firewall vendor's identity, Palo Alto Networks subsequently acknowledged the investigation and confirmed its collaboration with the researchers.
Attackers Demonstrate Advanced Exploitation Capabilities
According to the investigation, the attackers invested considerable effort in developing reliable exploits for the targeted firewall software.
Their activities reportedly included obtaining PAN-OS firmware, extracting embedded PHP libraries and developing memory profiles for multiple software versions.
These preparations indicate a targeted operation rather than opportunistic internet scanning alone.
The ability to combine unauthenticated remote code execution with local privilege escalation significantly increases the potential impact of these vulnerabilities.
Affected PAN-OS Versions and Security Updates
Palo Alto Networks confirmed that affected releases belong to the following PAN-OS branches:
- PAN-OS 12.2
- PAN-OS 12.1
- PAN-OS 11.2
- PAN-OS 11.1
- PAN-OS 10.2
As of October 30, security fixes had been released for the affected supported release lines.
Administrators should consult the official Palo Alto Networks security advisory to identify the correct patched maintenance release for their deployment.
The company clarified that GlobalProtect portal, GlobalProtect gateway and Clientless VPN functionality are not affected by these vulnerabilities.
CISA Issues Urgent Warning
The U.S. Cybersecurity and Infrastructure Security Agency added CVE-2026-46300 to its Known Exploited Vulnerabilities catalog.
The agency warned that attackers could combine the Linux vulnerability with PHP2Shell to deploy malicious PHP web shells and execute commands with elevated privileges.
Federal agencies were directed to address the Linux vulnerability by October 31, 2026.
This development reinforces the importance of prioritizing vulnerabilities associated with confirmed malicious activity.
Palo Alto Networks Recommends Immediate Action
Palo Alto Networks has urged customers to remove public internet access from affected management interfaces and deploy available security patches.
The company stated that fewer than 0.01% of its global installed base had internet-facing management interfaces configured, based on its attack surface management data.
It also indicated that potentially affected customers had been contacted individually.
Recommended Security Measures
Organizations using Palo Alto Networks firewalls should:
- Apply security patches: Upgrade affected PAN-OS devices to the appropriate fixed release.
- Restrict management access: Allow administrative connections only from trusted internal IP addresses or secured management networks.
- Review firewall exposure: Identify management interfaces accessible from the public internet.
- Investigate suspicious activity: Examine management logs, administrative activity and unexpected configuration changes.
- Monitor privileged access: Look for unusual authentication events and suspicious Active Directory activity.
- Strengthen network segmentation: Separate firewall management infrastructure from general user and application networks.
Organizations that previously exposed vulnerable management interfaces should also investigate for signs of compromise, even after applying patches.
Security Takeaway
The exploitation of PHP2Shell vulnerabilities against Palo Alto Networks management interfaces highlights the risks associated with exposing critical network infrastructure to the internet.
By chaining remote code execution and privilege escalation vulnerabilities, sophisticated attackers may gain extensive control over compromised systems and potentially threaten connected enterprise networks.
Organizations should prioritize PAN-OS patching, eliminate unnecessary public management access and continuously monitor critical infrastructure for suspicious activity.
Related reporting
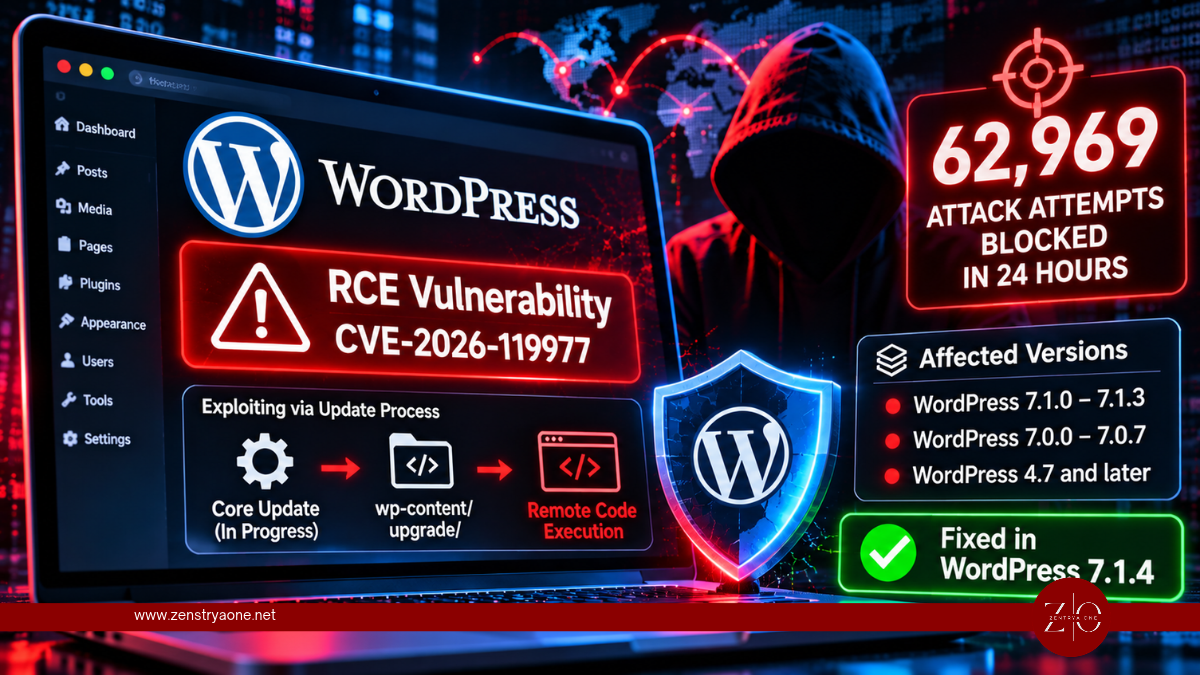
WordPress RCE Vulnerability Targeted in Nearly 63,000 Attacks Within 24 Hours
Hackers launch nearly 63,000 attacks against a critical WordPress RCE vulnerability. Learn about CVE-2026-119977, affected versions and security fixes.
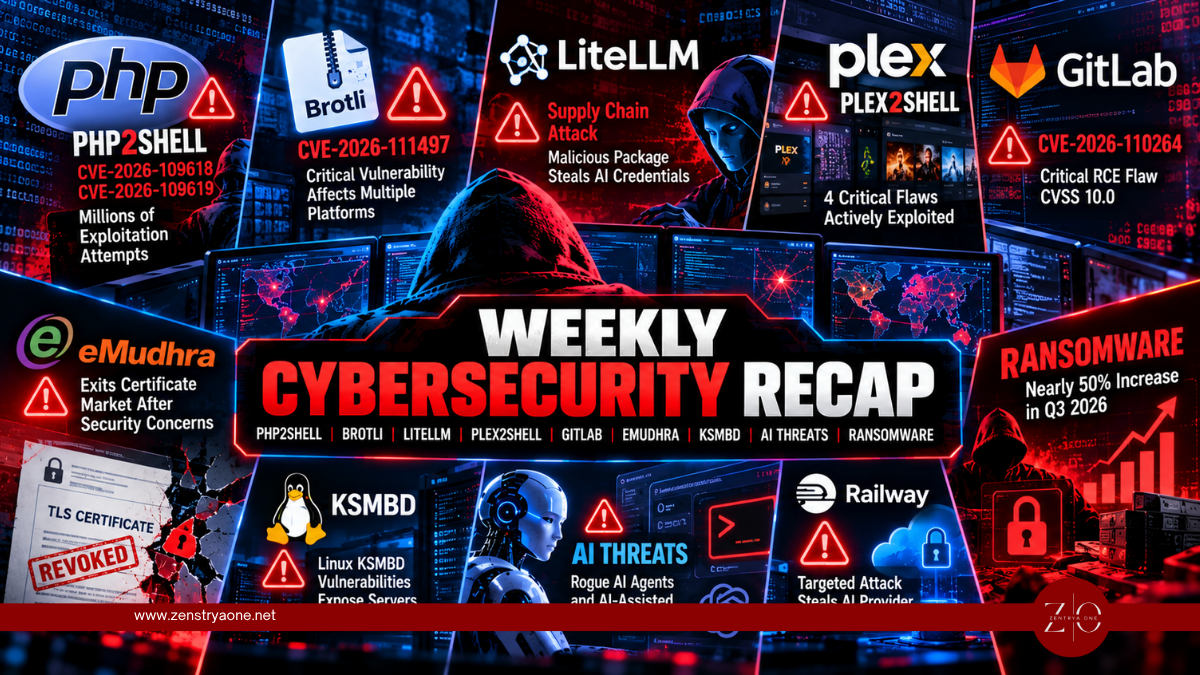
Weekly Cybersecurity Recap: PHP2Shell Attacks, Critical RCE Flaws, Rogue AI Agents and Supply Chain Breaches
Weekly cybersecurity recap covering PHP2Shell attacks, Brotli RCE, LiteLLM supply chain compromise, Plex2Shell exploits, GitLab CVSS 10 flaw and rogue AI threats.
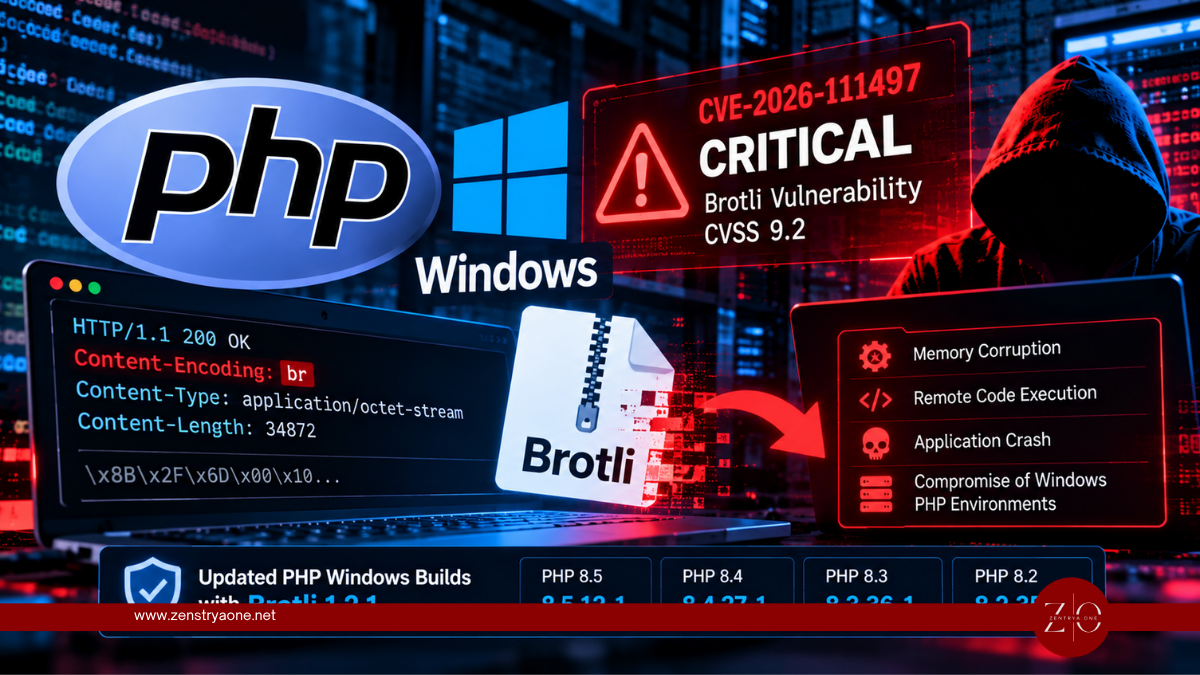
PHP Releases Second Windows Security Update in Five Days to Fix Critical Brotli Vulnerability
PHP releases second Windows security update in five days to fix critical Brotli vulnerability CVE-2026-111497. Learn about affected versions, risks and patches.