Chinese Hackers Use AI-Powered ARTEX to Target More Than 200 Organizations Worldwide
Chinese hackers use AI-powered ARTEX to target over 200 organizations worldwide. CrowdStrike links the campaign to Vapor Panda, with nine confirmed intrusions.
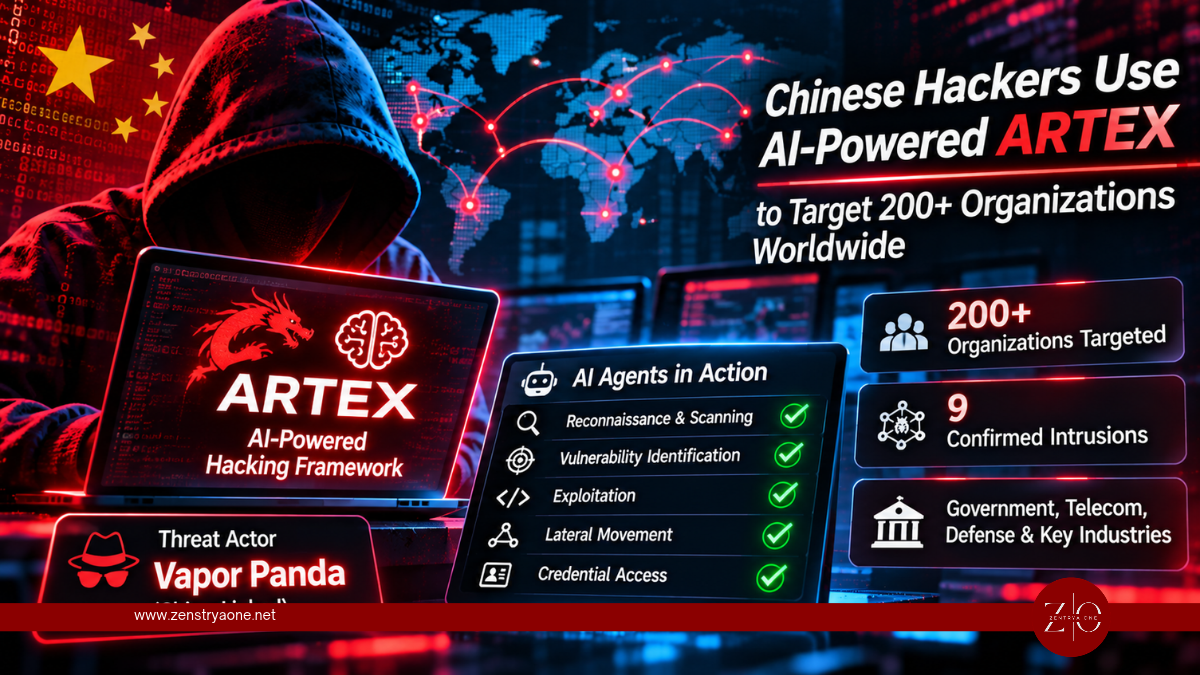
A China-linked cyber espionage group has launched a large-scale campaign using an artificial intelligence-powered hacking framework known as ARTEX, targeting more than 200 organizations across multiple countries.
According to cybersecurity company CrowdStrike, the threat actor, tracked as Vapor Panda, used autonomous AI agents to accelerate reconnaissance, identify security weaknesses and conduct coordinated intrusion attempts against government agencies, telecommunications providers and critical industries.
Researchers confirmed post-exploitation activity at nine organizations, demonstrating how AI-assisted attack tools are enabling sophisticated threat actors to conduct operations at an unprecedented scale.
What Is ARTEX?
ARTEX is a Go-based, AI-powered penetration testing framework designed to automate various cybersecurity assessment activities.
Unlike traditional security tools that require extensive manual interaction, ARTEX uses multiple AI agents to coordinate tasks and execute complex workflows.
The framework can perform activities such as:
- Automated network reconnaissance and vulnerability identification
- Identification of potential attack paths
- Exploitation of vulnerable systems
- Credential discovery and privilege escalation
- Internal network enumeration
- Lateral movement across compromised environments
Researchers identified the use of DeepSeek alongside another commercial large language model to support the campaign.
The attackers employed a combination of planning agents and worker agents, allowing multiple operations to run simultaneously under human supervision.
More Than 200 Organizations Targeted
CrowdStrike reported that Vapor Panda began using ARTEX against over 200 organizations worldwide on October 17, 2026.
The targeted organizations included government institutions and strategically important industries across several regions.
Notable targets included:
- Foreign ministries and government institutions in Latin America, Europe, Asia and the Middle East
- Nineteen U.S. organizations operating in pharmaceutical, semiconductor, defense, nuclear and financial sectors
- Telecommunications providers in the United States, Belgium and the Philippines
- Government agencies responsible for defense, finance, intelligence and justice
The targeting pattern suggests that the campaign was primarily focused on cyber espionage and intelligence collection.
Nine Organizations Confirmed Compromised
While more than 200 organizations were targeted, researchers confirmed post-exploitation activity at nine organizations.
Following initial access, attackers deployed BLOODALCHEMY, a malware family associated with the ShadowPad backdoor ecosystem.
The malware enabled attackers to maintain access to compromised environments while conducting additional reconnaissance.
Observed post-compromise activities included credential spraying, internal network scanning and attempts to obtain privileged access.
Researchers also identified password-spraying and credential-scanning activity against at least 12 additional organizations.
These findings indicate that the attackers were attempting to expand their access beyond initially compromised systems.
How AI Accelerated the Cyberattacks
One of the most significant aspects of the campaign was the extensive use of autonomous AI agents.
Instead of manually performing every stage of an intrusion, attackers assigned tasks to AI agents capable of exploring multiple attack paths simultaneously.
The framework was observed supporting activities involving web applications, cloud environments, container infrastructure, Active Directory and VPN systems.
Researchers identified attack sequences involving weaknesses in SAML authentication, XML external entity processing and cloud metadata services.
Other observed activities included deploying web shells, extracting privileged credentials and abusing insecure authentication mechanisms.
In one intrusion, CrowdStrike estimated that ARTEX planning agents processed approximately 1.4 billion input tokens, highlighting the scale of automated analysis involved.
Human operators remained involved in directing the operation, including tasks related to credential extraction and evasion of endpoint security controls.
Who Is Vapor Panda?
Vapor Panda is a China-linked threat actor previously tracked as VexatiousTemper.
The group was first identified in February 2021 and overlaps with activity associated with Earth Estries, a threat cluster documented by Trend Micro.
The group has been associated with targeted cyber espionage operations against high-value organizations.
Its adoption of ARTEX represents a significant development in the use of artificial intelligence for offensive cybersecurity operations.
Rather than introducing entirely new attack techniques, the framework enables attackers to execute established intrusion methods faster and across a larger number of targets.
AI-Powered Cyberattacks Raise New Security Concerns
The campaign demonstrates how autonomous AI tools can significantly increase the operational capacity of cyber threat actors.
A relatively small group of attackers can now coordinate reconnaissance and exploitation activities against numerous organizations simultaneously.
AI agents can also investigate alternative attack paths when initial attempts fail, reducing the manual effort traditionally required during complex intrusions.
For security operations centers, this creates additional challenges involving detection speed, alert prioritization and incident response.
Organizations may face increasingly automated attacks capable of operating continuously across multiple infrastructure environments.
Security Recommendations
Organizations, particularly those operating critical infrastructure and government systems, should consider the following measures:
- Strengthen identity security: Implement phishing-resistant MFA, conditional access and privileged access management.
- Monitor automated reconnaissance: Detect unusual scanning, repeated authentication failures and suspicious API activity.
- Secure cloud environments: Restrict access to metadata services and regularly review cloud permissions.
- Improve endpoint monitoring: Deploy EDR/XDR capabilities to detect web shells, credential theft and lateral movement.
- Protect Active Directory: Monitor privileged account activity, delegation configurations and credential access attempts.
- Review exposed services: Identify vulnerable internet-facing applications, VPN gateways and authentication systems.
- Enhance threat hunting: Investigate unusual activity across endpoints, cloud infrastructure and identity platforms.
- Accelerate incident response: Use automated detection and response workflows to reduce attacker dwell time.
Security teams should also review threat intelligence related to Vapor Panda, ARTEX and BLOODALCHEMY to identify relevant indicators of compromise.
Security Takeaway
The ARTEX campaign highlights a major shift in the cyber threat landscape, where artificial intelligence is increasingly being used to automate complex attack operations.
With more than 200 organizations targeted and nine confirmed cases of post-exploitation activity, the campaign demonstrates the potential impact of AI-assisted cyber espionage.
Although human operators continue to direct these attacks, autonomous AI agents are enabling threat actors to operate faster, investigate multiple vulnerabilities simultaneously and scale their activities across international targets.
Organizations must strengthen identity protection, vulnerability management, threat detection and incident response capabilities to defend against increasingly automated cyber threats.
Related reporting
Police Disrupt KillSec Ransomware Group and Arrest Suspected 16-Year-Old Operator
International law enforcement disrupts KillSec ransomware in Operation KillSwitch, arresting three suspects including a 16-year-old alleged operator and securing more than 110 TB of data.
U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks
The FBI seized domains linked to NightmareStresser, a major DDoS-for-hire service blamed for hundreds of thousands of actual or attempted attacks worldwide since 2022.
Threat Intelligence Alone Cannot Close the Growing Exploitation Gap
Threat intelligence alone cannot stop rapidly evolving cyberattacks. Learn how security validation, risk-based vulnerability management and faster remediation can help organizations close the growing exploitation gap.