Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users’ Mailboxes
Microsoft patches CVE-2026-96940, a high-severity Exchange Server flaw that could let authenticated attackers access other users' mailboxes, emails and attachments.
Microsoft has released out-of-band security updates for a high-severity Microsoft Exchange Server vulnerability that could allow an authenticated attacker to access other users' mailboxes within the same organization.
Tracked as CVE-2026-96940, the vulnerability carries a CVSS score of 8.8 and results from weak authorization controls in Microsoft Exchange Server.
CVE-2026-96940 at a Glance
| Detail | Information |
|---|---|
| CVE | CVE-2026-96940 |
| Severity | High |
| CVSS | 8.8 |
| Type | Elevation of Privilege |
| Authentication | Required |
| Impact | Unauthorized mailbox access |
| Active Exploitation | No evidence currently |
| Microsoft Assessment | Exploitation More Likely |
The vulnerability does not provide unauthenticated access. An attacker must already possess valid credentials before attempting exploitation.
What Can an Attacker Access?
Successful exploitation could allow an authenticated attacker to gain unauthorized access to mailboxes belonging to other users within the same Exchange organization.
This could expose:
- Email messages
- Email attachments
- Sensitive business communications
- Confidential information stored in mailboxes
The flaw does not allow cross-tenant mailbox access, limiting exploitation to the affected organization's Exchange environment.
A simplified attack path would be:
Compromised Account → Exploit CVE-2026-96940 → Authorization Bypass/Elevation → Access Other Internal Mailboxes → Read Emails and Attachments
This makes stolen credentials particularly concerning because an attacker could potentially expand access beyond the originally compromised mailbox.
Which Exchange Versions Are Affected?
Microsoft identified the following on-premises Exchange releases as affected:
- Exchange Server Subscription Edition RTM
- Exchange Server 2016 CU23
- Exchange Server 2019 CU14
- Exchange Server 2019 CU15
Microsoft has released security updates addressing CVE-2026-96940 and several other Exchange vulnerabilities. For example, the October 2 update for Exchange Server Subscription Edition also addresses eight additional CVEs.
Exchange Online Already Protected
Organizations using Exchange Online do not need to deploy an update specifically for CVE-2026-96940.
Microsoft says it has already implemented a related service-side fix protecting Exchange Online customers.
The primary patching requirement therefore applies to organizations operating affected on-premises Microsoft Exchange Server environments.
No Active Exploitation Detected — Yet
Microsoft says there is currently no evidence that CVE-2026-96940 has been exploited in the wild.
However, the company has classified exploitation as “Exploitation More Likely,” increasing the urgency for administrators to deploy the available security updates.
Microsoft researcher Jan Mitchell was credited with discovering and reporting the vulnerability.
What Organizations Should Do
Exchange administrators should prioritize installing Microsoft's October 2 security updates and verify successful deployment using the Exchange Server Health Checker.
Security teams should also review:
- Unexpected mailbox access
- Suspicious authenticated sessions
- Compromised or unusual user accounts
- Abnormal access to multiple mailboxes
- Unusual attachment downloads
- Privileged Exchange activity
- Authentication from unexpected locations or devices
Organizations still running Exchange Server 2016 or 2019 should also note that these releases have reached end of support. Microsoft says eligible organizations enrolled in the applicable Extended Security Update program can continue receiving security updates through the end of October 2026; others should migrate to Exchange Server Subscription Edition.
Security Takeaway
CVE-2026-96940 demonstrates why compromising even a standard user account can become significantly more dangerous when combined with a privilege-escalation vulnerability.
The risk progression is straightforward:
Credential Compromise → Exchange Vulnerability → Other Mailboxes Accessed → Sensitive Corporate Data Exposed
There is currently no evidence of active exploitation, but Microsoft's “Exploitation More Likely” assessment means organizations running affected on-premises Exchange servers should treat the update as a high priority.
Related reporting
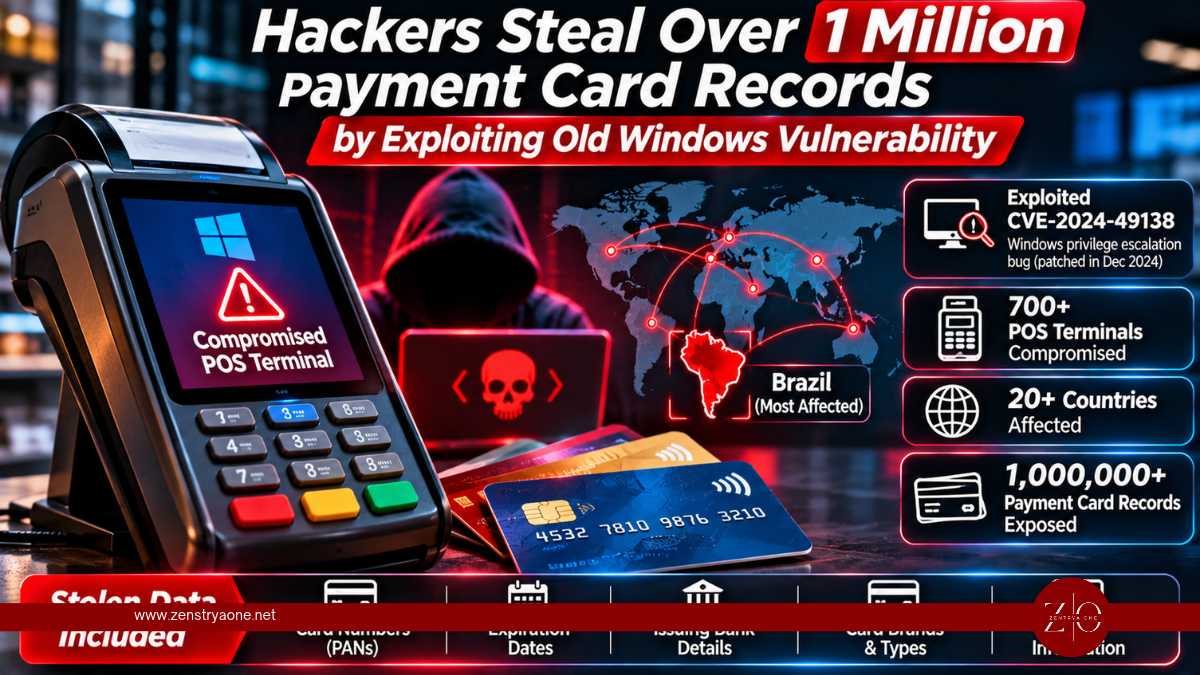
Hackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability
Hackers exploit Windows CVE-2024-49138 to compromise over 700 POS terminals across 20 countries, stealing more than one million payment card records.
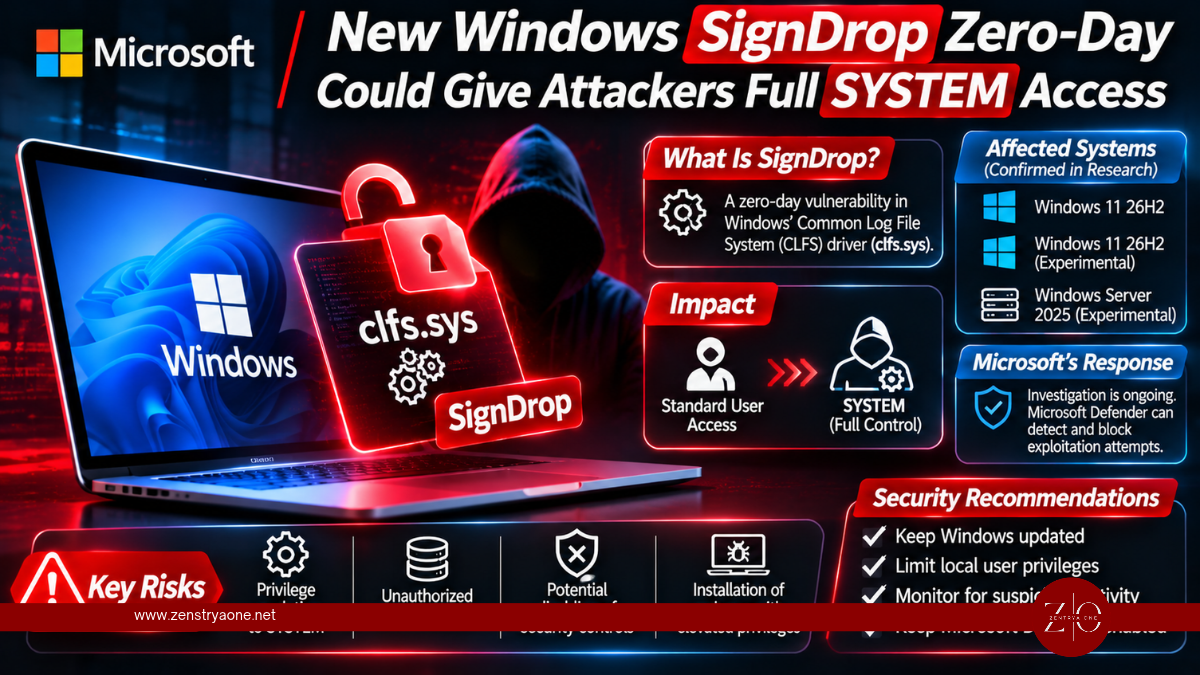
New Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access
New Windows SignDrop zero-day exploit abuses Microsoft CLFS security protections to gain SYSTEM privileges. Learn about affected systems and mitigation.
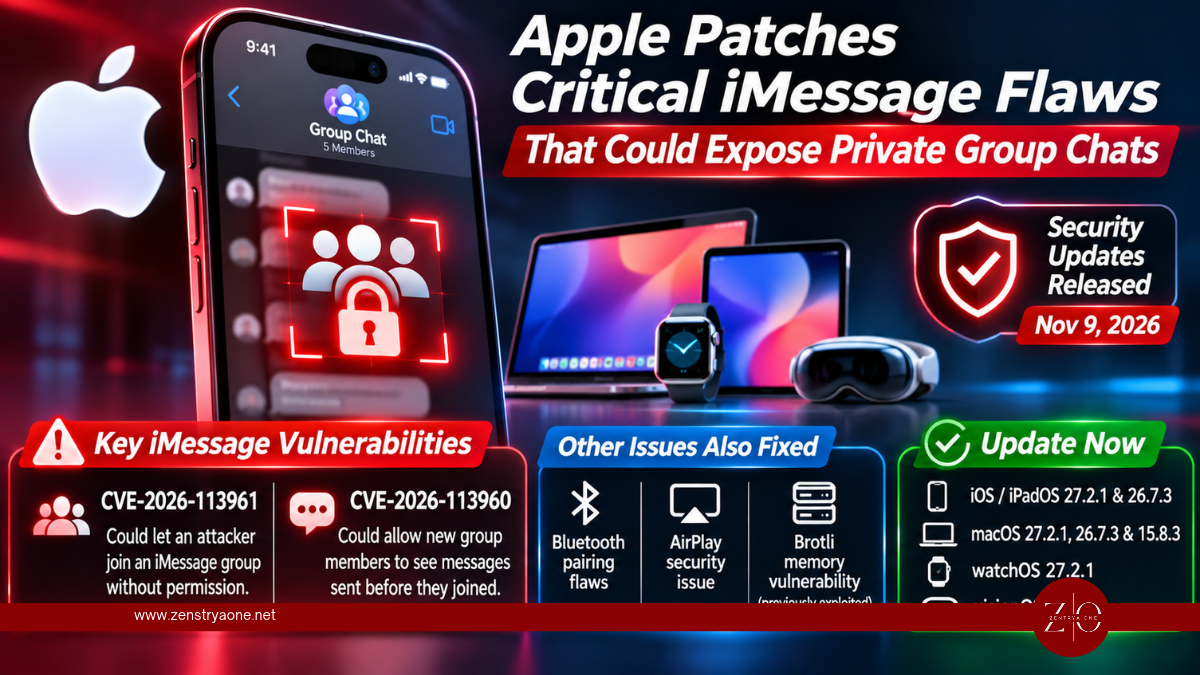
Apple Fixes Critical iMessage Privacy Flaws That Could Expose Private Group Chats
Apple patches two iMessage vulnerabilities that could expose private group chats, alongside Bluetooth, AirPlay and Brotli security flaws.