Critical Atlassian Flaw Lets Unauthenticated Attackers Read Files Across Eight Products
Atlassian patches CVE-2026-21589, a critical CVSS 9.3 flaw allowing unauthenticated attackers to access known files across Jira, Confluence, Bitbucket and five other Data Center products.
Atlassian has disclosed a critical arbitrary file access vulnerability affecting eight of its self-hosted Data Center products, including Jira, Confluence and Bitbucket.
Tracked as CVE-2026-21589, the vulnerability carries a CVSS v4.0 score of 9.3 and can be exploited remotely without authentication or user interaction.
CVE-2026-21589 at a Glance
| Detail | Information |
|---|---|
| CVE | CVE-2026-21589 |
| Severity | Critical |
| CVSS | 9.3 |
| Vulnerability | Arbitrary File Access / Path Traversal |
| Authentication | Not required |
| User Interaction | Not required |
| Main Impact | Unauthorized file disclosure |
| Directory Listing | Not possible |
| Cloud Customers | Already patched |
Atlassian disclosed the vulnerability on October 5, 2026, warning Data Center customers that immediate action is required.
How the Attack Works
The vulnerability allows an attacker to access specific files located within an affected product's web application root directory.
However, exploitation has an important limitation: the attacker must already know the exact filename and path of the file they want to retrieve.
CVE-2026-21589 does not allow attackers to simply enumerate directories and discover every available file.
A simplified attack path is:
Internet-Exposed Atlassian Server → Crafted Request → Path Traversal → Known File Accessed → Potential Sensitive Data Exposure
The impact can become more serious when sensitive configuration or application files are stored within accessible locations.
Eight Atlassian Products Affected
The vulnerability affects all versions prior to the applicable fixed releases of:
- Bitbucket Data Center
- Confluence Data Center
- Jira Software Data Center
- Jira Service Management Data Center
- Bamboo Data Center
- Crowd Data Center
- Crucible
- Fisheye
Atlassian recommends upgrading to a fixed Long Term Support version or later.
| Product | Fixed Versions |
|---|---|
| Bitbucket Data Center | 9.4.26, 10.2.8, 10.5.1 |
| Confluence Data Center | 9.2.26, 10.2.19 |
| Jira Software Data Center | 9.12.40, 10.3.26, 11.3.12 |
| Jira Service Management Data Center | 5.12.40, 10.3.26, 11.3.12 |
| Bamboo Data Center | 10.2.24, 12.1.12 |
| Crowd Data Center | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible | 4.9.15 |
| Fisheye | 4.9.15 |
Atlassian advises customers to move to the appropriate fixed version or a newer supported release.
Atlassian Cloud Customers Already Protected
The issue primarily requires action from organizations operating self-hosted Atlassian Data Center environments.
Atlassian says affected Cloud products have already been patched, and Cloud customers do not need to take additional action.
The company's investigation has also found no evidence of exploitation affecting its Cloud products.
What If You Cannot Patch Immediately?
Atlassian recommends temporarily removing affected instances from the internet if an immediate upgrade is not possible.
This recommendation applies even when an internet-facing instance requires users to authenticate, because CVE-2026-21589 itself does not require authentication.
Atlassian has also provided temporary blocking rules for WAFs, reverse proxies and certain affected products. These mitigations target suspicious path-traversal requests, but the company stresses that they are not replacements for patching.
Hunt for Previous Exploitation Attempts
Organizations should also review historical access logs rather than assuming that installing the update means the environment was never targeted.
Atlassian recommends searching requests for suspicious path-traversal patterns, including encoded versions of traversal sequences. However, the company says it cannot confirm whether individual customer instances have previously been affected.
Security teams should therefore prioritize:
Patch → Restrict Internet Exposure → Review Access Logs → Investigate Suspicious Requests → Assess Potential Data Exposure
Security Takeaway
CVE-2026-21589 is particularly important because an attacker does not need credentials to attempt exploitation against an exposed vulnerable instance.
However, it should not be described as remote code execution.
The demonstrated security impact is unauthorized access to specifically known files:
Unauthenticated Request → Path Traversal → Known File Retrieved → Potential Sensitive Information Exposure
Organizations operating Jira, Confluence, Bitbucket or the other affected Atlassian Data Center products should treat the update as an immediate priority, especially when those systems are accessible from the public internet.
Related reporting
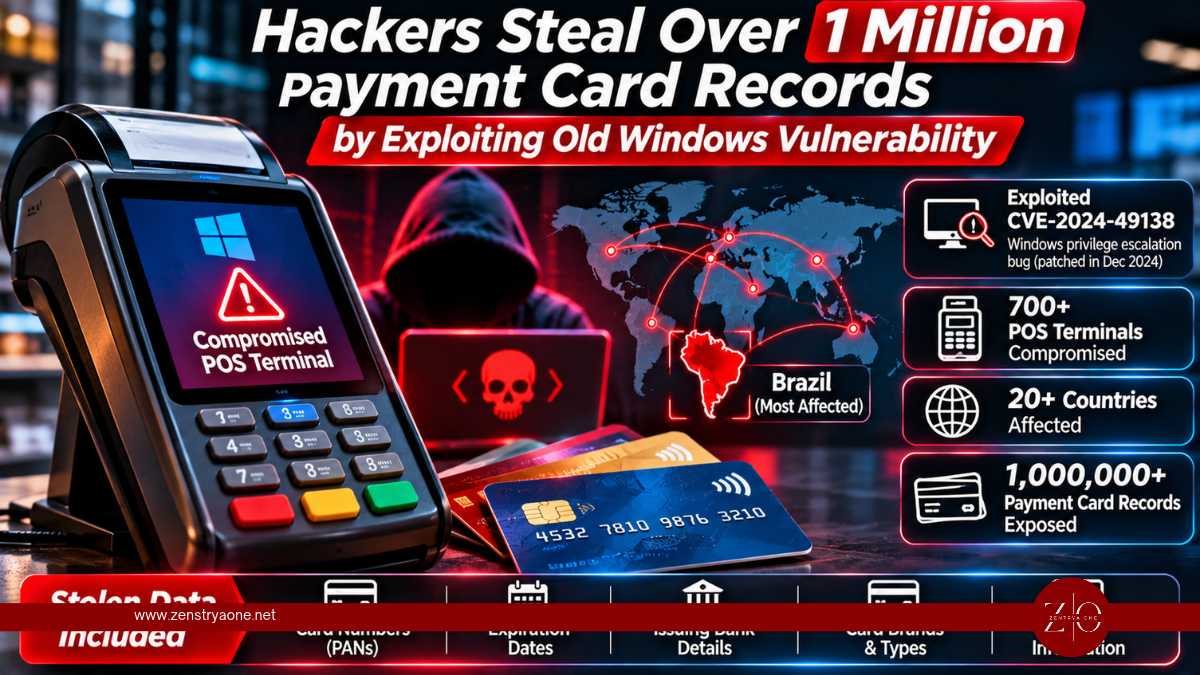
Hackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability
Hackers exploit Windows CVE-2024-49138 to compromise over 700 POS terminals across 20 countries, stealing more than one million payment card records.
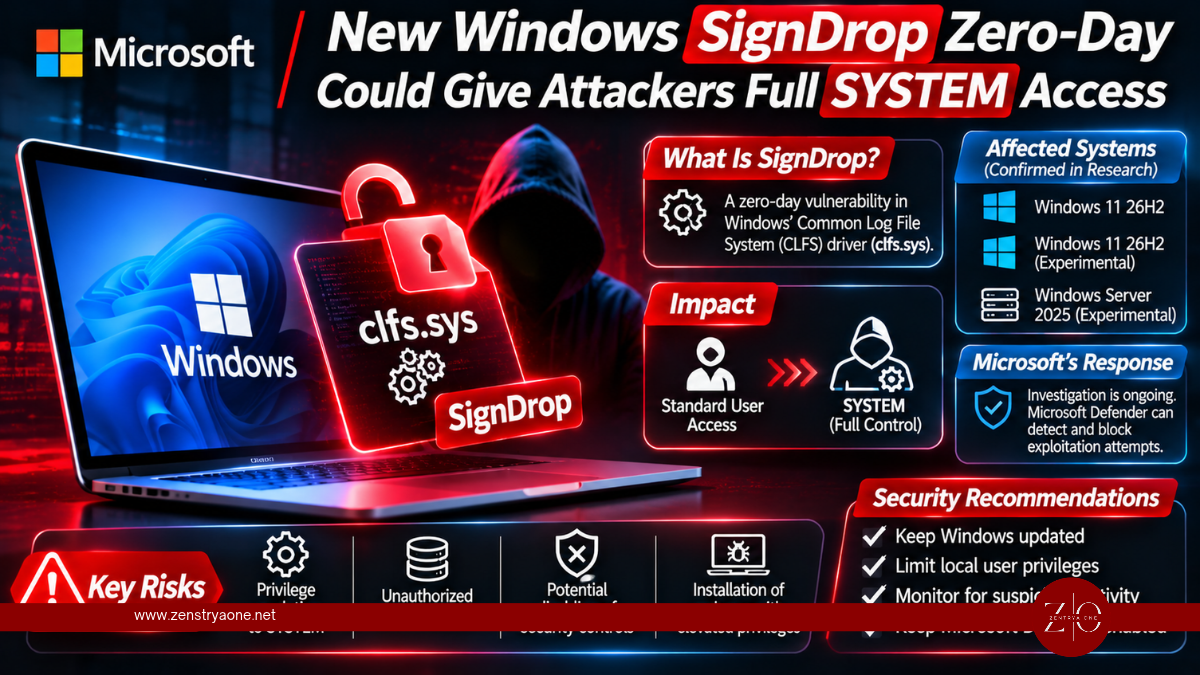
New Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access
New Windows SignDrop zero-day exploit abuses Microsoft CLFS security protections to gain SYSTEM privileges. Learn about affected systems and mitigation.
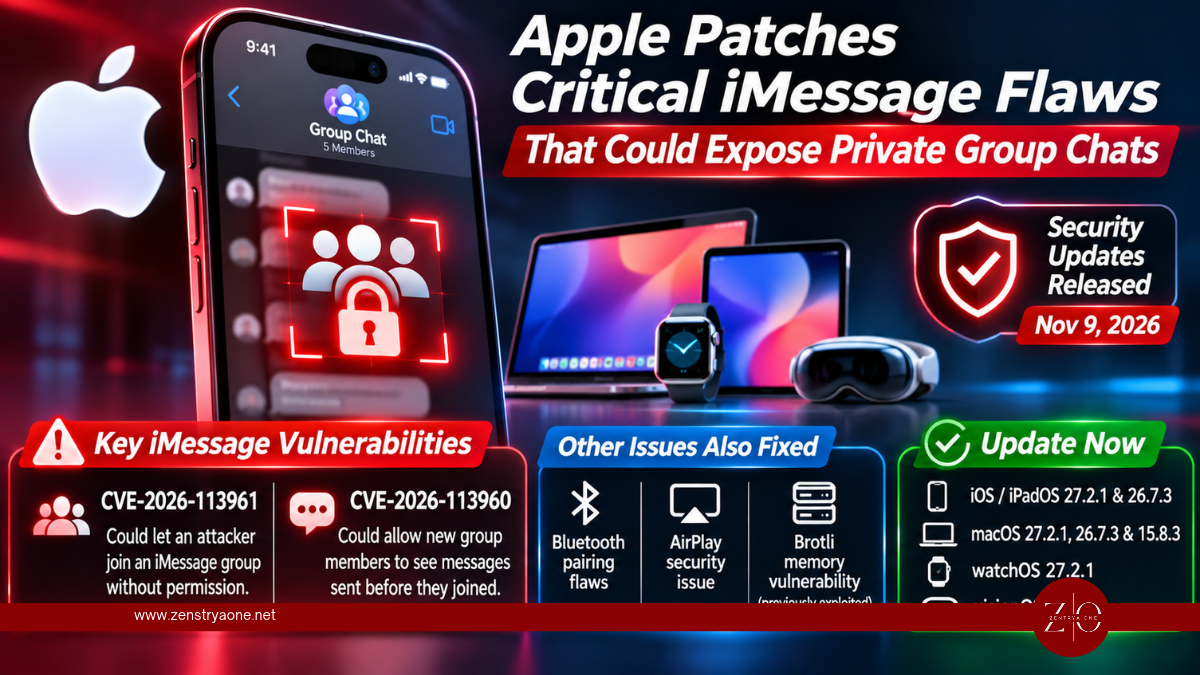
Apple Fixes Critical iMessage Privacy Flaws That Could Expose Private Group Chats
Apple patches two iMessage vulnerabilities that could expose private group chats, alongside Bluetooth, AirPlay and Brotli security flaws.