U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks
The FBI seized domains linked to NightmareStresser, a major DDoS-for-hire service blamed for hundreds of thousands of actual or attempted attacks worldwide since 2022.
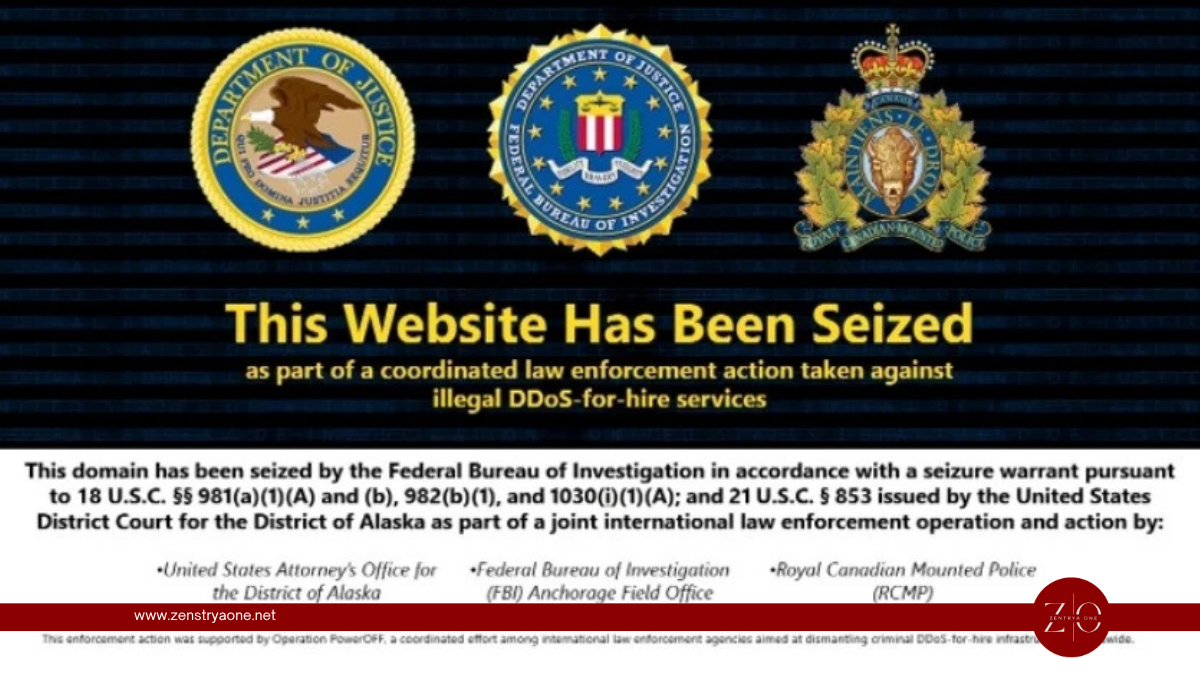
U.S. authorities have disrupted NightmareStresser, one of the world's longest-running distributed denial-of-service (DDoS)-for-hire platforms, seizing domains associated with a service allegedly responsible for hundreds of thousands of attacks and attempted attacks worldwide.
The U.S. Department of Justice (DOJ) announced the court-authorized operation on September 15, 2026, with the Federal Bureau of Investigation (FBI) taking control of domains used by the service.
The operation was conducted with support from the Royal Canadian Mounted Police (RCMP) and forms part of Operation PowerOFF, an ongoing international law-enforcement effort targeting criminal DDoS-for-hire infrastructure.
NightmareStresser at a Glance
| Detail | Information |
|---|---|
| Service | NightmareStresser |
| Type | DDoS-for-hire / booter / stresser |
| Domains targeted | nightmare-stresser[.]com, nightmarestresser[.]org |
| Enforcement | FBI / U.S. Department of Justice |
| International Partner | Royal Canadian Mounted Police |
| Operation | Operation PowerOFF |
| Activity cited by DOJ | Since 2022 |
| Estimated attacks | Hundreds of thousands of actual or attempted DDoS attacks |
| Reported targets | Education, government, gaming and other online services |
| Status | Domains seized |
What Was NightmareStresser?
NightmareStresser operated as a so-called booter or stresser service.
These platforms are commonly advertised as tools that customers can use to stress-test their own servers and networks.
However, authorities say services such as NightmareStresser lower the technical barrier to conducting unauthorized DDoS attacks by allowing customers to pay for attack capabilities rather than building their own infrastructure.
A DDoS attack attempts to overwhelm a target with traffic or requests until legitimate users can no longer access the service.
The basic model is:
Customer selects target
↓
DDoS infrastructure generates attack traffic
↓
Target receives overwhelming traffic
↓
Resources become exhausted
↓
Legitimate users experience disruption or outage
This turns DDoS capability into an easily accessible service.
Hundreds of Thousands of Attacks Since 2022
According to the DOJ, NightmareStresser was used to conduct hundreds of thousands of actual or attempted DDoS attacks against victims worldwide since 2022.
Authorities identified targets across sectors including:
- Educational institutions
- Government agencies
- Gaming platforms
- Online services
- Individual internet users
The scale of the operation highlights how DDoS-for-hire platforms can allow relatively inexperienced attackers to generate significant disruption without operating their own large attack infrastructure.
More Than 566,000 Registered Users Reported
Earlier research published by Searchlight Cyber in 2023 indicated that NightmareStresser had grown into a substantial operation.
Researchers identified more than 566,000 registered users and 52 servers associated with the service.
The platform reportedly supported 28 attack methods and advertised attack capacity reaching approximately 200 Gbps.
Customers could select a target IP address or URL, specify ports and launch attacks against different layers of network infrastructure.
Reported subscription prices ranged from roughly €25 to €19,999, depending on attack duration, concurrency and other capabilities.
These historical figures provide an indication of the scale NightmareStresser had reached, but they should not be interpreted as meaning every registered account was actively conducting attacks.
Layer 4 and Layer 7 Attacks
NightmareStresser reportedly offered attacks targeting multiple layers of internet infrastructure.
Layer 4 Attacks
Transport-layer attacks typically attempt to overwhelm networking resources using protocols such as:
- TCP
- UDP
The objective may be to consume bandwidth, connection tables or other networking resources.
Layer 7 Attacks
Application-layer attacks instead target services such as websites and APIs.
Rather than simply generating large volumes of network traffic, these attacks can generate large numbers of apparently legitimate application requests.
This can consume:
- Web server resources
- Application processing capacity
- Database connections
- API resources
- Backend infrastructure
Supporting multiple attack types makes a DDoS-for-hire service capable of targeting a wider range of systems.
Two Domains Seized
The enforcement action targeted two domains associated with NightmareStresser:
nightmare-stresser[.]com
and
nightmarestresser[.]org
Visitors to the seized infrastructure are now presented with a law-enforcement seizure notice.
The banner states that the websites were seized as part of coordinated law-enforcement action against illegal DDoS-for-hire services.
Taking control of the domains disrupts an important part of the service's customer-facing infrastructure, making it harder for operators and customers to continue using the platform through those addresses.
NightmareStresser Had Already Been Targeted Before
This is not the first time U.S. authorities have targeted NightmareStresser infrastructure.
In December 2022, nightmarestresser[.]com was among 48 domains seized by the DOJ during an earlier crackdown on DDoS-for-hire services.
The platform's continued presence after that action illustrates one of the difficulties associated with disrupting cybercrime-as-a-service operations.
Taking down a domain does not necessarily eliminate:
- Backend infrastructure
- Administrators
- Customer databases
- Payment systems
- Attack servers
- Botnets
- Communication channels
- Alternative domains
Operators can potentially move to new infrastructure unless authorities also disrupt the broader ecosystem supporting the service.
Operation PowerOFF
The latest seizure forms part of Operation PowerOFF, an international initiative focused on disrupting DDoS-for-hire services and pursuing their operators and users.
Operation PowerOFF brings together law-enforcement agencies from multiple countries to target the infrastructure behind booter and stresser services.
The initiative has involved:
- Domain seizures
- Infrastructure disruption
- Search warrants
- Arrests
- Criminal charges
- Identification of service users
- Public-awareness campaigns
The DOJ says investigations conducted by prosecutors and investigators in Anchorage and Los Angeles over the past eight years have resulted in charges against 12 defendants accused of facilitating DDoS-for-hire services and the seizure of more than 100 related internet domains.
Earlier Operation PowerOFF Action Hit 53 Domains
The NightmareStresser seizure follows another significant Operation PowerOFF action earlier in 2026.
In April, authorities disrupted 53 domains associated with commercial DDoS services, while four people were arrested in connection with related operations.
European authorities said approximately 75,000 users of the targeted services had been identified during that operation.
The continued enforcement activity indicates that authorities are targeting both the operators supplying DDoS services and the broader ecosystem supporting them.
DDoS-as-a-Service Lowers the Barrier to Cybercrime
Operating a large-scale DDoS campaign traditionally required considerable infrastructure and technical expertise.
An attacker might need access to:
Compromised devices
↓
Command-and-control infrastructure
↓
Attack scripts
↓
Traffic-generation capabilities
↓
Infrastructure capable of coordinating attacks
DDoS-for-hire platforms change this model.
The customer may only need to:
Create account
↓
Purchase subscription
↓
Enter target
↓
Select attack parameters
↓
Launch attack
The technical complexity is handled by the service provider.
This cybercrime-as-a-service model significantly lowers the barrier to launching disruptive attacks.
“Stresser” Branding Does Not Make Unauthorized Attacks Legal
Some DDoS services present themselves as legitimate network stress-testing platforms.
There are legitimate reasons for organizations to conduct controlled load and resilience testing against infrastructure they own or have explicit authorization to test.
The distinction is authorization.
Using such infrastructure against a third-party system without permission can constitute criminal activity.
The DOJ specifically warns that booter services are frequently marketed as stress-testing utilities while being used to facilitate attacks against victims in the United States and elsewhere.
DDoS Remains a Significant Business Risk
Although DDoS attacks typically focus on availability rather than directly stealing information, their business impact can still be substantial.
Successful attacks can cause:
- Website outages
- API disruption
- Gaming-service interruptions
- Customer-access failures
- Payment-service disruption
- Operational downtime
- Lost revenue
- Increased infrastructure costs
- Reputational damage
DDoS attacks may also be used alongside other malicious activity.
For example, defenders occupied with an availability incident may have less visibility into unrelated intrusion activity occurring elsewhere in the environment.
Organizations should therefore avoid treating DDoS solely as a bandwidth-management issue.
Defensive Measures Against DDoS Attacks
Organizations operating public-facing infrastructure should maintain layered DDoS defenses.
Important controls include:
- DDoS mitigation services
- Content delivery networks
- Web application firewalls
- Rate limiting
- Traffic filtering
- Anycast infrastructure
- Network-level anomaly detection
- Application-layer request monitoring
- Upstream ISP coordination
- Autoscaling where appropriate
- Tested incident-response procedures
Organizations should also establish baseline traffic patterns so abnormal spikes can be identified quickly.
Prepare Before an Attack Happens
DDoS response planning should happen before an outage begins.
Security and infrastructure teams should know:
Who contacts the ISP?
Who activates the DDoS provider?
Who manages DNS changes?
Who communicates with customers?
Who preserves attack telemetry?
Who coordinates with law enforcement?
These decisions become much harder to make when production services are already unavailable.
Organizations should periodically test their DDoS response procedures and verify that mitigation providers can handle expected attack scenarios.
Security Takeaway
The seizure of NightmareStresser demonstrates the continuing international effort to dismantle the infrastructure supporting DDoS-as-a-Service operations.
According to U.S. authorities, NightmareStresser facilitated hundreds of thousands of actual or attempted attacks worldwide since 2022, targeting educational institutions, government agencies, gaming platforms and other victims.
Historical research also illustrates the platform's scale, with more than 566,000 registered users, 52 servers and dozens of available attack methods identified in 2023.
The latest operation can be summarized as:
DDoS-for-Hire Platform
→ Hundreds of Thousands of Attacks/Attempts
→ International Investigation
→ Court-Authorized Seizure
→ NightmareStresser Domains Taken Offline
→ Operation PowerOFF Continues
However, a domain seizure should not automatically be interpreted as destruction of every technical component behind the operation.
The DOJ announcement focuses on the seizure of NightmareStresser's domains and does not establish that every backend attack server, botnet or related piece of infrastructure has been eliminated.
For defenders, the broader lesson remains unchanged: DDoS capabilities have become commoditized, allowing attackers to rent disruptive capacity instead of developing it themselves.
Organizations running critical internet-facing services should therefore combine technical DDoS mitigation with monitoring, incident-response planning and coordination with upstream providers.
Related reporting
Police Disrupt KillSec Ransomware Group and Arrest Suspected 16-Year-Old Operator
International law enforcement disrupts KillSec ransomware in Operation KillSwitch, arresting three suspects including a 16-year-old alleged operator and securing more than 110 TB of data.
Threat Intelligence Alone Cannot Close the Growing Exploitation Gap
Threat intelligence alone cannot stop rapidly evolving cyberattacks. Learn how security validation, risk-based vulnerability management and faster remediation can help organizations close the growing exploitation gap.
KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have uncovered a sophisticated banking-malware campaign that hijacks Google Chrome and Microsoft Edge using malicious browser extensions capable of stealing credentials, cookies, session tokens and other sensitive browser data.