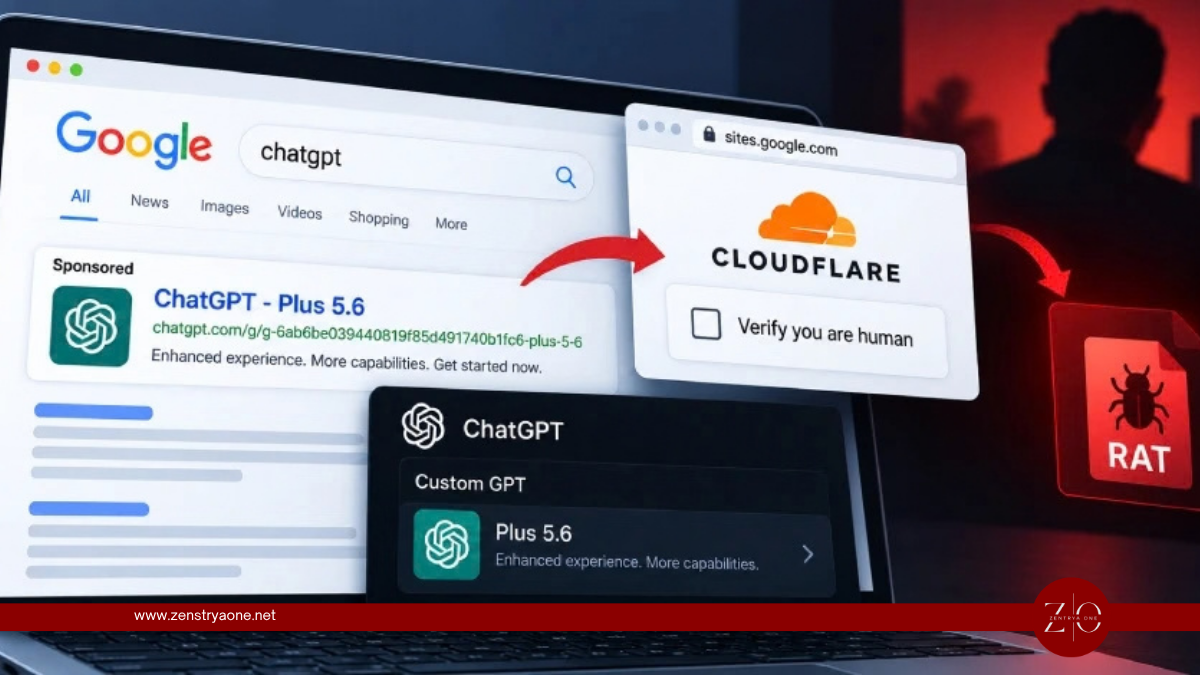
Attackers Abuse ChatGPT Custom GPTs to Deliver RAT Malware via ClickFix
Attackers abuse ChatGPT Custom GPTs and sponsored Google results to redirect victims to ClickFix pages that execute PowerShell and install remote access trojan malware.
Loaders, stealers, ransomware and botnets.
Attackers abuse ChatGPT Custom GPTs and sponsored Google results to redirect victims to ClickFix pages that execute PowerShell and install remote access trojan malware.
Russia-linked Star Blizzard targets more than 100 organizations using fake event invitations, the new RedFlick malware delivery technique and the CosmicPulse Windows backdoor.
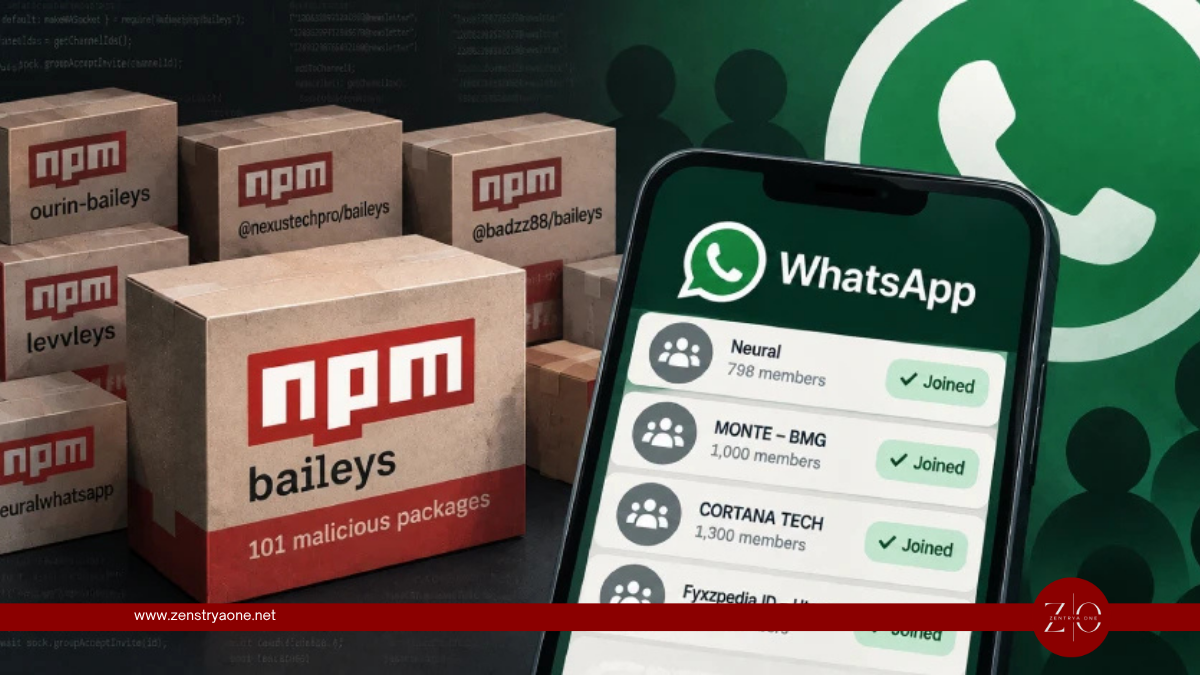
Researchers uncover 101 malicious npm packages in the PhantomSub campaign that abuse authenticated WhatsApp sessions to secretly add developers to attacker-controlled groups and channels.
Researchers uncover malicious Terraform providers and Go modules delivering Graphalgo-linked Go malware using Slack and Ethereum blockchain infrastructure for command and control.
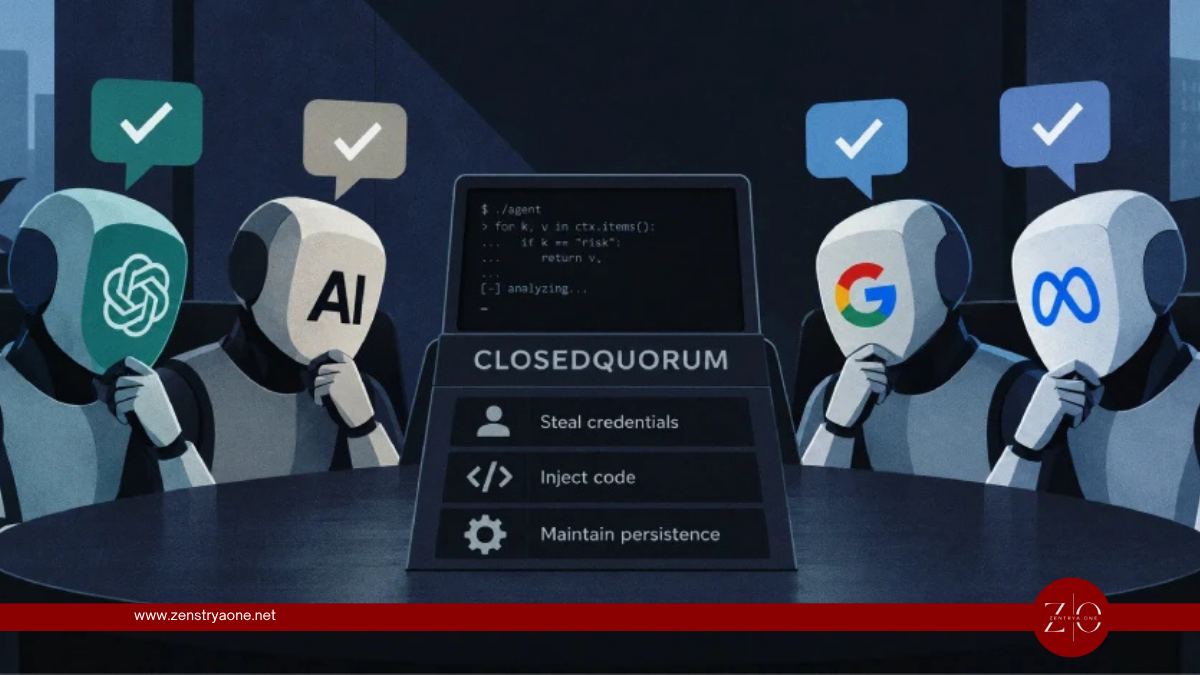
Cisco Talos uncovers CLOSEDQUORUM, experimental Windows malware that lets DeepSeek, Qwen, Mistral and Gemini vote on whether to steal data, inject code or establish persistence.
Compromised MemTensor packages on npm and PyPI deliver the cross-platform sckit credential stealer, targeting GitHub, AWS, SSH, npm, PyPI and developer secrets.
TASK#STOMP is a new PowerShell backdoor that steals business documents, Wi-Fi passwords and clipboard data while using scheduled tasks and dual C2 servers for persistent access.
Researchers uncover ChainScript, a Node.js RAT delivered through ClickFix lures that uses a Polygon smart contract to dynamically locate and rotate its WebSocket C2 infrastructure.
Researchers link Handala Hack to HEAVYGRAM, a Telegram-controlled Windows backdoor capable of stealing passwords, messages, screenshots and other sensitive data.
ESET researchers uncover SparroWocky, a new modular C++ backdoor used by China-aligned FamousSparrow in cyberespionage attacks targeting governments across Latin America.
Kaspersky reports NightEagle, Hacking Cat and Toy Ghouls targeting Russian enterprises with VPN compromise, Exchange attacks, GhostContainer and Gorilla RAT backdoors, ransomware and destructive wipers.
Cybersecurity and intelligence agencies from the United Kingdom, United States and Netherlands have exposed an Iranian state-linked cyber-espionage campaign using sophisticated Windows malware to monitor dissidents, activists and journalists around the world.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.