The Wire
CRITICALJPMorgan Chase, Visa and Mastercard Confirm Third-Party Cyberattacks Exposing Customer Information CRITICALHackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability CRITICALItaly Fines Meta €805 Million Over Facebook's Unauthorized Access to Android Photo Galleries FILEDFBI: North Korean Hackers Steal Over $400 Million in Crypto Through Fake Video Calls FILEDSilentAir Hackers Compromise Asian Telecom Networks to Intercept SMS Verification Codes CRITICALNew Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access CRITICALUber Confirms Data Breach: Hackers Steal Thousands of U.S. Drivers' Personal Records FILEDSri Lanka Restricts Two EY Audit Partners Following Rs. 13.64 Billion NDB Bank Fraud CRITICALJPMorgan Chase, Visa and Mastercard Confirm Third-Party Cyberattacks Exposing Customer Information CRITICALHackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability CRITICALItaly Fines Meta €805 Million Over Facebook's Unauthorized Access to Android Photo Galleries FILEDFBI: North Korean Hackers Steal Over $400 Million in Crypto Through Fake Video Calls FILEDSilentAir Hackers Compromise Asian Telecom Networks to Intercept SMS Verification Codes CRITICALNew Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access CRITICALUber Confirms Data Breach: Hackers Steal Thousands of U.S. Drivers' Personal Records FILEDSri Lanka Restricts Two EY Audit Partners Following Rs. 13.64 Billion NDB Bank Fraud
CyberNews by Zentrya One
Section

Malware

Loaders, stealers, ransomware and botnets.

critical Malware

Russian State-Sponsored Hackers Used Claude to Rebuild Malware After Detection

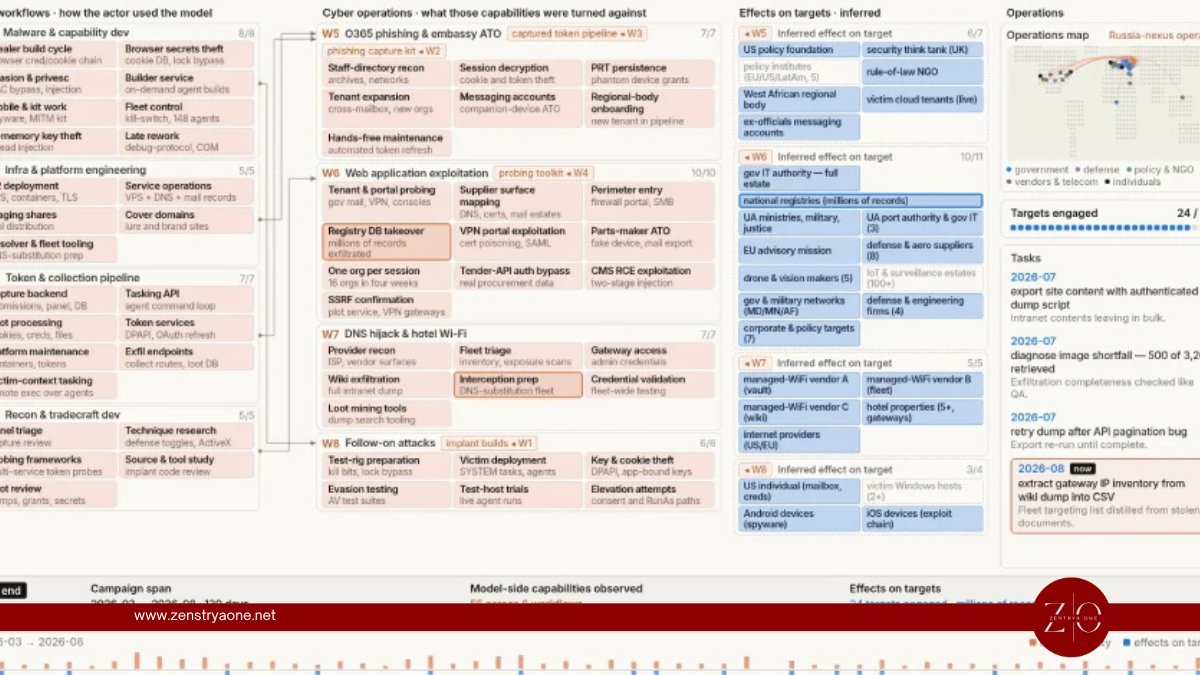
A Russian state-linked cyber-espionage operation has used Anthropic's Claude AI to create an automated malware-evasion workflow capable of detecting when its malicious tools were identified by security products and then modifying and rebuilding those tools to bypass the detections.

critical Malware

Cisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin Ransomware

Threat actors are exploiting vulnerabilities in Cisco Secure Firewall Management Center (FMC) to gain access to enterprise environments, steal credentials and ultimately deploy Qilin ransomware, turning vulnerable security infrastructure into an entry point for broader network compromise.

Malware

Infostealer Logs Reveal Stolen AI Session Tokens Capable of Bypassing MFA

Cybercriminals are increasingly targeting artificial intelligence accounts by stealing browser session tokens and API credentials from infected devices. These stolen artifacts may allow attackers to access AI services without entering a username, password, or multi-factor authentication (MFA) code.

critical CVE-2025-53521 Malware

F5 BIG-IP APM Malware Hides Web Shell in Apache Memory to Evade Disk Scans

Security researchers have uncovered a sophisticated malware implant targeting F5 BIG-IP Access Policy Manager (APM) appliances that can conceal a PHP web shell entirely within Apache process memory, allowing attackers to maintain server-side code execution while leaving the targeted PHP files on disk unchanged.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.