F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE
F5 patches CVE-2026-94127, a critical CVSS 9.8 BIG-IP APM zero-day actively exploited to achieve unauthenticated remote code execution on OAuth authorization servers.
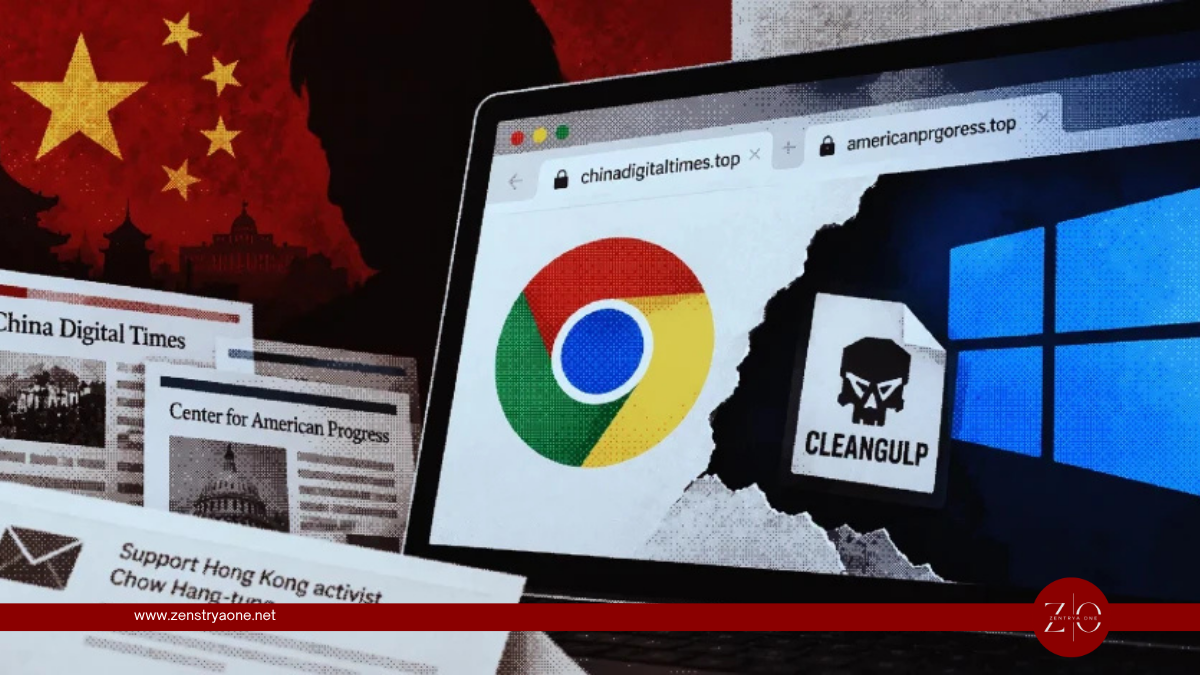
China-linked UTA0565 exploited Chrome and Windows zero-days through fake websites to deploy CLEANGULP, a new backdoor supporting commands, file theft and BOF execution.
Critical Next.js vulnerability CVE-2026-94545, rated CVSS 9.5, could allow unauthenticated remote code execution through crafted input passed to Node.js ImageResponse.
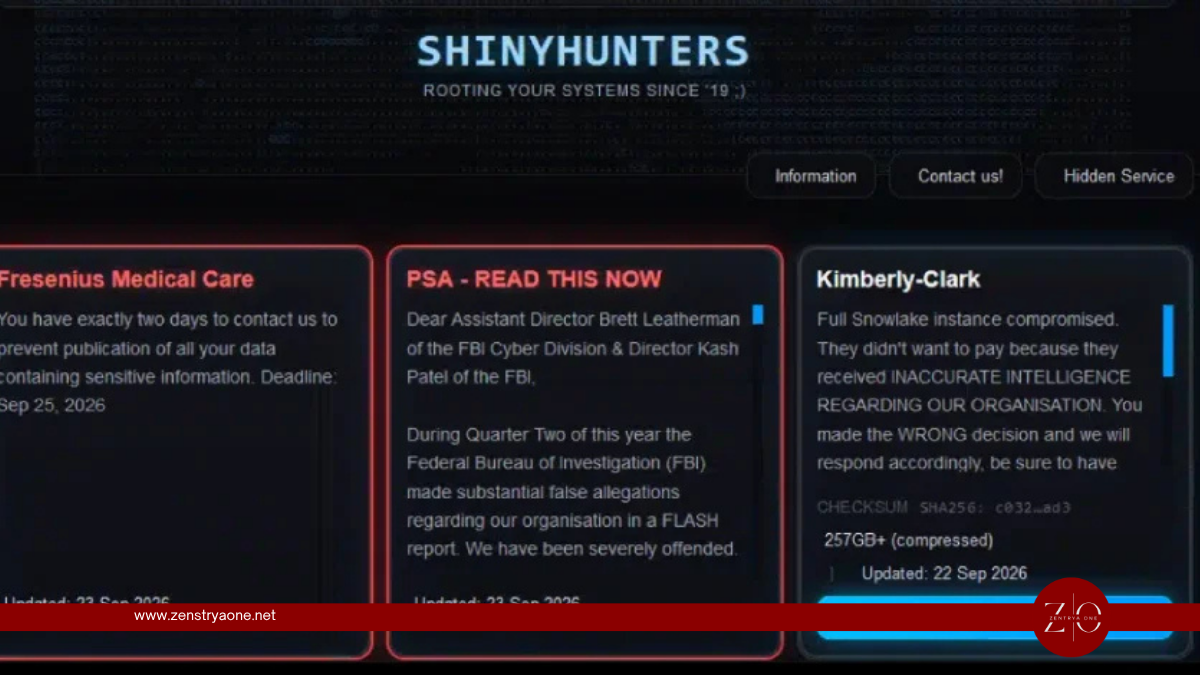
ShinyHunters claims it breached FBI systems and stole sensitive data on agents, employees and job applicants, while the FBI investigates unauthorized activity affecting FBIJobs.gov.
This week's cybersecurity recap covers an exploited Cisco ISE zero-day, AI-agent RCE risks, surging ClickFix attacks, ChainScript malware, browser hijacking and software supply-chain threats.
TASK#STOMP is a new PowerShell backdoor that steals business documents, Wi-Fi passwords and clipboard data while using scheduled tasks and dual C2 servers for persistent access.
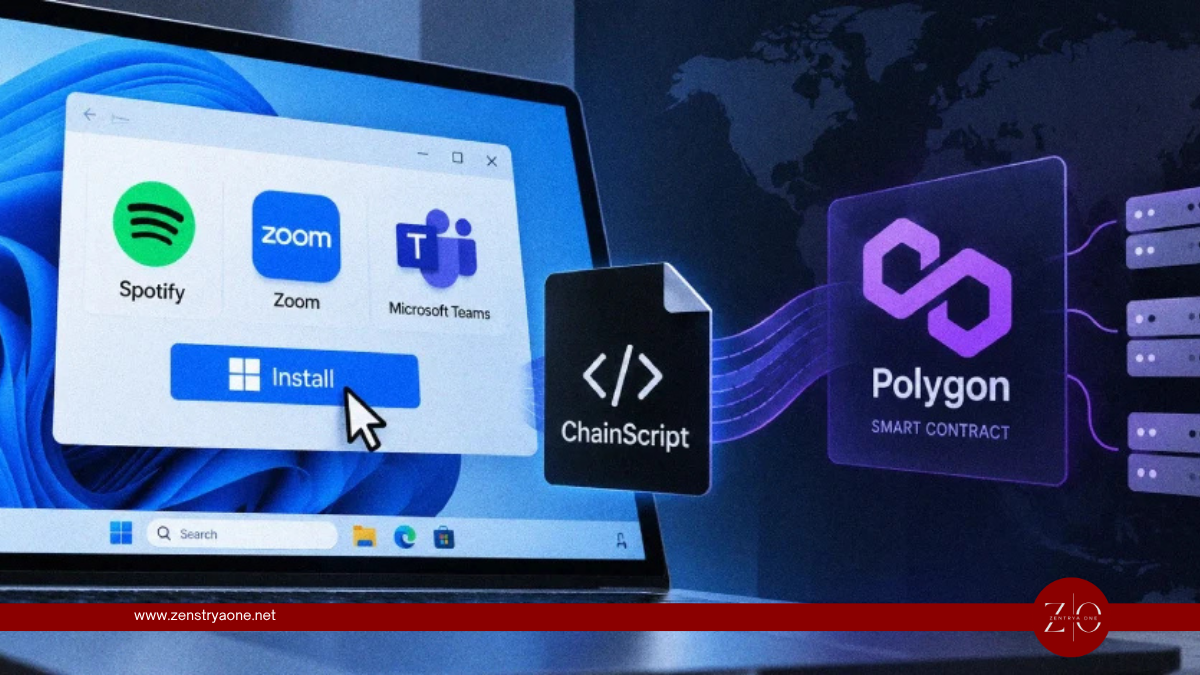
Researchers uncover ChainScript, a Node.js RAT delivered through ClickFix lures that uses a Polygon smart contract to dynamically locate and rotate its WebSocket C2 infrastructure.
Researchers link Handala Hack to HEAVYGRAM, a Telegram-controlled Windows backdoor capable of stealing passwords, messages, screenshots and other sensitive data.
NLnet Labs patches critical Unbound vulnerability CVE-2026-81642, a CVSS 9.1 DNSSEC validator heap overflow that could cause denial of service or potentially enable remote code execution.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.