As organizations rapidly integrate generative AI and AI agents into everyday workflows, Security Operations Centers (SOCs) are facing a new challenge: AI itself is becoming a major source of security alerts.
GitLab has patched a maximum-severity path traversal vulnerability that can allow unauthenticated attackers to read arbitrary files from vulnerable GitLab servers.
Anthropic says it identified and disrupted seven industrial-scale attempts to extract capabilities from its Claude AI models, attributing the activity to China-based AI laboratories.
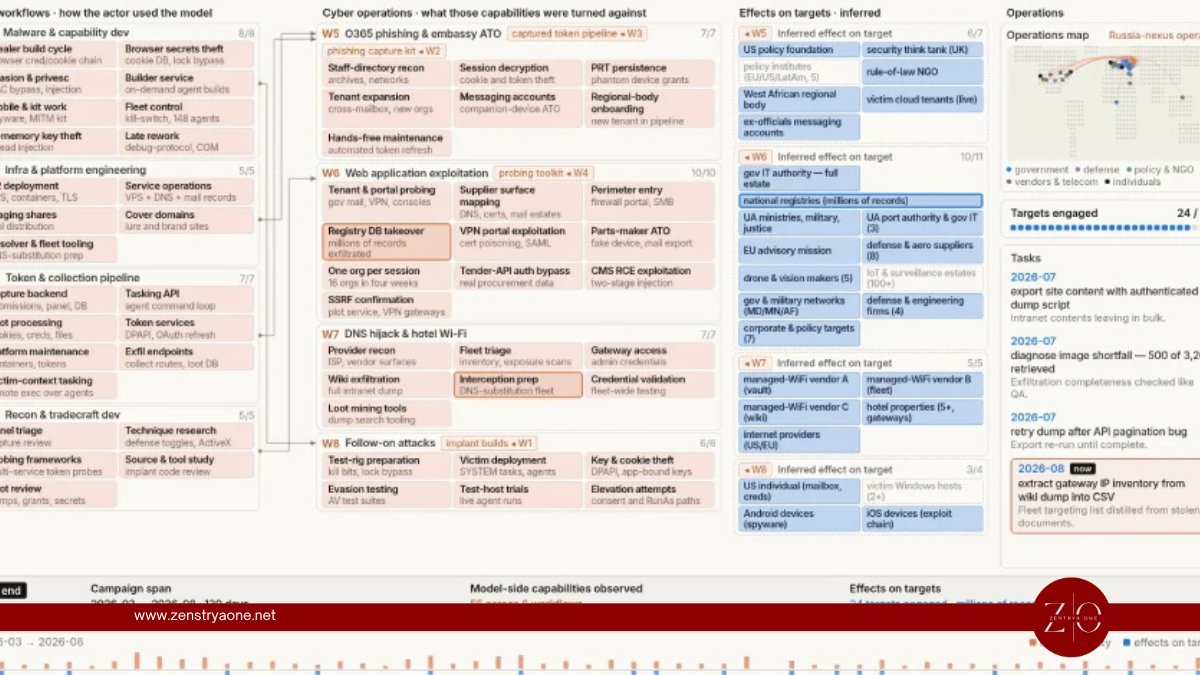
Cybercriminals and state-sponsored threat actors are increasingly using artificial intelligence to automate portions of real-world cyberattacks, with Anthropic revealing that its Claude models were incorporated into multi-stage operations involving reconnaissance, exploitation, credential theft and data exfiltration.
A Russian state-linked cyber-espionage operation has used Anthropic's Claude AI to create an automated malware-evasion workflow capable of detecting when its malicious tools were identified by security products and then modifying and rebuilding those tools to bypass the detections.
Attackers have been actively exploiting vulnerabilities in self-hosted JFrog Artifactory deployments to obtain administrator privileges, create persistent accounts, execute commands and install backdoors, raising serious concerns for organizations that rely on Artifactory as a central component of their software supply chains.
A China-linked threat actor tracked as UNC3569 has exploited a newly disclosed vulnerability in Sogou Input Method for Windows to compromise systems and deploy the GRAYRABBIT backdoor, according to research from Gen Threat Labs.
PaperCut has released new regular maintenance updates for its PaperCut NG and PaperCut MF print-management platforms, replacing the emergency patches previously issued to address two vulnerabilities that have been actively exploited in the wild.
Zentrya One Desk6d ago6 min read
The Daily Brief
Stay informed. Stay prepared. Stay one step ahead.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.