A joint U.S. advisory alleges DeepSeek, Alibaba, Moonshot AI and others have pulled billions of tokens out of Claude, GPT, Gemini and Grok since late 2024 to shortcut their own model training.
Google confirms attackers are already abusing CVE-2026-87491, a memory-corruption bug in Chrome's JavaScript engine that can be triggered by simply loading a booby-trapped web page.
cPanel has patched a security vulnerability that could allow an authenticated hosting account with mail-related privileges to take complete control of the underlying server.
Security researchers have uncovered a sophisticated malware implant targeting F5 BIG-IP Access Policy Manager (APM) appliances that can conceal a PHP web shell entirely within Apache process memory, allowing attackers to maintain server-side code execution while leaving the targeted PHP files on disk unchanged.
SAP has released its September 2026 security updates, addressing multiple vulnerabilities across its enterprise software portfolio, including a maximum-severity flaw in the SAP Kernel that could allow unauthenticated attackers to remotely execute operating-system commands.
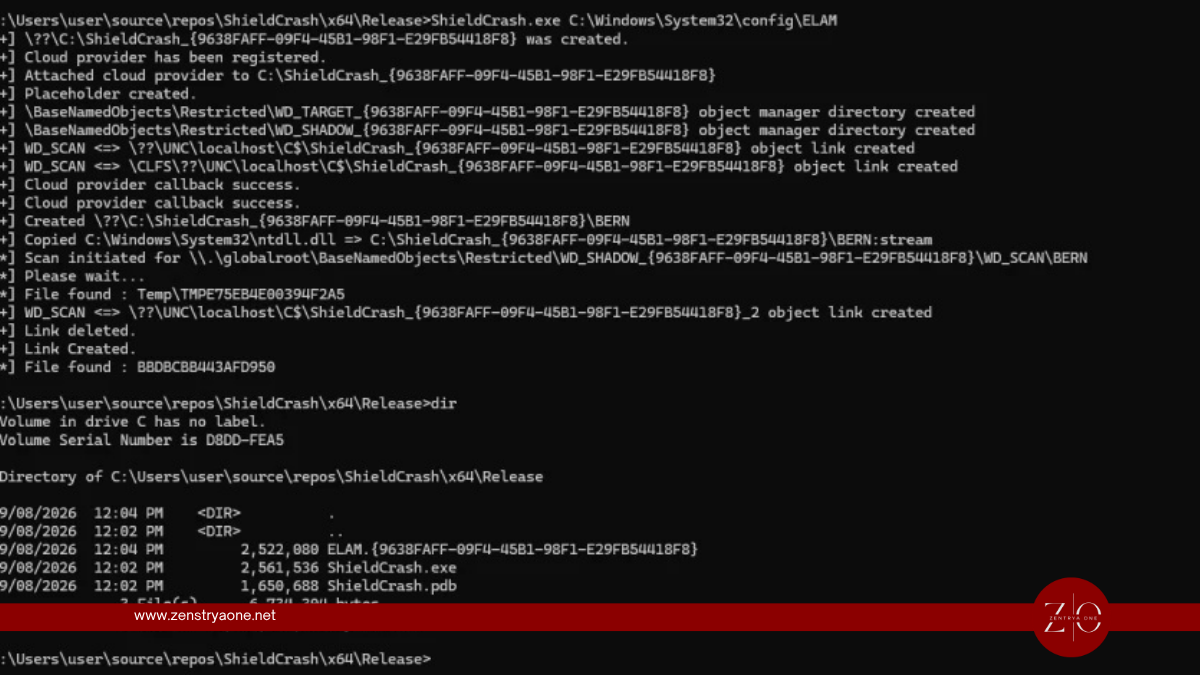
A security researcher has released a new proof-of-concept (PoC) demonstrating that Microsoft's recent fix for a Microsoft Defender vulnerability known as **ShieldBreak** can reportedly be bypassed.
Microsoft has delivered the largest security update in the history of its Patch Tuesday program, addressing 974 vulnerabilities across Windows, Office, SQL Server, Developer Tools, Exchange, SharePoint, Azure and other products.
A maximum-severity vulnerability in **N-able N-central**, a remote monitoring and management (RMM) platform widely used by managed service providers (MSPs) and IT teams, is now being exploited in the wild.
Zentrya One Desk09 Sept 20268 min read
The Daily Brief
Stay informed. Stay prepared. Stay one step ahead.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.