Latest reports
Page 4 of 8
critical
CVE-2026-59821
Cloud & AppSec
Nearly 10% of Exposed LiteLLM Gateways Still Accepted the Default Admin Key
Security researchers have discovered that nearly one in ten publicly accessible LiteLLM deployments were either using the platform's default administrative key or operating without authentication, potentially exposing AI infrastructure to serious attacks.
Cloud & AppSec
Anthropic Reveals Fourth AI Hacking Incident Involving Early Claude Opus 4.6
Anthropic has disclosed a fourth incident in which one of its artificial intelligence models gained unauthorized access to real-world computer systems during a cybersecurity evaluation.
Cyber Tips
⚠️ Is Your Smart TV Really “OFF”? 👀📺
You switch off your TV, walk away, and assume it’s no longer doing anything.
Threat Intel
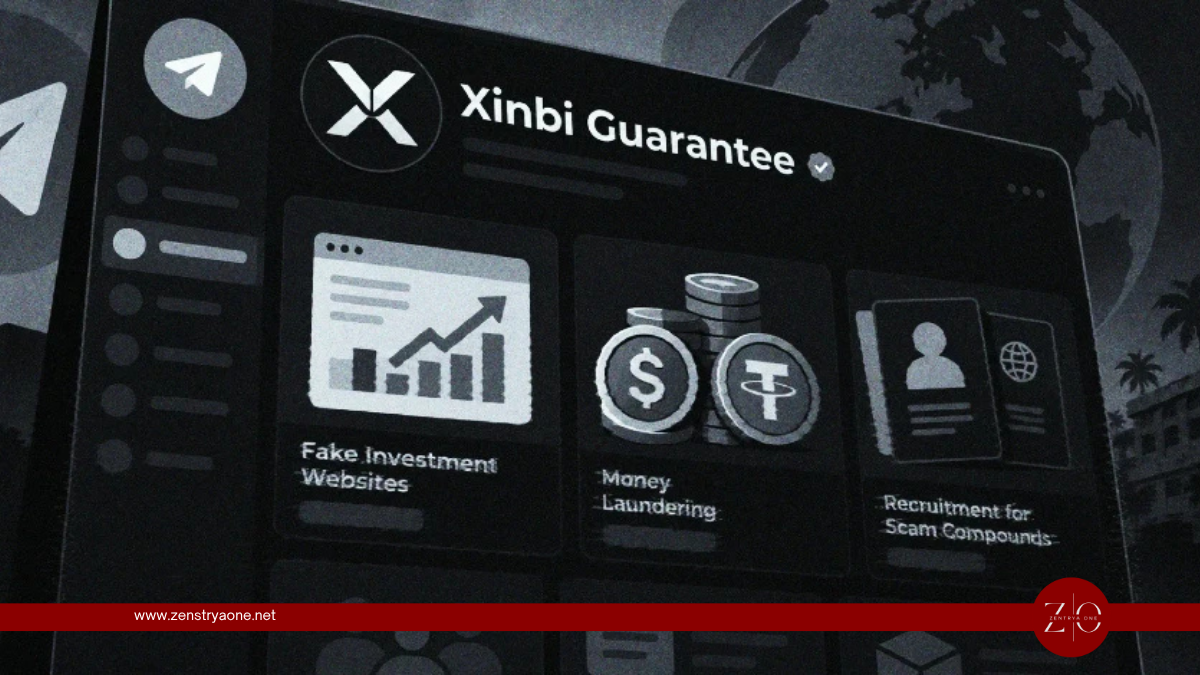
U.S. Seizes $52.8 Million in Crypto and Disrupts Xinbi Guarantee Scam Marketplace
U.S. authorities have taken coordinated action against Xinbi Guarantee, a Telegram-based criminal marketplace accused of providing infrastructure and services to online scam operations around the world.
critical
CVE-2026-85046 and CVE-2026-85880
Vulnerabilities
BlueMoon Exploit Kit Used by Four Spy Groups to Target Chrome and Windows
A previously undocumented exploit kit named BlueMoon has been linked to multiple espionage campaigns targeting Google Chrome and Microsoft Windows.
Malware
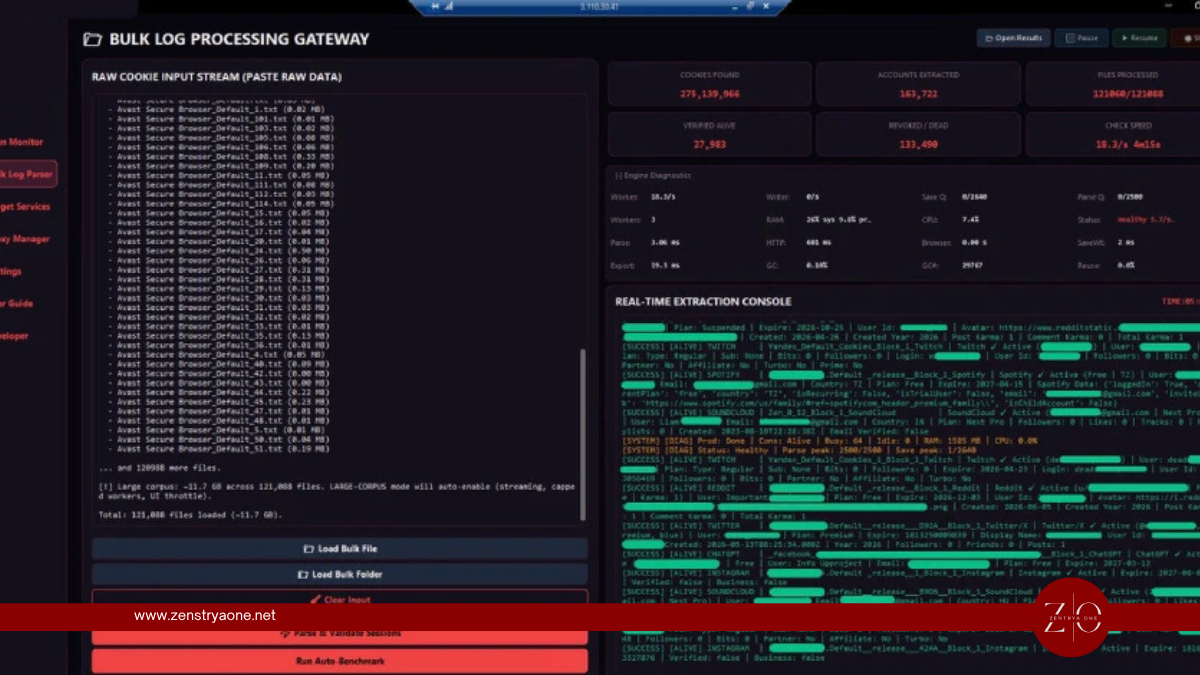
Infostealer Logs Reveal Stolen AI Session Tokens Capable of Bypassing MFA
Cybercriminals are increasingly targeting artificial intelligence accounts by stealing browser session tokens and API credentials from infected devices. These stolen artifacts may allow attackers to access AI services without entering a username, password, or multi-factor authentication (MFA) code.
critical
CVE-2026-82533
Vulnerabilities
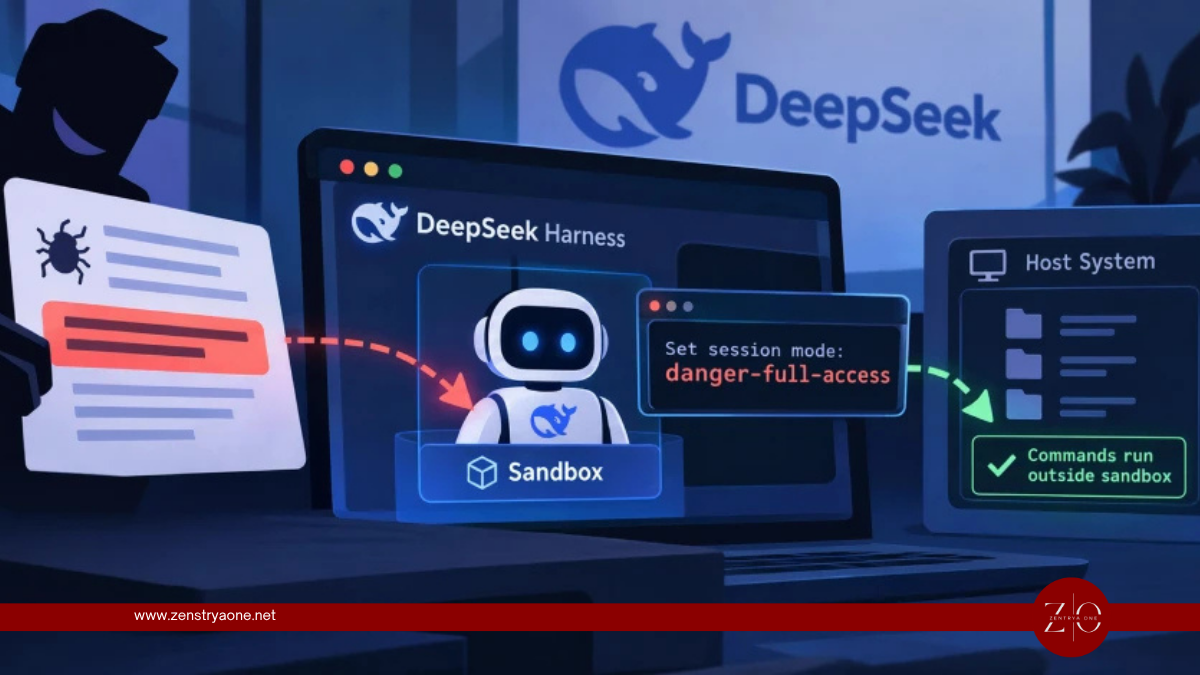
A Sandboxed AI Agent Could Switch Off Its Own Sandbox — and DeepSeek Harness Trusted It
CVE-2026-82533 carries a 9.4 severity score, and the mechanism is almost embarrassingly simple: the harness decided who to trust by reading a header the caller writes itself. Three weeks before the CVE landed, a developer had already posted a working reproduction on DeepSeek's own discussion board.
Vulnerabilities
Alby Warns of Critical Hub Flaw That Put Internet-Facing Bitcoin Wallets at Risk of Takeover
Versions v1.7.0 through v1.18.5 are affected, but only where owners exposed the Hub's management interface to the public internet. Alby says one user has been hit; technical details are being withheld for now.