 Live
critical
CVE-2026-5430
Vulnerabilities
Hackers Exploit Critical WSO2 API Manager JWT Flaw Using Forged Admin Tokens
Security researchers have detected active exploitation attempts targeting a critical authentication-bypass vulnerability in WSO2 API Manager, with attackers sending forged JSON Web Tokens (JWTs) containing administrator privileges.
Iran-Linked Hackers Use Telegram-Controlled Malware to Spy on Dissidents and Journalists
Nintendo Switch Vulnerability Lets Nearby Attackers Run Unauthorized Code via QR Code Feature
UK Government Begins Moving 23 Million Users Away From Passwords With Passkeys
Latest reports
Page 1 of 8

critical
CVE-2026-85046, CVE-2026-87491 and CVE-2
Vulnerabilities
China-Linked Hackers Chain Chrome and Windows Zero-Days to Deploy GRIMWEDGE Backdoor
China-linked threat actors have been observed chaining multiple vulnerabilities in Google Chrome and Microsoft Windows as part of sophisticated cyber-espionage campaigns targeting non-governmental organizations and other high-value organizations.
Vulnerabilities
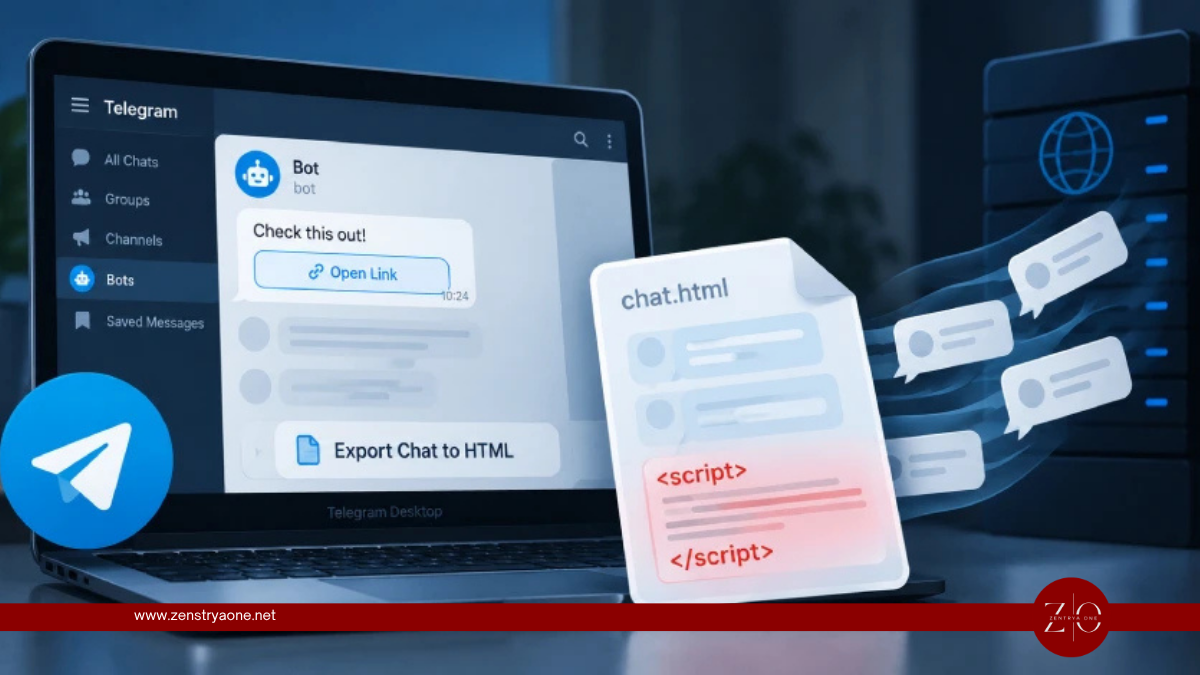
Telegram Desktop Flaw Lets Hidden JavaScript Steal Messages From HTML Chat Exports
Security researchers have disclosed a high-severity vulnerability in Telegram Desktop that could allow malicious JavaScript hidden inside a seemingly normal chat message to execute when a conversation is exported as HTML and opened in a web browser.
Vulnerabilities
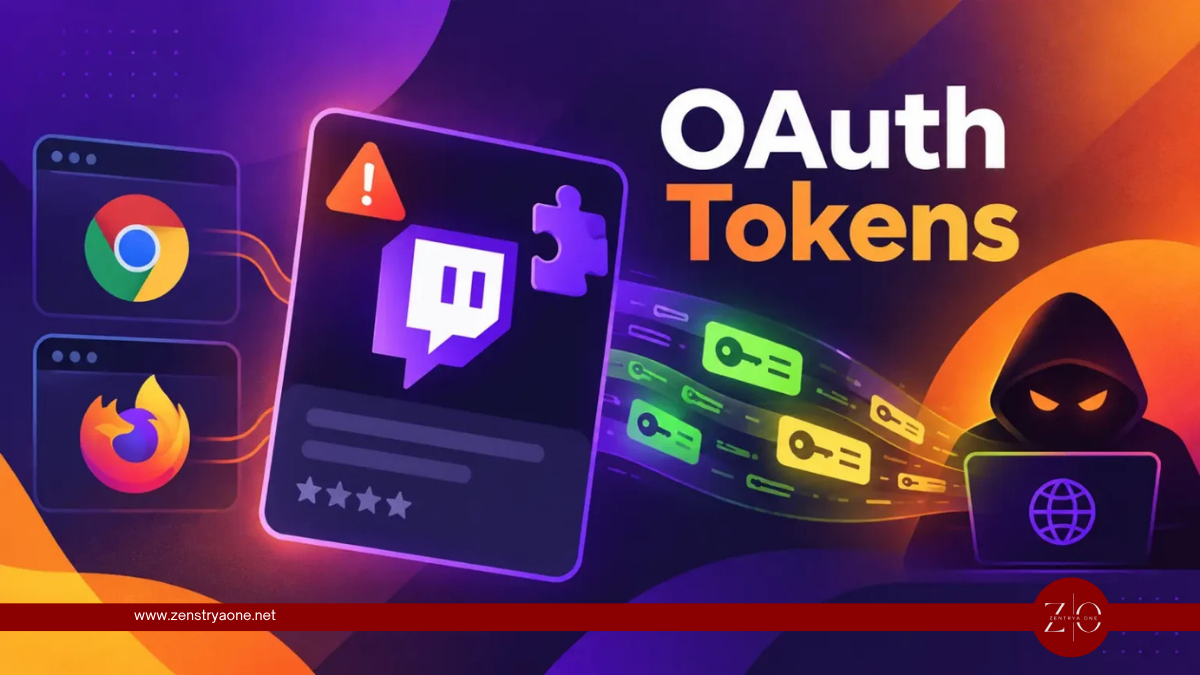
Malicious Twitch Extension Exposes OAuth Tokens of More Than 30,000 Users
A browser extension advertised as a Twitch enhancement tool has been found exposing users' OAuth session tokens to third-party proxy infrastructure, potentially allowing attackers to access affected Twitch accounts without knowing the users' passwords.
Threat Intel
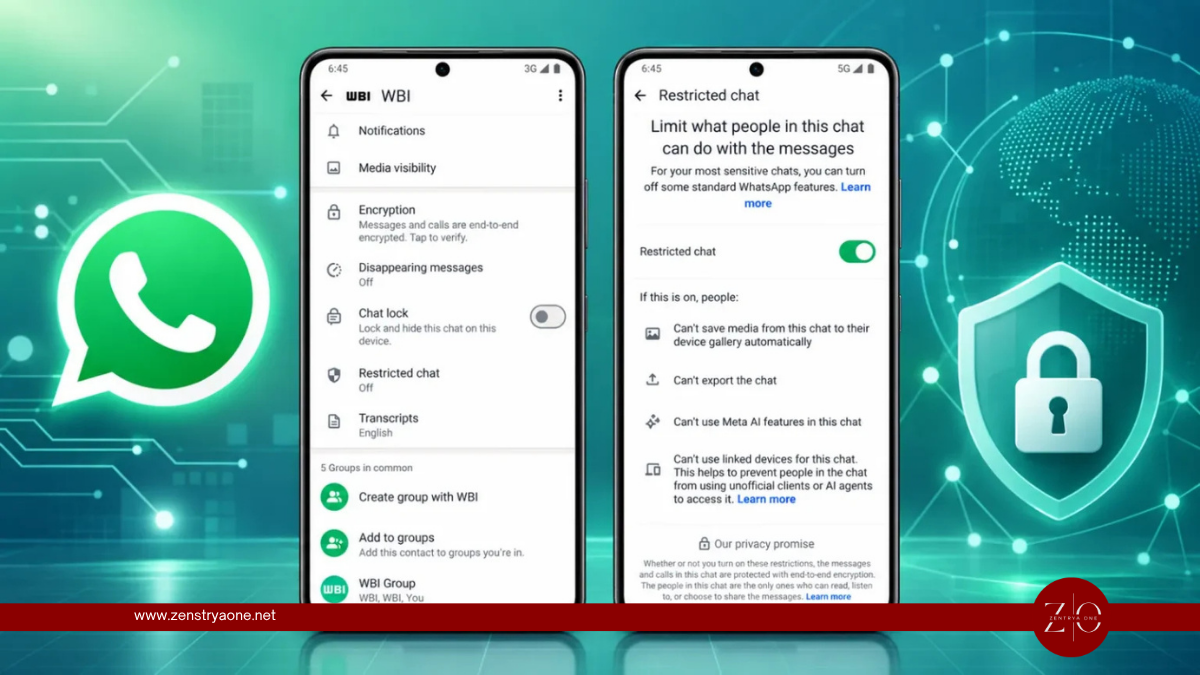
WhatsApp Tests Restricted Chat Feature to Keep Sensitive Conversations on Your Primary Phone
WhatsApp is developing a new privacy feature called Restricted Chat that could give users greater control over where sensitive conversations are accessible.
critical
Vulnerabilities
Weekly Cybersecurity Roundup: Zero-Days, Firewall Attacks, AI-Powered Threats and Major Data Breaches
The cybersecurity landscape remained highly active this week, with attackers targeting enterprise firewalls, operating systems, browsers, databases and cloud environments. Security teams also faced a record-scale Microsoft Patch Tuesday, multiple vulnerabilities under active exploitation, and growing evidence that artificial intelligence is being integrated directly into offensive cyber operations
critical
CVE-2026-68488
Vulnerabilities
Plesk Backup Manager Flaw Lets Low-Privileged Users Gain Root Access
A newly disclosed vulnerability in Plesk Backup Manager could allow a low-privileged customer to escalate privileges and obtain full root access to a vulnerable Linux server.
Data Breaches
Revolut Data Breach Exposes Passports and Full Transaction Histories After Fake Government Request
Fintech giant Revolut has confirmed a data-security incident in which an unauthorized party obtained sensitive customer information after submitting fraudulent requests that appeared to come from a legitimate government agency.
Cloud & AppSec
Attackers Use Passkey-Themed Phishing to Hijack Microsoft Cloud Accounts and Steal Data
Threat actors are using passkey-themed social engineering to compromise Microsoft 365 accounts and gain access to sensitive cloud data, according to Microsoft Threat Intelligence.