Fake Job Interviews and Compromised AI Tools Behind Binance’s $6.43 Billion Crypto Heist
Binance reveals how fake job interviews, malicious software and compromised AI tools enabled hackers to steal $6.43 billion in cryptocurrency.
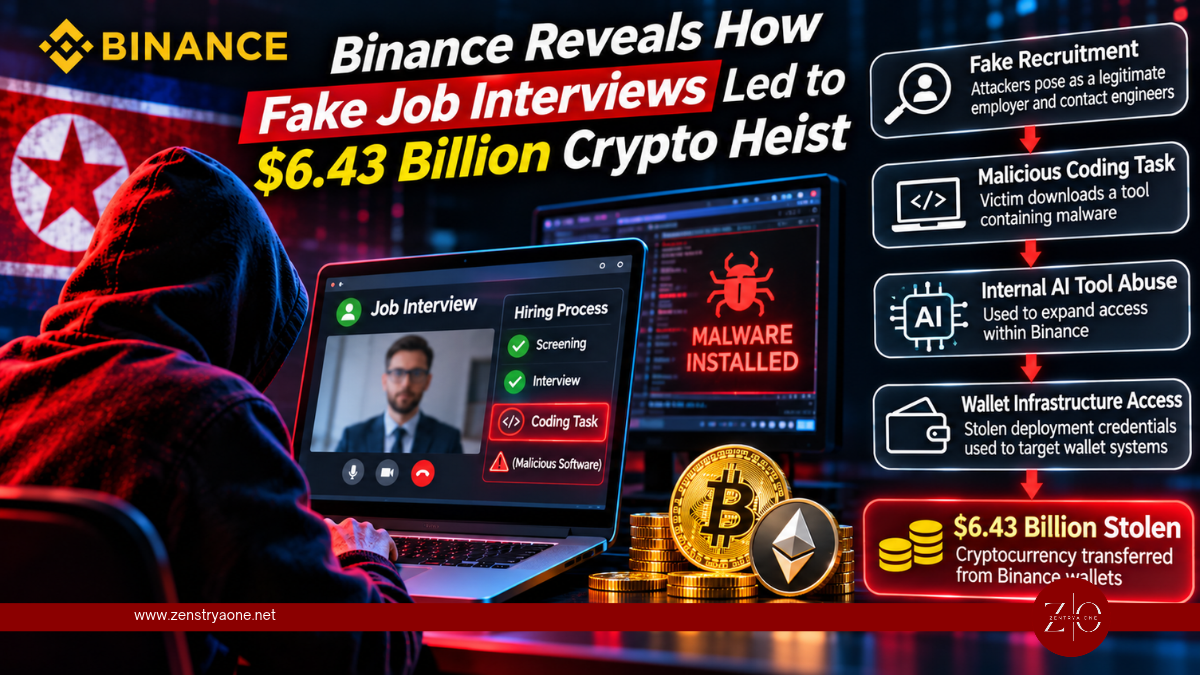
Cryptocurrency exchange Binance has revealed how a sophisticated cyberattack involving fake job interviews, malicious software and compromised internal artificial intelligence tools resulted in the theft of approximately $6.43 billion in digital assets.
According to the company's investigation, attackers spent several months targeting employees and gaining access to critical wallet infrastructure before executing the massive cryptocurrency theft on October 29, 2026.
The FBI has attributed the attack to North Korea-linked hacking group TraderTraitor, although North Korea has denied involvement.
How Hackers Infiltrated Binance
The investigation identified a multi-stage attack that began in June 2026.
An engineer working in Binance's wallet infrastructure team downloaded a malicious Homebrew installer while attempting to install an AI development tool.
Although Binance detected the suspicious activity, replaced the affected device and rotated credentials, the attackers had already obtained information about the employee's responsibilities and colleagues.
In September, the attackers launched another campaign targeting a different engineer through a legitimate recruitment platform.
Posing as representatives of a fictitious company, the attackers arranged multiple interviews involving individuals impersonating human resources personnel and senior executives.
During the recruitment process, the engineer was instructed to download a coding assignment containing malicious software.
The malware executed during setup, allowing attackers to compromise the employee's computer while attempting to evade endpoint security detection.
Internal AI Tool Used to Expand Access
On October 20, the attackers exploited the compromised computer and abused an internal AI tool to extend their access to other engineers.
They subsequently discovered deployment credentials associated with Binance's wallet infrastructure.
On October 29, the attackers used the stolen credentials to deploy a malicious container and execute code targeting the exchange's wallet systems.
This provided unauthorized access to internal wallet-signing functionality, enabling fraudulent cryptocurrency transactions outside the normal withdrawal process.
Investigators also identified abuse of Ethereum's EIP-7702 authorization mechanism, which complicated efforts to immediately stop unauthorized transfers.
Billions Stolen in Cryptocurrency
The attack resulted in approximately $6.43 billion in cryptocurrency being transferred from affected wallets.
Binance reported that approximately $2.85 billion in assets had been frozen or intercepted through coordination with blockchain intelligence firms, stablecoin issuers and law enforcement agencies.
The exchange also stated that around 98% of affected token assets had been replenished using company funds.
Binance maintains that customers will not bear the financial losses associated with the incident.
Binance Strengthens Security Following the Attack
Following the breach, Binance announced several security improvements, including:
- Rebuilding compromised wallet infrastructure in a clean environment.
- Replacing affected employee devices and revoking compromised credentials.
- Strengthening internal AI tool security and access controls.
- Expanding endpoint protection and behavioral anomaly detection.
- Improving security controls around wallet-signing services.
- Conducting additional employee-device security assessments.
The company also plans to commission independent cybersecurity experts to review its security environment.
Growing Threat From Fake Recruitment Campaigns
The incident highlights the increasing use of recruitment-themed social engineering against software developers and cryptocurrency organizations.
Attackers frequently impersonate recruiters or technology executives and distribute malicious coding assignments, software packages or video conferencing applications.
These techniques can compromise developer workstations and expose sensitive credentials, even when employees are using legitimate job-search platforms.
Organizations should isolate untrusted coding assignments, restrict privileged credentials, verify recruitment contacts and monitor unusual developer-environment activity.
Security Takeaway
The Binance breach demonstrates how social engineering, compromised developer tools and excessive access privileges can combine to create a major cybersecurity incident.
It also highlights the risks of connecting employee workstations, internal AI tools and sensitive financial infrastructure without sufficient security boundaries.
Organizations handling high-value digital assets should prioritize developer endpoint security, privileged access management, secure software supply chains and continuous monitoring to prevent similar attacks.
Related reporting
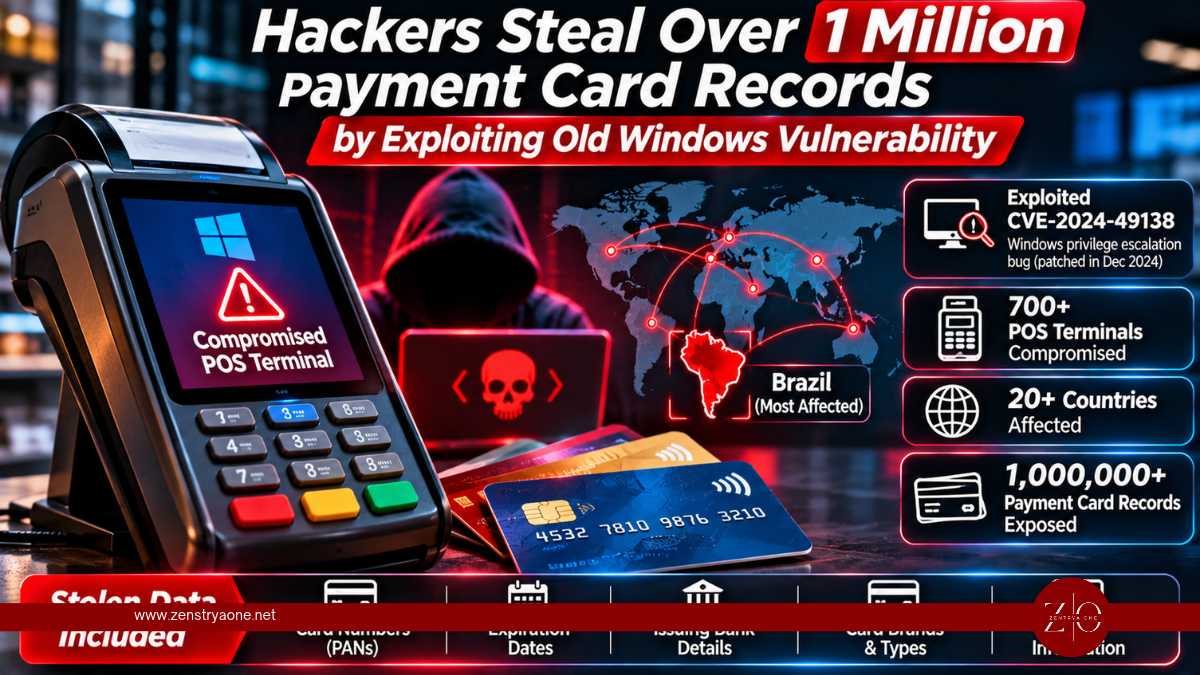
Hackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability
Hackers exploit Windows CVE-2024-49138 to compromise over 700 POS terminals across 20 countries, stealing more than one million payment card records.
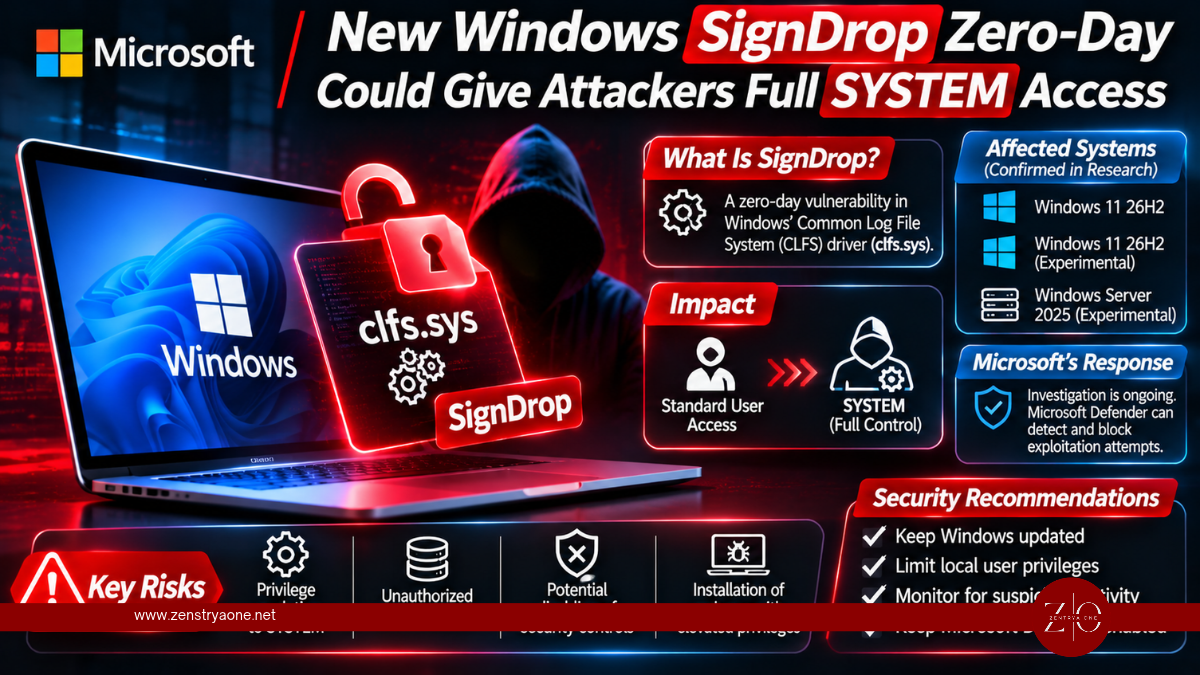
New Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access
New Windows SignDrop zero-day exploit abuses Microsoft CLFS security protections to gain SYSTEM privileges. Learn about affected systems and mitigation.
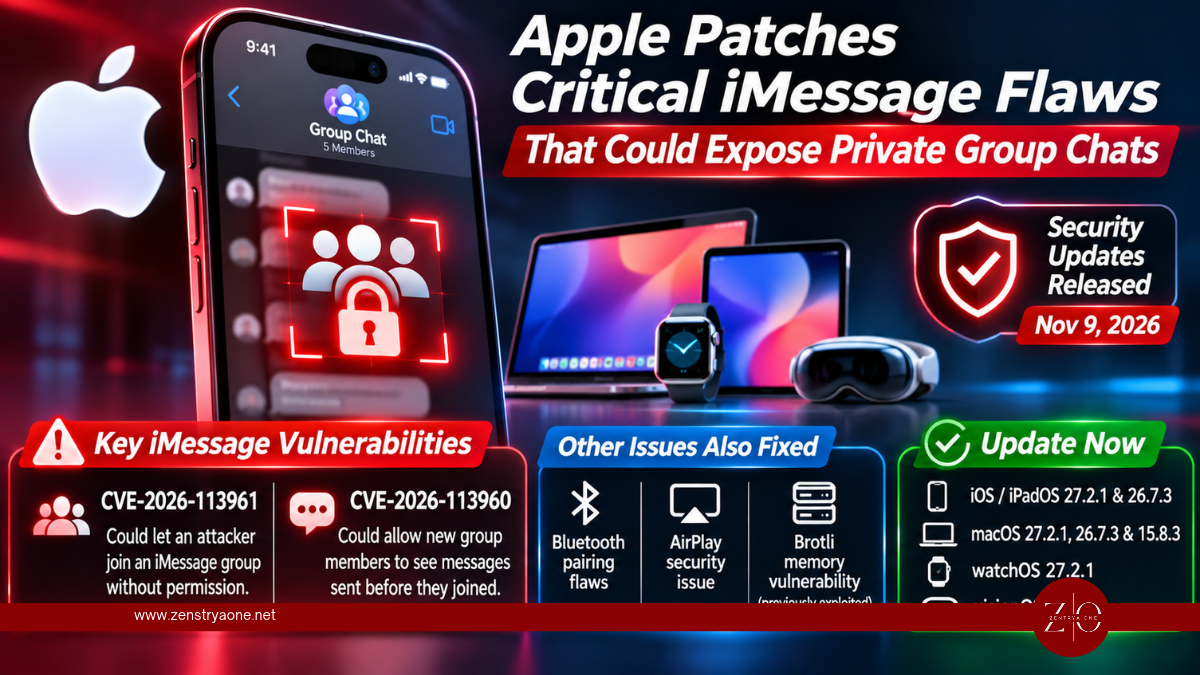
Apple Fixes Critical iMessage Privacy Flaws That Could Expose Private Group Chats
Apple patches two iMessage vulnerabilities that could expose private group chats, alongside Bluetooth, AirPlay and Brotli security flaws.