JPMorgan Chase, Visa and Mastercard Confirm Third-Party Cyberattacks Exposing Customer Information
JPMorgan Chase, Visa and Mastercard confirm third-party cyberattacks exposing customer contact information, while payment networks remain unaffected.
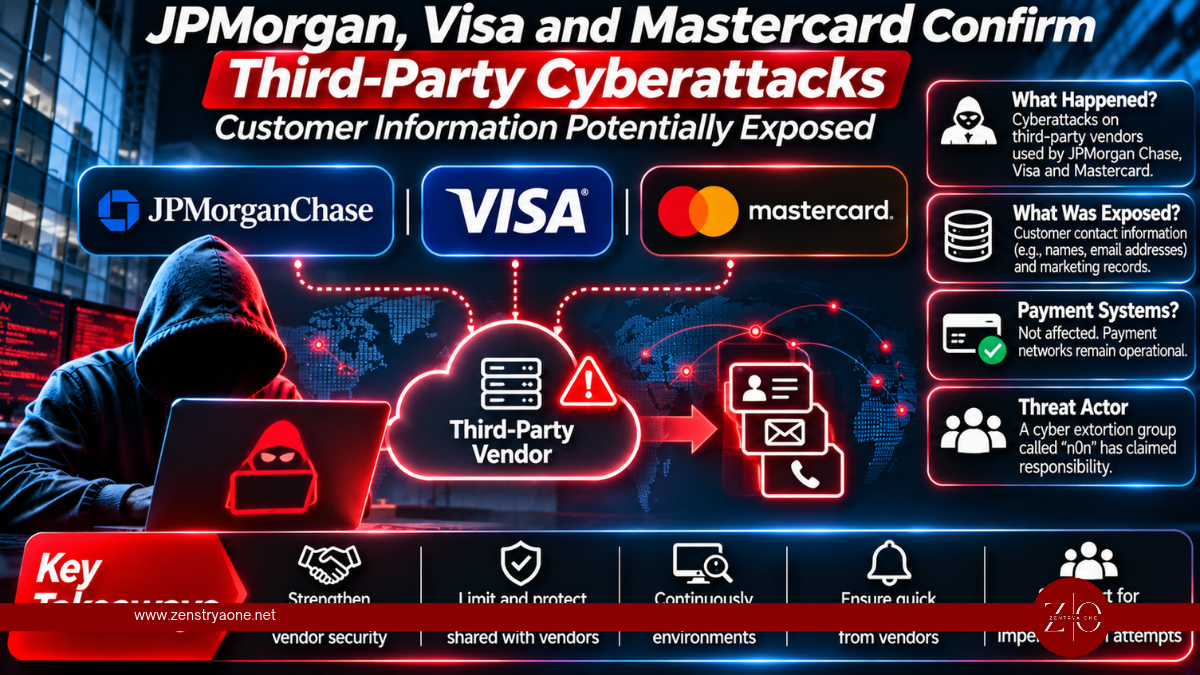
Three major financial institutions — JPMorgan Chase, Visa and Mastercard — have confirmed cybersecurity incidents involving third-party service providers, potentially exposing customer contact information and marketing records.
The incidents came to public attention after a cyber extortion group claimed to have stolen customer information associated with the financial companies.
However, all three organizations have emphasized that their core payment systems remain operational and that payment card numbers and transaction data were not affected, based on their investigations so far.
What Happened?
On November 19, JPMorgan Chase confirmed that attackers had targeted external vendors providing services to the bank.
According to the company, the attackers may have accessed marketing information, including customer names and email addresses.
Visa separately acknowledged an incident involving a third-party service provider in the Asia-Pacific region.
Mastercard also confirmed that a vendor security incident exposed a limited number of email addresses belonging to cardholders enrolled in a specific benefits program.
The companies have not publicly identified the affected vendors or established whether all three incidents originated from the same provider.
Hackers Claim to Have Stolen Thousands of Customer Records
A cyber extortion group known as n0n has claimed responsibility for the data theft and reportedly published information associated with the affected companies.
Security researchers examining the alleged leaked material identified approximately 16,000 email addresses linked to JPMorgan Chase customers.
Some records reportedly contained additional contact information, including phone numbers.
The group also claimed to possess customer engagement and marketing information associated with Visa and Mastercard.
However, the full authenticity and extent of the published datasets have not been independently confirmed.
Payment Networks Remain Secure
Despite the reported exposure of customer information, the companies stated that their payment operations were not compromised.
| Organization | Reported impact |
|---|---|
| JPMorgan Chase | Possible exposure of customer names and email addresses held by vendors |
| Visa | Third-party provider incident; no reported compromise of Visa systems or payment card data |
| Mastercard | Limited email address exposure involving a specific cardholder benefits program |
Mastercard confirmed that the incident had been contained and that customers could continue using their cards normally.
JPMorgan Chase also stated that the breach was unrelated to banking service disruptions experienced earlier in the week, which the company attributed to a software bug.
Why Third-Party Cyberattacks Are a Growing Concern
Financial institutions frequently depend on external technology providers for customer communications, marketing, loyalty programs and other business operations.
Although these vendors may not directly process payments, they can hold valuable customer information.
Attackers can exploit weaknesses in third-party environments to obtain sensitive information without compromising a financial institution's primary systems.
Even limited exposure of names and email addresses can increase the risk of targeted phishing, impersonation and financial scams.
Security Recommendations
Financial institutions should strengthen third-party security through the following measures:
- Conduct regular vendor risk assessments to evaluate external providers' cybersecurity controls.
- Limit customer data sharing to information necessary for specific business purposes.
- Implement strong access controls and multifactor authentication for vendor accounts.
- Monitor third-party environments for suspicious activity and unauthorized data access.
- Establish incident notification requirements to ensure vendors report security incidents promptly.
- Review data retention policies to prevent unnecessary storage of customer information.
Customers should remain cautious about unexpected emails or messages claiming to represent their bank or payment card provider. They should verify suspicious communications through official channels and avoid opening unfamiliar links.
Security Takeaway
The incidents involving JPMorgan Chase, Visa and Mastercard highlight the cybersecurity risks associated with external service providers.
Although the companies' payment networks remain unaffected, the exposure of customer contact information demonstrates how third-party weaknesses can create security and privacy concerns.
Financial organizations must strengthen vendor security governance, restrict unnecessary data access and continuously monitor third-party risks to protect customer information.
Related reporting
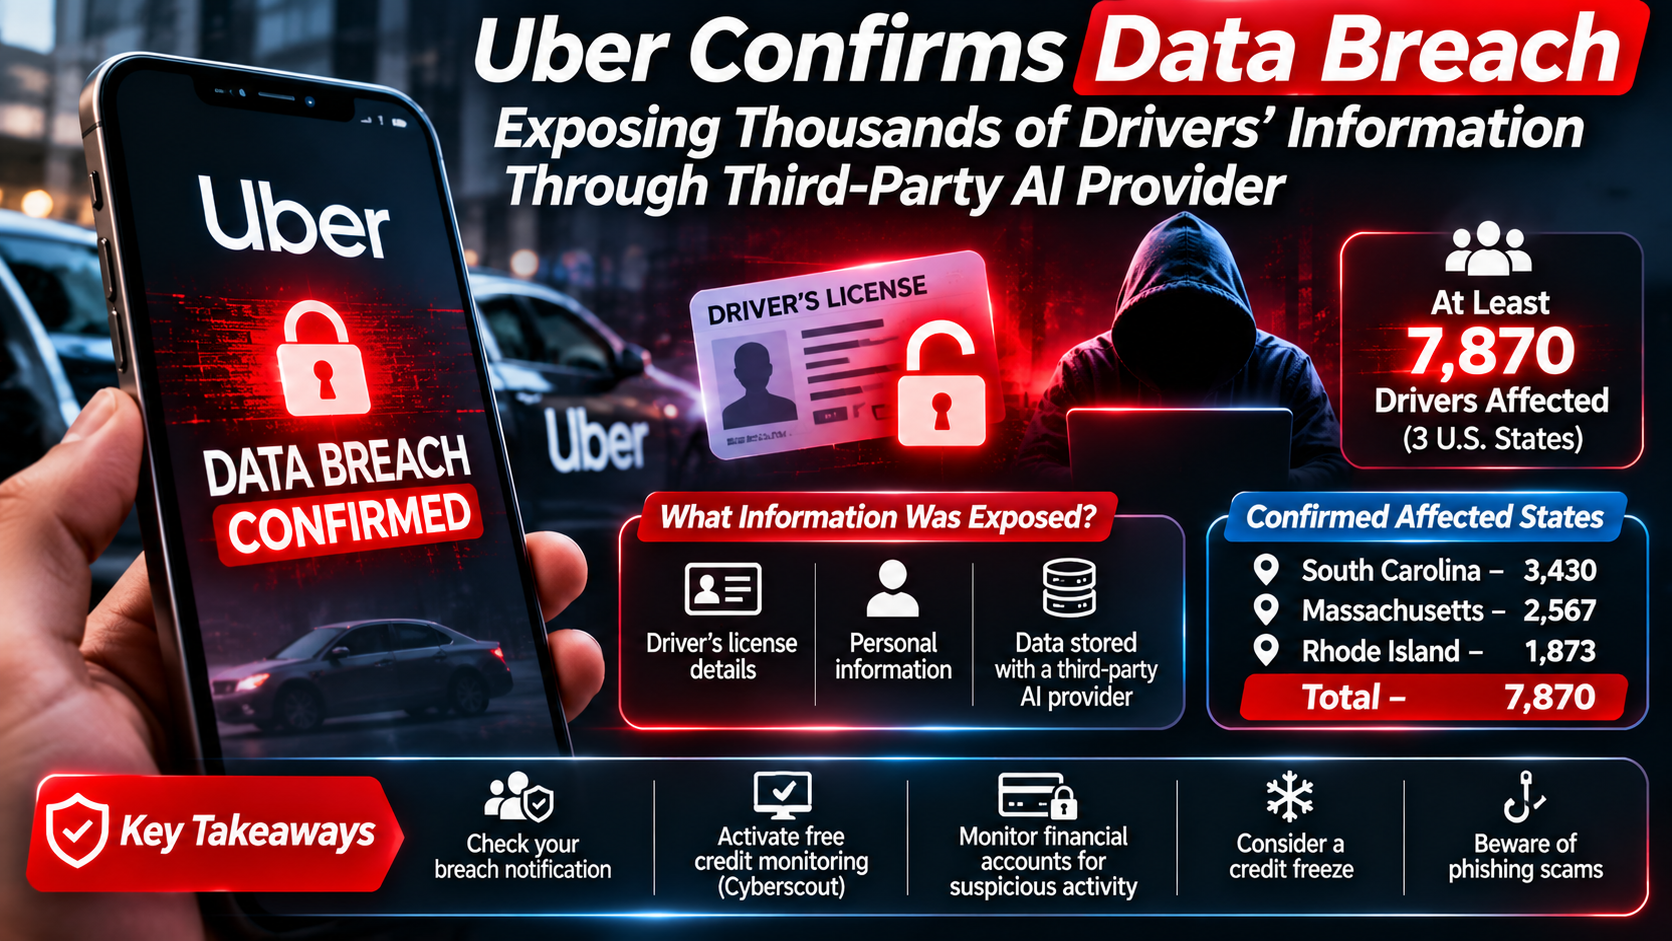
Uber Confirms Data Breach: Hackers Steal Thousands of U.S. Drivers' Personal Records
Uber confirms a data breach involving Fireworks AI, exposing personal information and driver's license details of thousands of U.S. drivers.
Binance Hit by Record $6.3 Billion Cryptocurrency Hack as North Korean Group Faces Attribution
Binance suffers a record $6.3 billion cryptocurrency hack linked to North Korea's TraderTraitor group. Nearly $3 billion frozen as Binance covers customer losses.
State Bank of India Confirms Data Leak as 3,897 Customer Records Appear on Dark Web
State Bank of India confirms a data leak involving 3,897 customer records found on the dark web. SBI investigates the source and extent of the exposure.