Russian APT29 Hackers Hijack Web Analytics Service to Target iPhone and Android Users
Russian APT29-linked hackers hijack web analytics scripts to exploit iOS and Android vulnerabilities, stealing browser cookies, passwords and sensitive data.
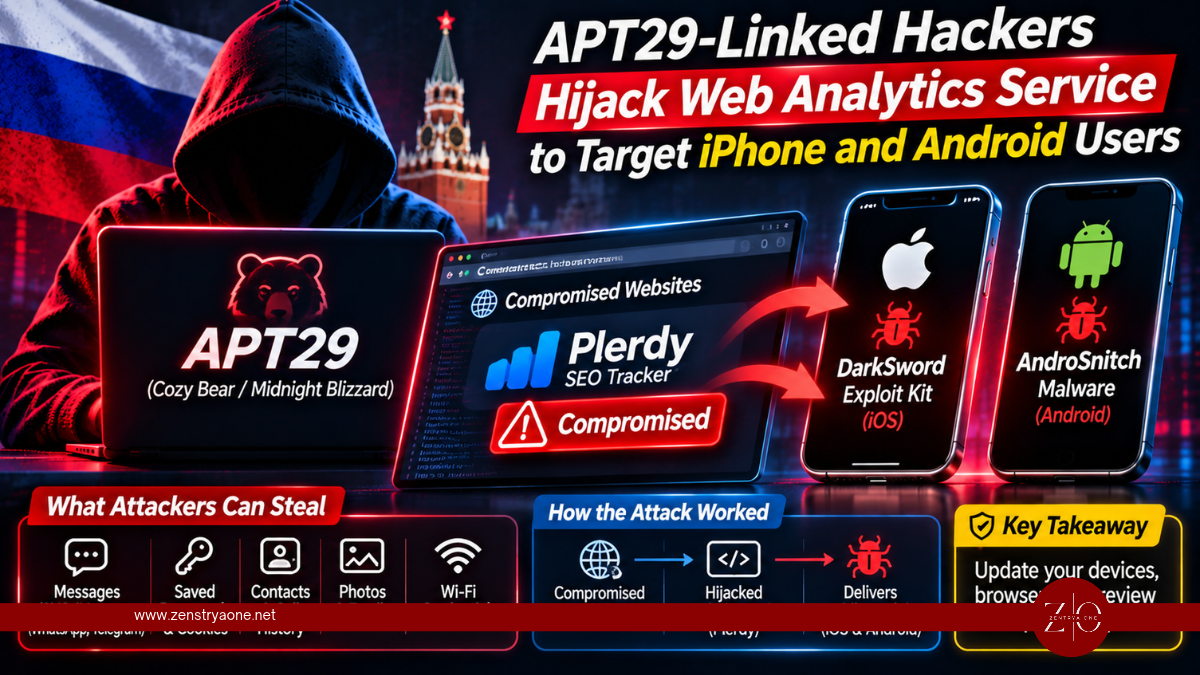
Cybersecurity researchers have uncovered a sophisticated cyber espionage campaign linked to the Russian threat group APT29, in which attackers compromised legitimate websites and a popular web analytics service to deliver malicious exploits targeting iOS and Android devices.
The campaign, identified as Poisoned Source, was discovered by French cybersecurity company Sekoia in October 2026.
Researchers warned that attackers could exploit previously patched vulnerabilities in outdated mobile devices to steal sensitive information, including browser cookies, messages, saved credentials and Wi-Fi passwords.
Hackers Compromise Legitimate Websites
According to Sekoia, the attackers used three methods to distribute malicious JavaScript:
- Compromised websites: Injecting malicious scripts into legitimate websites visited by potential targets.
- Fake websites: Creating lookalike domains impersonating trusted organizations.
- Supply chain compromise: Hijacking the Ukrainian web analytics service Plerdy SEO Tracker to distribute malicious code through websites using its tracking script.
The Plerdy compromise reportedly occurred between August 27 and September 3, 2026, potentially exposing visitors across hundreds of websites.
Once a visitor accessed an affected website, the injected JavaScript collected information about the browser and operating system before delivering an exploit designed for the device.
iPhones Targeted Through DarkSword Exploit Kit
For Apple devices, attackers used exploit chains targeting vulnerabilities in older iOS versions.
One attack targeted devices running iOS 16.7 to steal browser cookies.
A more advanced attack targeted iOS 18.5 using the DarkSword exploit kit, enabling the collection of extensive device information.
Potentially exposed data included:
- SMS and iMessage conversations
- WhatsApp and Telegram databases
- Saved passwords and iCloud Keychain information
- Contacts, call history and browser cookies
- Photos, emails and Wi-Fi credentials
Researchers emphasized that these attacks exploited known vulnerabilities for which security patches were already available.
Android Devices Targeted With AndroSnitch Malware
Android users were targeted through vulnerabilities affecting older Chrome browser versions.
The attackers deployed malware identified as AndroSnitch, designed to extract browser information and stored Wi-Fi passwords.
The Android attack chain exploited two vulnerabilities:
- CVE-2026-3910
- CVE-2025-27038
Researchers observed targeting of Chrome versions 139 through 145, excluding version 143.
The malware focused on information theft rather than maintaining long-term persistence on compromised devices.
Campaign Linked to Russian Intelligence Operations
APT29, also known as Cozy Bear and Midnight Blizzard, is widely associated with Russia's Foreign Intelligence Service (SVR).
Sekoia assessed the campaign's connection to APT29 with moderate-to-high confidence.
The affected websites included organizations associated with the military, government-related activities and strategically important industries.
Researchers identified compromised websites connected to Ukrainian military interests, a U.S. chemical industry association and European political organizations.
However, investigators have not confirmed the total number of successfully compromised devices or whether the campaign targeted specific individuals exclusively.
How Users and Organizations Can Stay Protected
Security experts recommend the following measures:
- Update mobile operating systems: Install the latest available iOS and Android security updates.
- Update web browsers: Keep Chrome, Safari and other browsers fully patched.
- Monitor third-party scripts: Website administrators should review externally hosted analytics and tracking scripts.
- Strengthen mobile security: Organizations should use mobile device management and endpoint threat detection.
- Monitor suspicious traffic: Investigate unexpected connections to unfamiliar domains and infrastructure.
- Protect sensitive accounts: Use strong authentication and review account sessions if device compromise is suspected.
Security Takeaway
The Poisoned Source campaign demonstrates how attackers can transform legitimate websites and trusted third-party services into delivery channels for advanced mobile exploits.
The attacks are particularly concerning because vulnerable devices can be compromised simply by visiting an affected website, without downloading suspicious applications.
Keeping mobile devices updated, monitoring third-party website dependencies and strengthening browser security remain essential defenses against sophisticated cyber espionage campaigns.
Related reporting
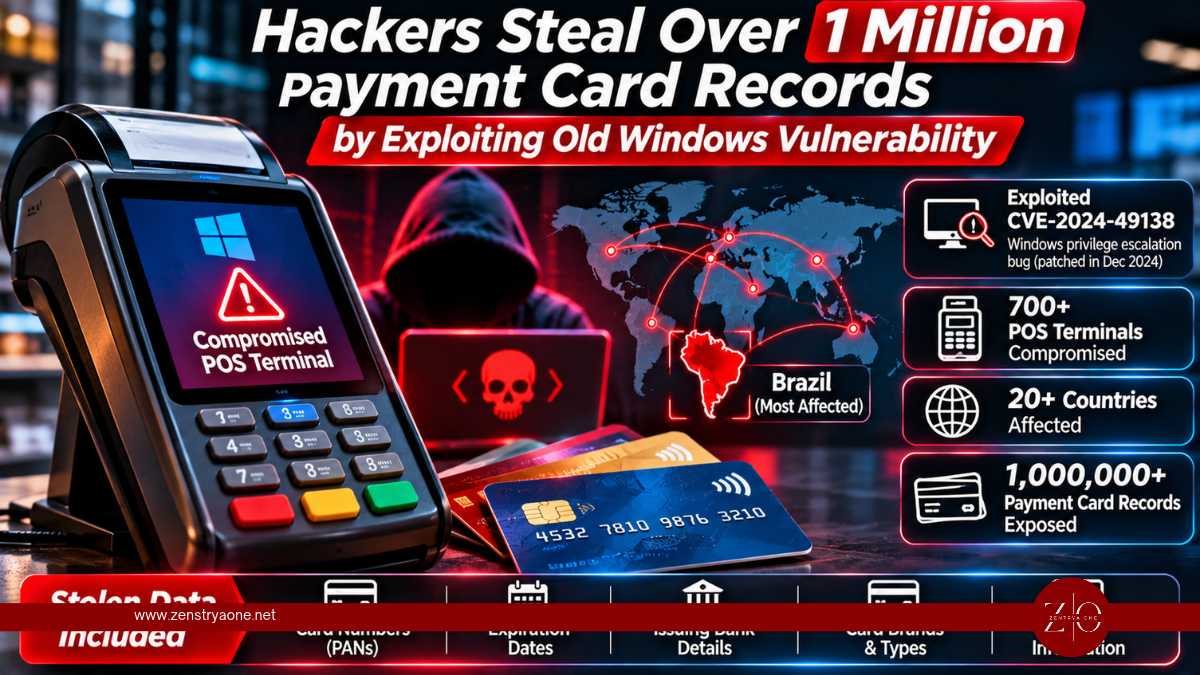
Hackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability
Hackers exploit Windows CVE-2024-49138 to compromise over 700 POS terminals across 20 countries, stealing more than one million payment card records.
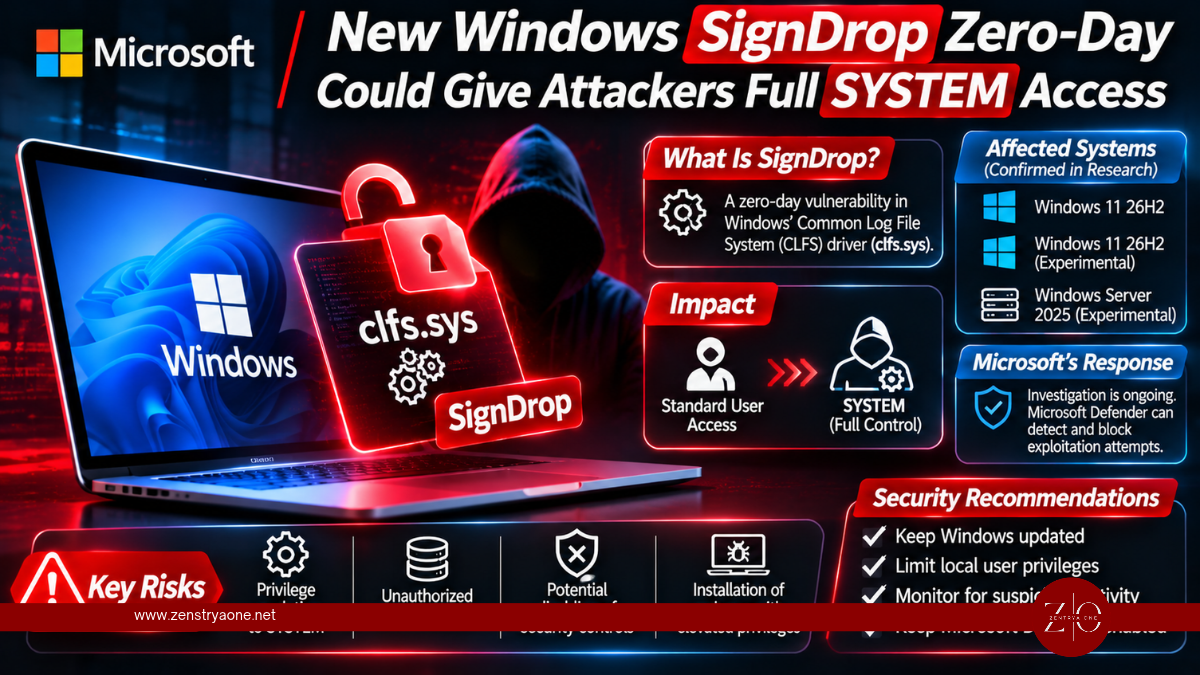
New Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access
New Windows SignDrop zero-day exploit abuses Microsoft CLFS security protections to gain SYSTEM privileges. Learn about affected systems and mitigation.
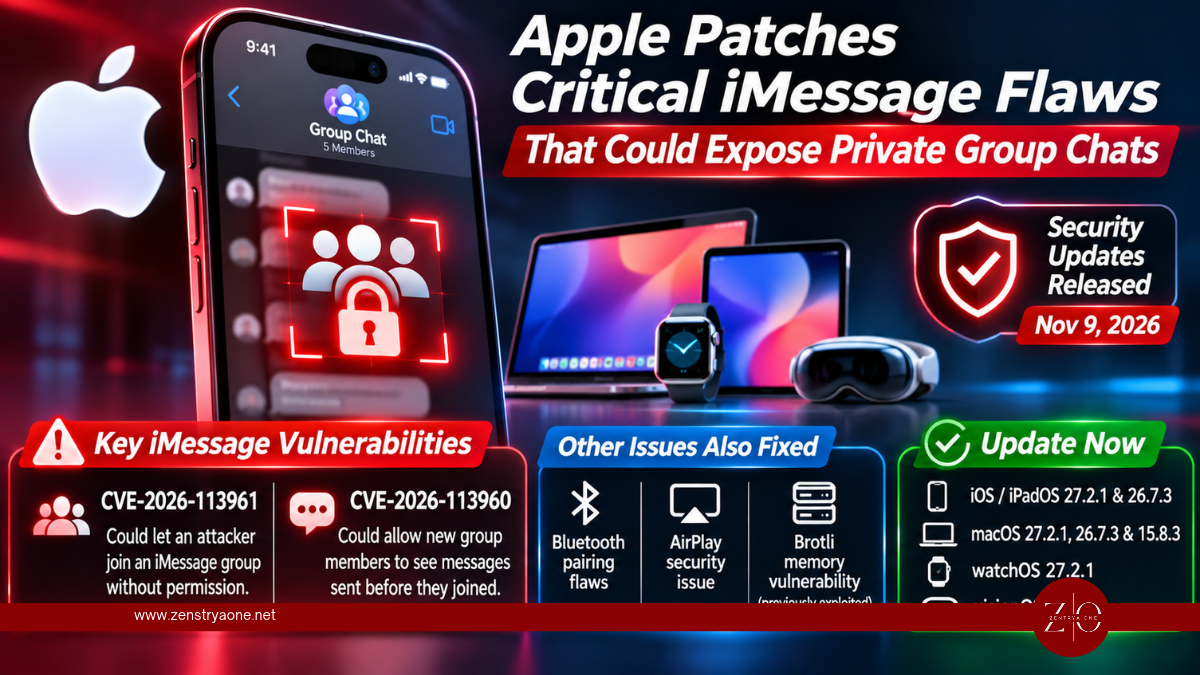
Apple Fixes Critical iMessage Privacy Flaws That Could Expose Private Group Chats
Apple patches two iMessage vulnerabilities that could expose private group chats, alongside Bluetooth, AirPlay and Brotli security flaws.