The Wire
CyberNews by Zentrya One
Section

Vulnerabilities

Disclosed flaws, patches and exploitation status.

critical CVE-2026-81642 Vulnerabilities

Critical Unbound DNSSEC Flaw Could Enable Remote Code Execution

NLnet Labs patches critical Unbound vulnerability CVE-2026-81642, a CVSS 9.1 DNSSEC validator heap overflow that could cause denial of service or potentially enable remote code execution.
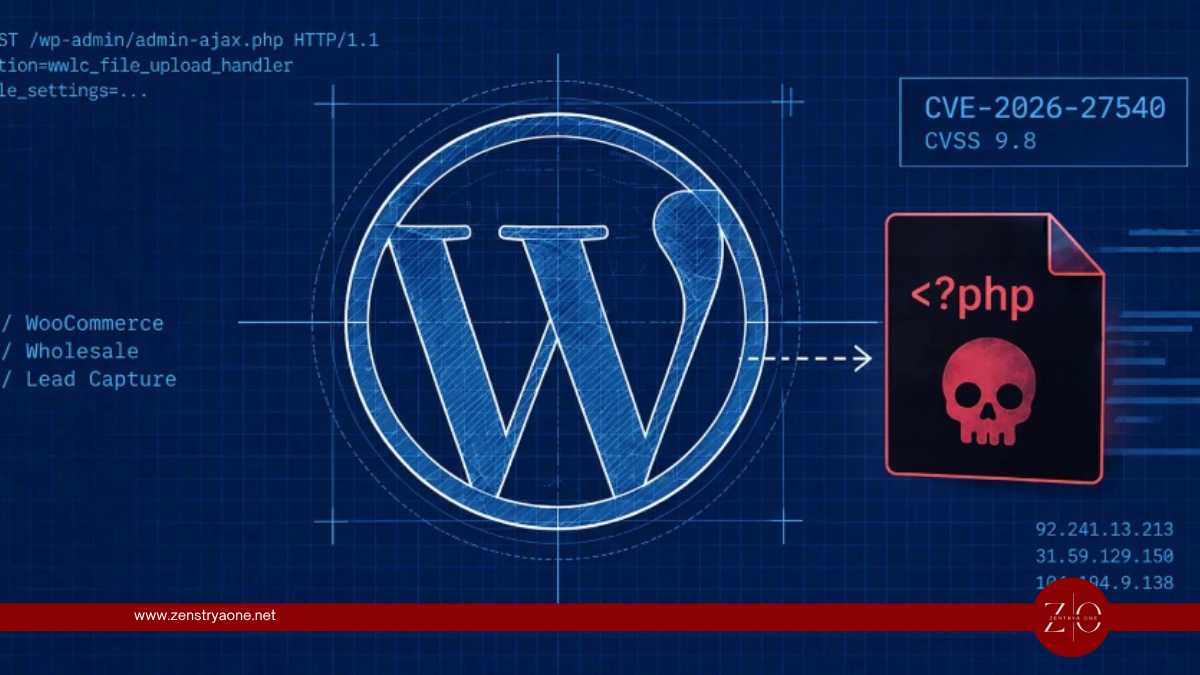
critical CVE-2026-27540 Vulnerabilities

Hackers Exploit Critical WooCommerce Plugin Flaw to Plant PHP Web Shells

Threat actors are actively exploiting a critical vulnerability in the Wholesale Lead Capture Plugin for WooCommerce, allowing unauthenticated attackers to upload malicious PHP files and potentially take complete control of vulnerable WordPress websites.

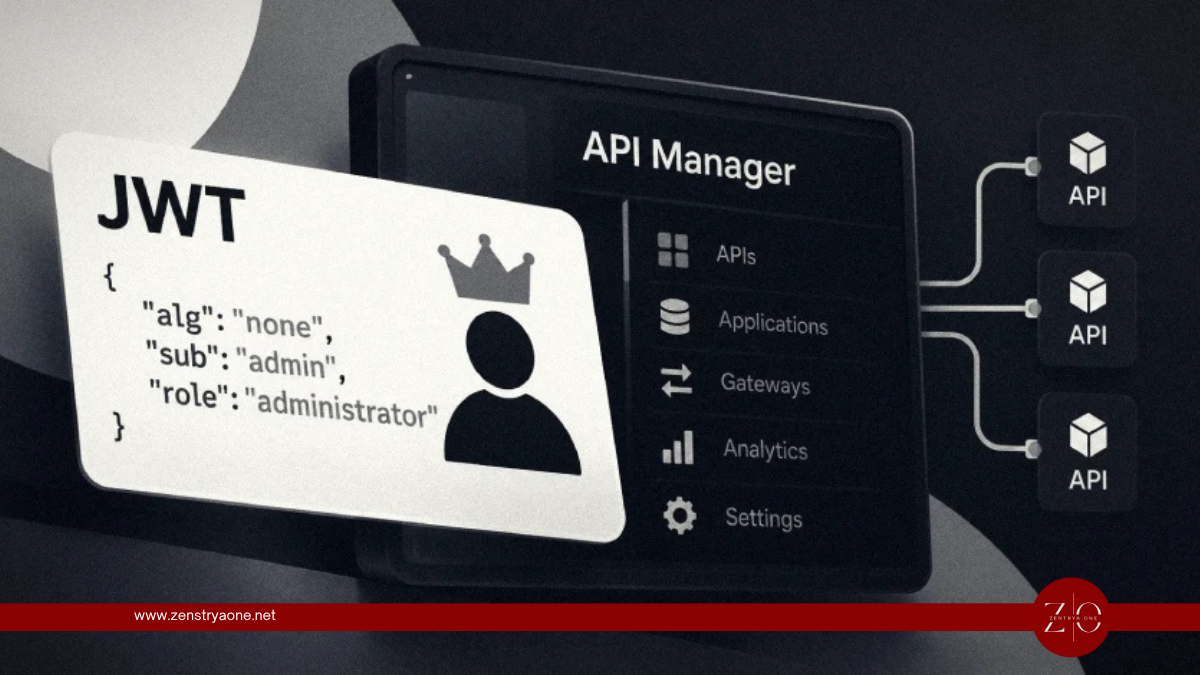
critical CVE-2026-5430 Vulnerabilities

Hackers Exploit Critical WSO2 API Manager JWT Flaw Using Forged Admin Tokens

Security researchers have detected active exploitation attempts targeting a critical authentication-bypass vulnerability in WSO2 API Manager, with attackers sending forged JSON Web Tokens (JWTs) containing administrator privileges.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.