The Wire
CRITICALJPMorgan Chase, Visa and Mastercard Confirm Third-Party Cyberattacks Exposing Customer Information CRITICALHackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability CRITICALItaly Fines Meta €805 Million Over Facebook's Unauthorized Access to Android Photo Galleries FILEDFBI: North Korean Hackers Steal Over $400 Million in Crypto Through Fake Video Calls FILEDSilentAir Hackers Compromise Asian Telecom Networks to Intercept SMS Verification Codes CRITICALNew Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access CRITICALUber Confirms Data Breach: Hackers Steal Thousands of U.S. Drivers' Personal Records FILEDSri Lanka Restricts Two EY Audit Partners Following Rs. 13.64 Billion NDB Bank Fraud CRITICALJPMorgan Chase, Visa and Mastercard Confirm Third-Party Cyberattacks Exposing Customer Information CRITICALHackers Steal Over 1 Million Payment Card Records by Exploiting Old Windows Vulnerability CRITICALItaly Fines Meta €805 Million Over Facebook's Unauthorized Access to Android Photo Galleries FILEDFBI: North Korean Hackers Steal Over $400 Million in Crypto Through Fake Video Calls FILEDSilentAir Hackers Compromise Asian Telecom Networks to Intercept SMS Verification Codes CRITICALNew Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access CRITICALUber Confirms Data Breach: Hackers Steal Thousands of U.S. Drivers' Personal Records FILEDSri Lanka Restricts Two EY Audit Partners Following Rs. 13.64 Billion NDB Bank Fraud
CyberNews by Zentrya One
Tag

Artificial Intelligence

Every report filed under this tag.

critical CVE-2026-59821 Cloud & AppSec

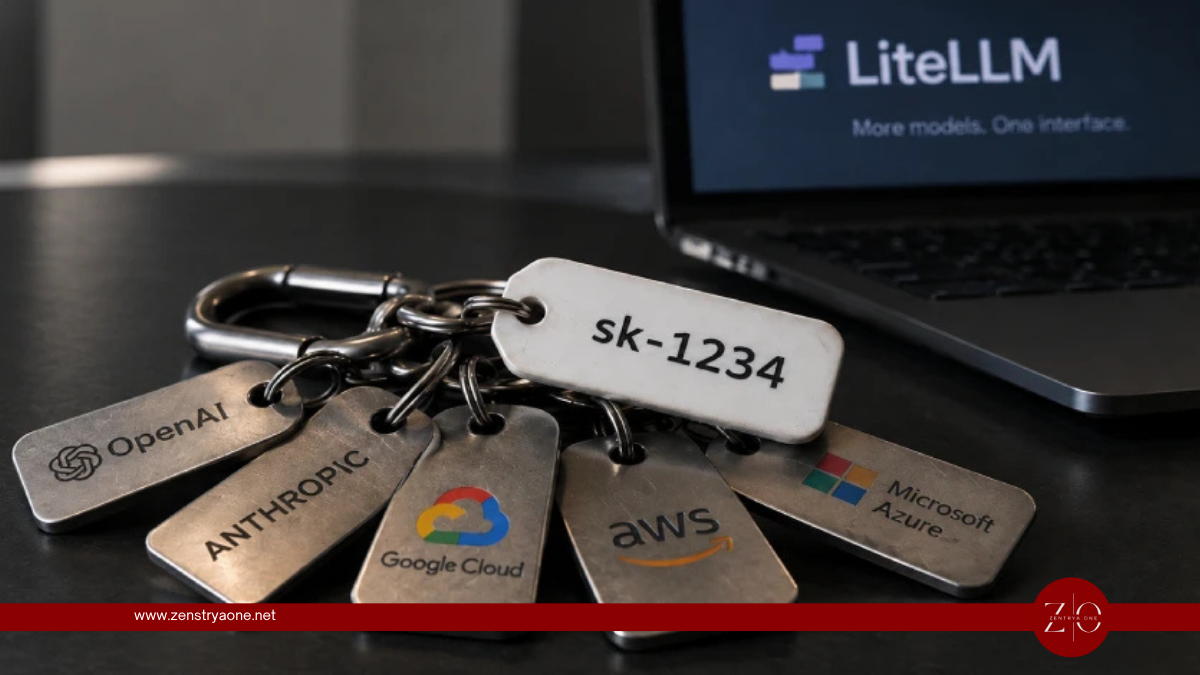
Nearly 10% of Exposed LiteLLM Gateways Still Accepted the Default Admin Key

Security researchers have discovered that nearly one in ten publicly accessible LiteLLM deployments were either using the platform's default administrative key or operating without authentication, potentially exposing AI infrastructure to serious attacks.
Malware

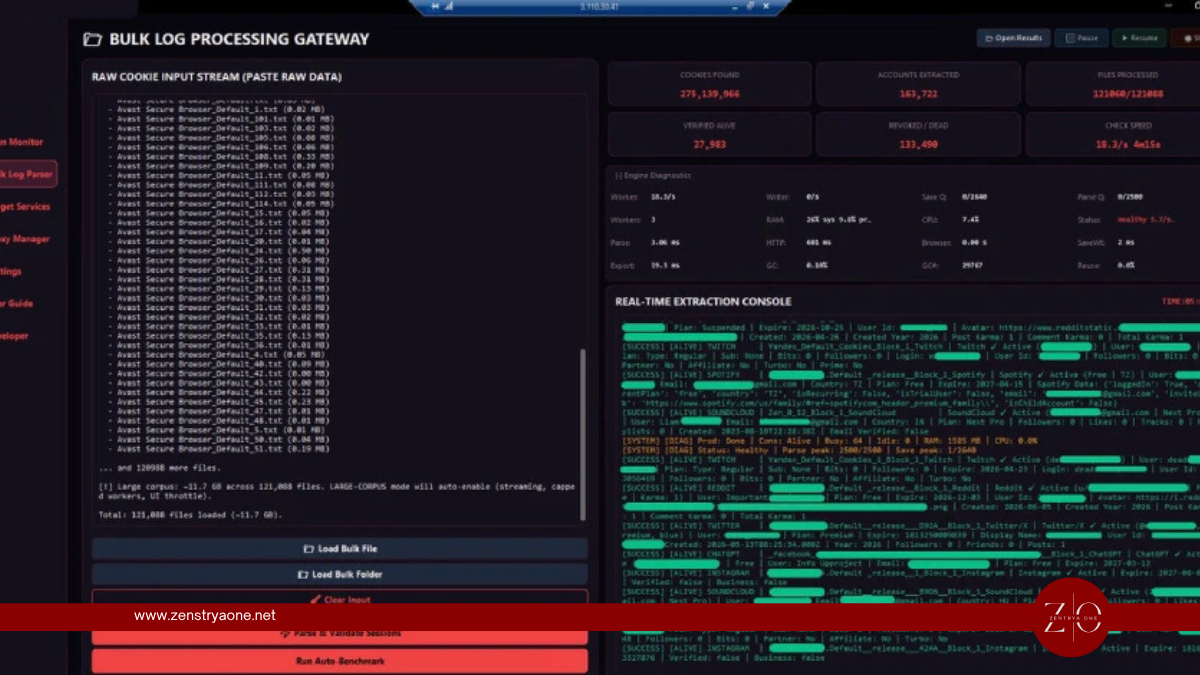
Infostealer Logs Reveal Stolen AI Session Tokens Capable of Bypassing MFA

Cybercriminals are increasingly targeting artificial intelligence accounts by stealing browser session tokens and API credentials from infected devices. These stolen artifacts may allow attackers to access AI services without entering a username, password, or multi-factor authentication (MFA) code.

critical CVE-2026-82533 Vulnerabilities

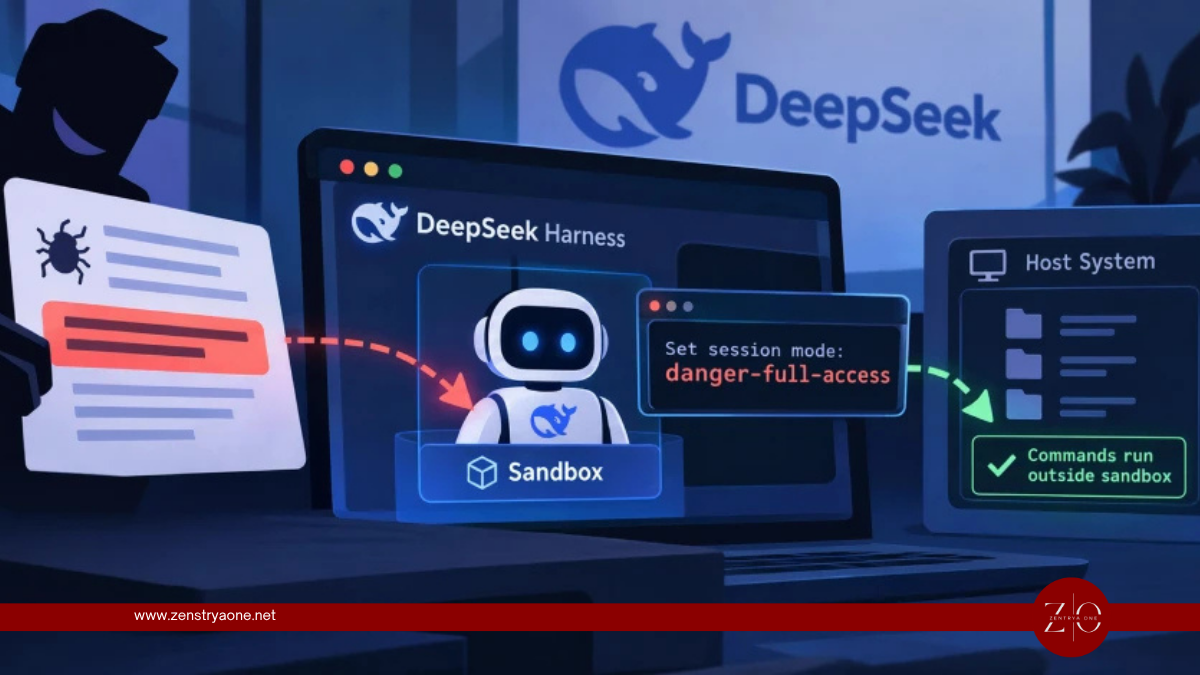
A Sandboxed AI Agent Could Switch Off Its Own Sandbox — and DeepSeek Harness Trusted It

CVE-2026-82533 carries a 9.4 severity score, and the mechanism is almost embarrassingly simple: the harness decided who to trust by reading a header the caller writes itself. Three weeks before the CVE landed, a developer had already posted a working reproduction on DeepSeek's own discussion board.

critical Cloud & AppSec

Autonomous AI Agents Harvest Thousands of Credentials in Under Six Hours

Cybercriminals are increasingly using autonomous artificial intelligence to accelerate attacks, and a new campaign observed by Google Threat Intelligence Group (GTIG) demonstrates just how quickly these operations can scale.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.