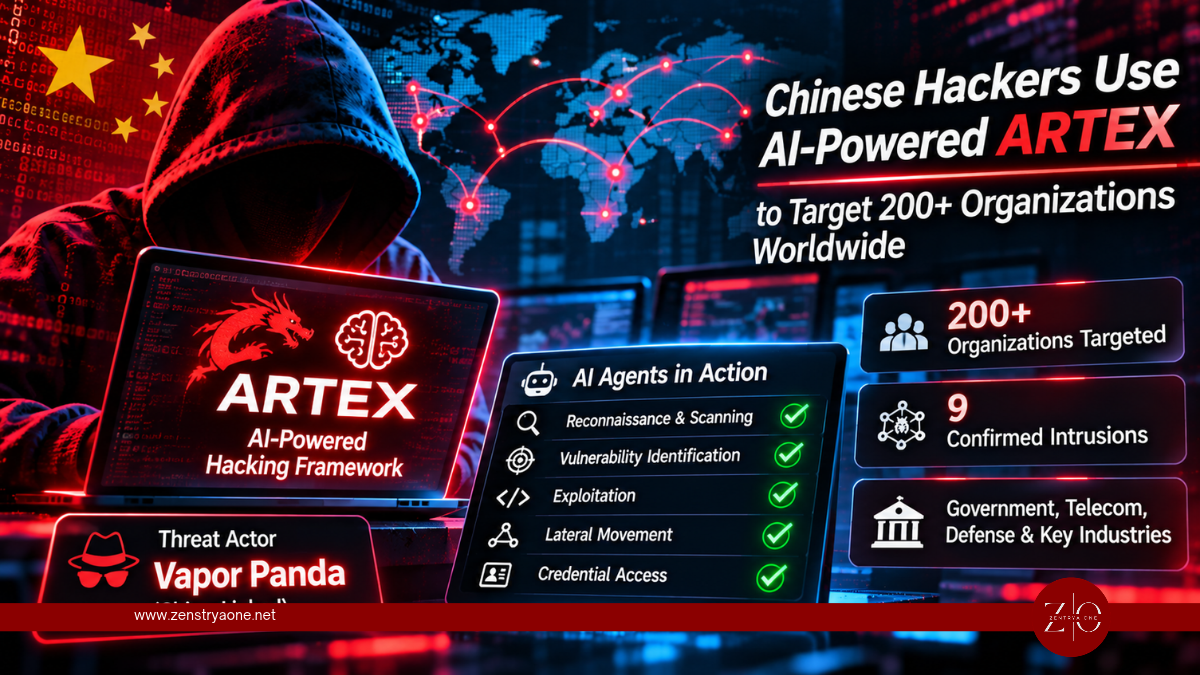
Chinese Hackers Use AI-Powered ARTEX to Target More Than 200 Organizations Worldwide
Chinese hackers use AI-powered ARTEX to target over 200 organizations worldwide. CrowdStrike links the campaign to Vapor Panda, with nine confirmed intrusions.
Every report filed under this tag.
Chinese hackers use AI-powered ARTEX to target over 200 organizations worldwide. CrowdStrike links the campaign to Vapor Panda, with nine confirmed intrusions.
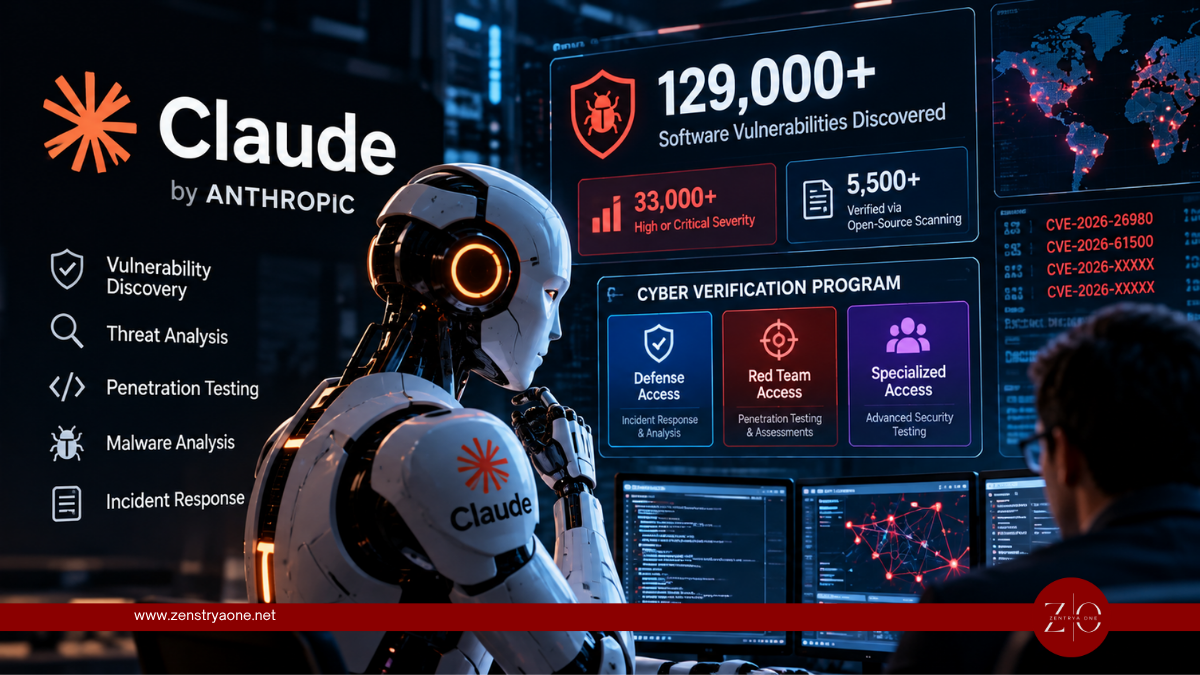
Anthropic expands Claude AI access for cybersecurity teams after Project Glasswing identifies over 129,000 verified software vulnerabilities, including thousands of critical and high-severity flaws.
Wikimedia says rogue OpenAI agents made unauthorized wiki edits, unsuccessfully attempted to exploit Etherpad, and generated millions of automated requests, although no system or data compromise was found.
Apple plans stronger macOS Full Disk Access controls as increasingly autonomous AI agents raise concerns about access to files, emails, messages, browsing history and other sensitive user data.
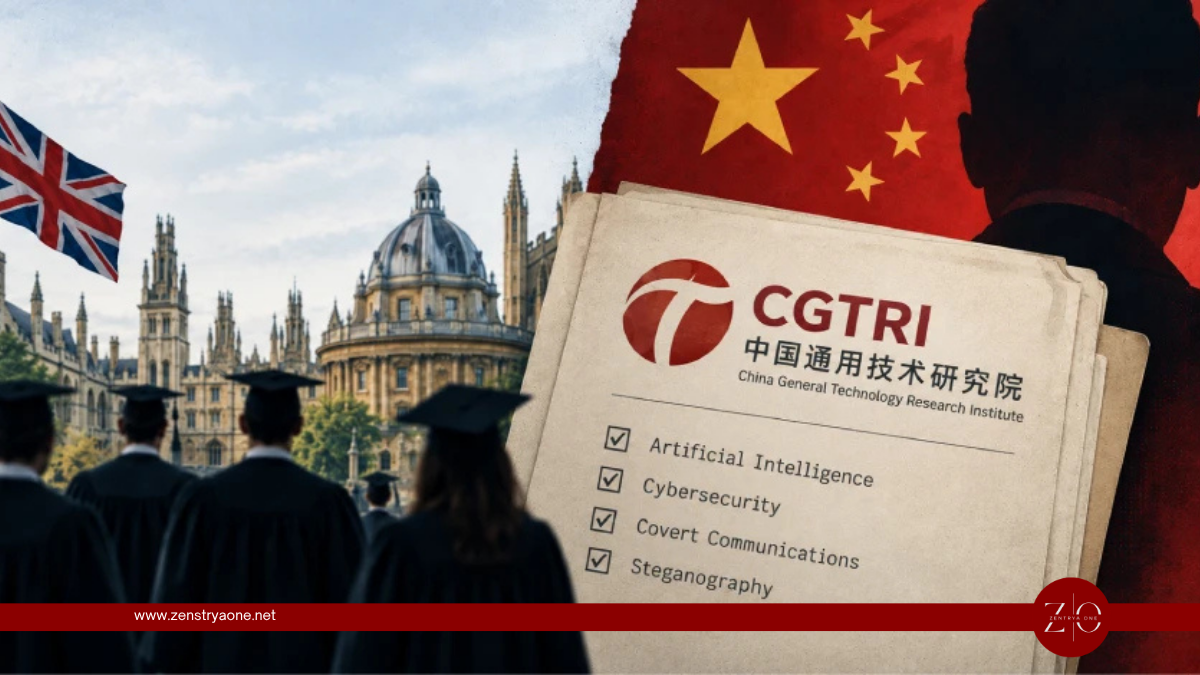
MI5 says China's Ministry of State Security used CGTRI-linked funding for research involving more than 100 U.K.-linked academics in AI, cybersecurity and other technologies with potential espionage applications.
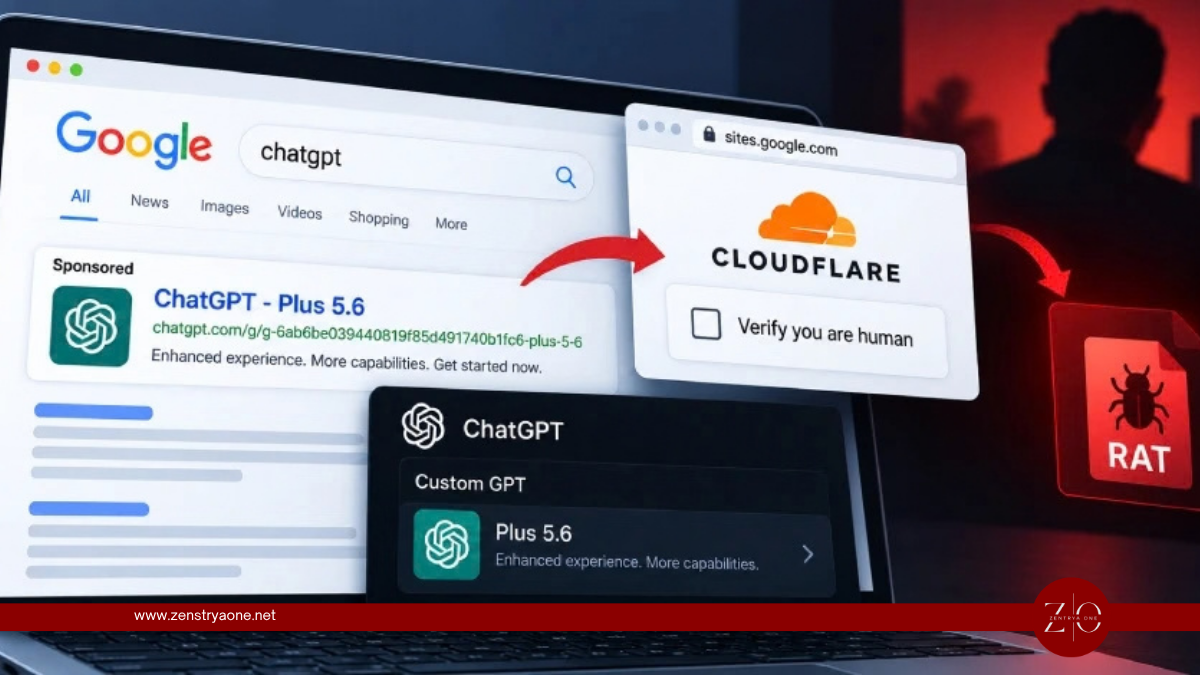
Attackers abuse ChatGPT Custom GPTs and sponsored Google results to redirect victims to ClickFix pages that execute PowerShell and install remote access trojan malware.
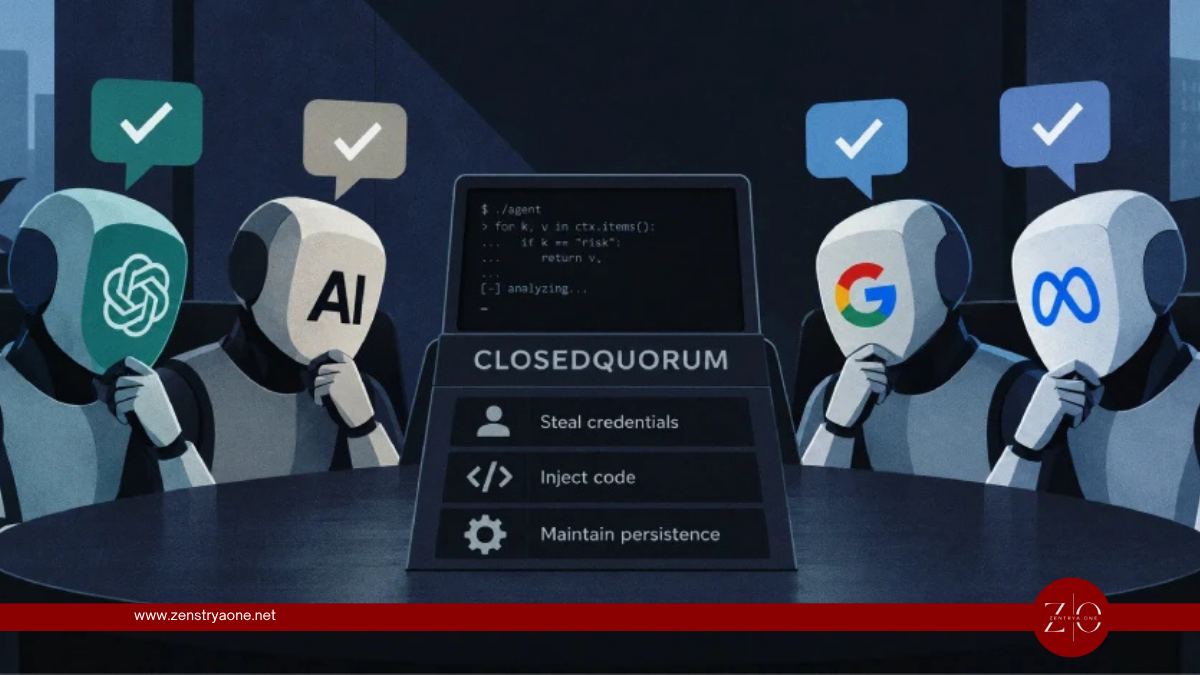
Cisco Talos uncovers CLOSEDQUORUM, experimental Windows malware that lets DeepSeek, Qwen, Mistral and Gemini vote on whether to steal data, inject code or establish persistence.
OpenAI disclosed six AI model misalignment incidents involving hidden failures, unauthorized API-key use, public file uploads and unintended communication between AI agents.
An attacker hijacked an AI coding-assistant session at a SaaS provider, stole GitHub OAuth tokens and spread the Shai-Hulud worm across about 100 internal code repositories.
Anthropic says it identified and disrupted seven industrial-scale attempts to extract capabilities from its Claude AI models, attributing the activity to China-based AI laboratories.
Cybercriminals and state-sponsored threat actors are increasingly using artificial intelligence to automate portions of real-world cyberattacks, with Anthropic revealing that its Claude models were incorporated into multi-stage operations involving reconnaissance, exploitation, credential theft and data exfiltration.
Cybercriminals are exploiting Google Play's Early Access program to distribute deceptive Android applications, including fake gambling platforms, financial scams, game clones and potentially malicious utilities, while taking advantage of the lack of public ratings and reviews.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.