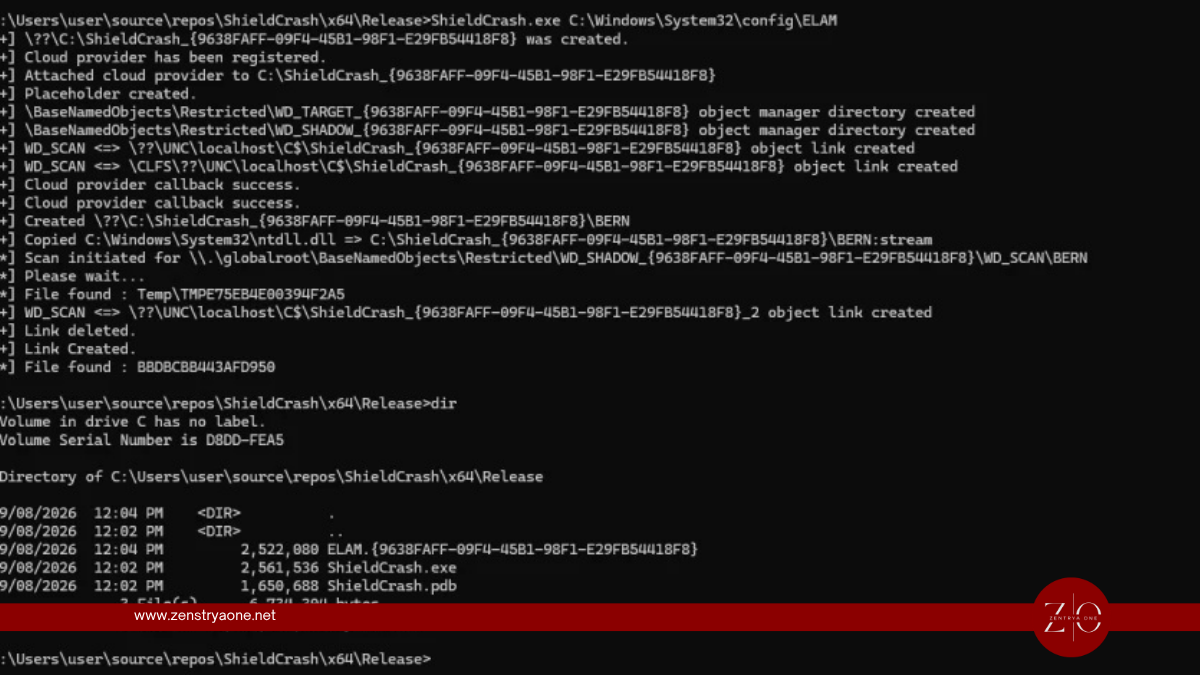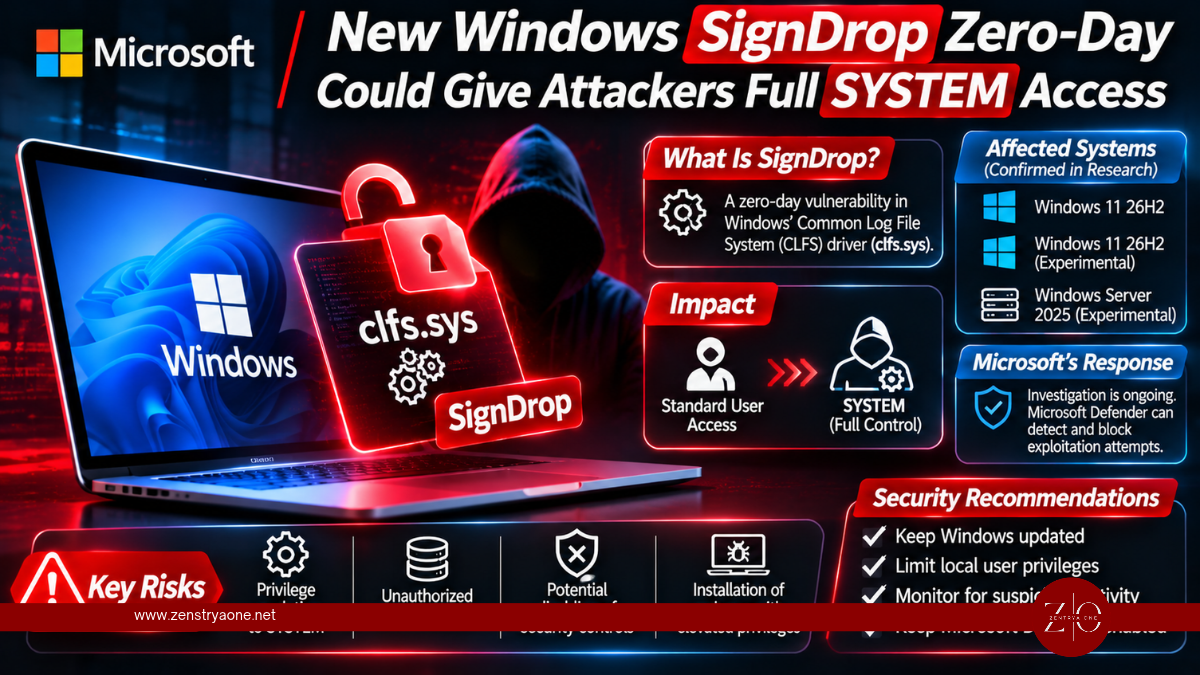
New Windows SignDrop Zero-Day Exploit Could Give Attackers Full SYSTEM Access
New Windows SignDrop zero-day exploit abuses Microsoft CLFS security protections to gain SYSTEM privileges. Learn about affected systems and mitigation.
Every report filed under this tag.
New Windows SignDrop zero-day exploit abuses Microsoft CLFS security protections to gain SYSTEM privileges. Learn about affected systems and mitigation.
TASK#STOMP is a new PowerShell backdoor that steals business documents, Wi-Fi passwords and clipboard data while using scheduled tasks and dual C2 servers for persistent access.
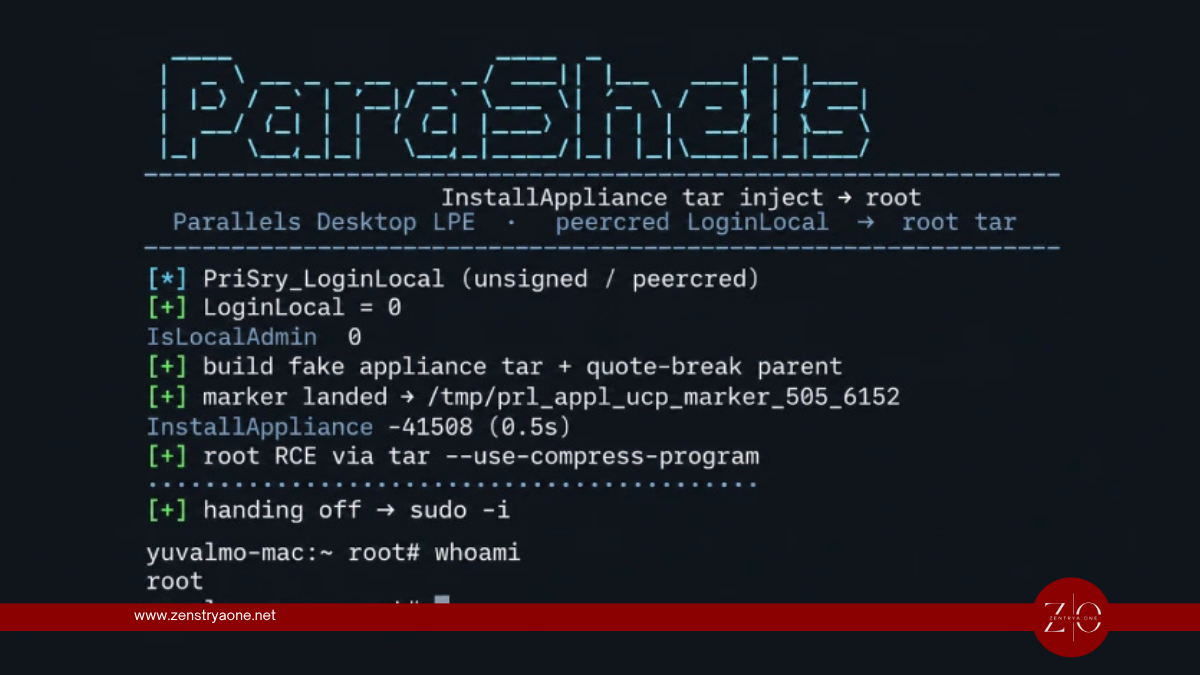
CVE-2026-90894, dubbed ParaShells, allows non-admin Mac users to exploit Parallels Desktop and execute code as root, while Intel Macs currently lack a confirmed fixed version.
A security researcher has released a new proof-of-concept (PoC) demonstrating that Microsoft's recent fix for a Microsoft Defender vulnerability known as **ShieldBreak** can reportedly be bypassed.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.