The Wire
CyberNews by Zentrya One
Tag

Vulnerability

Every report filed under this tag.

critical Malware

Cisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin Ransomware

Threat actors are exploiting vulnerabilities in Cisco Secure Firewall Management Center (FMC) to gain access to enterprise environments, steal credentials and ultimately deploy Qilin ransomware, turning vulnerable security infrastructure into an entry point for broader network compromise.
critical CVE-2018-13379 and CVE-2023-4966 Vulnerabilities

ISA Adds Exploited Cisco, Citrix and Fortinet Flaws to KEV Catalog

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added actively exploited vulnerabilities affecting Cisco, Citrix and Fortinet products to its Known Exploited Vulnerabilities (KEV) catalog.

critical CVE-2026-82533 Vulnerabilities

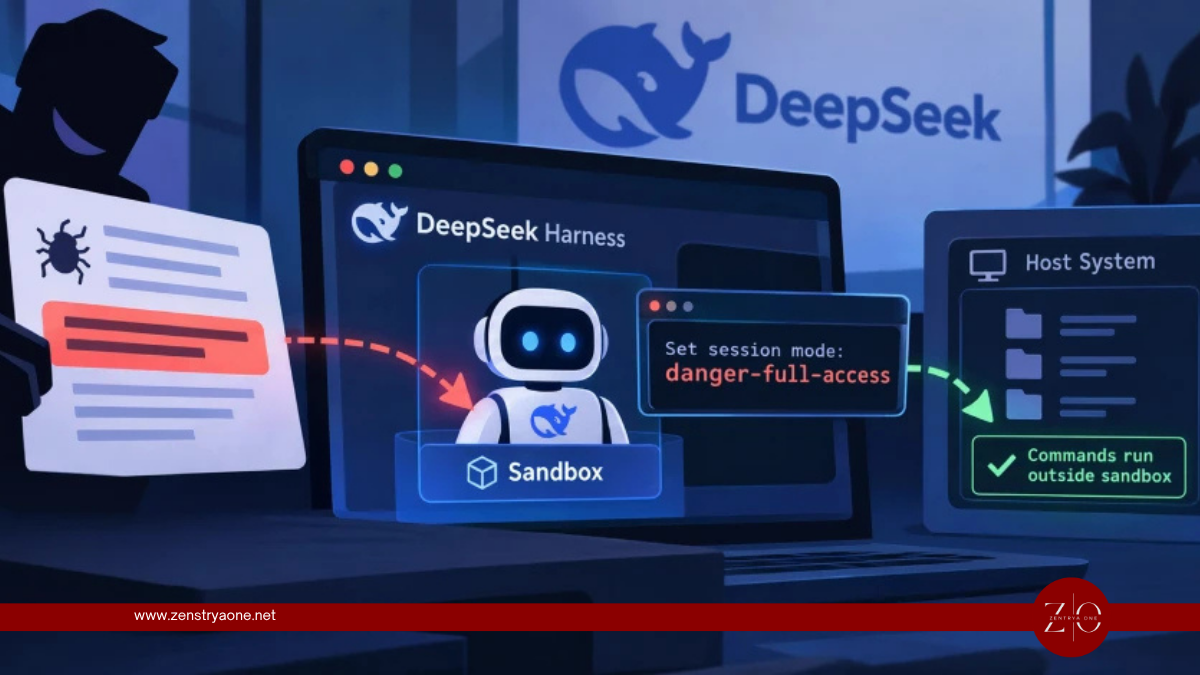
A Sandboxed AI Agent Could Switch Off Its Own Sandbox — and DeepSeek Harness Trusted It

CVE-2026-82533 carries a 9.4 severity score, and the mechanism is almost embarrassingly simple: the harness decided who to trust by reading a header the caller writes itself. Three weeks before the CVE landed, a developer had already posted a working reproduction on DeepSeek's own discussion board.

critical CVE-2026-44756 Vulnerabilities

SAP Fixes CVSS 10.0 OVERPASS Flaw Allowing Unauthenticated Remote Code Execution

SAP has released its September 2026 security updates, addressing multiple vulnerabilities across its enterprise software portfolio, including a maximum-severity flaw in the SAP Kernel that could allow unauthenticated attackers to remotely execute operating-system commands.

critical CVE-2026-69414 Vulnerabilities

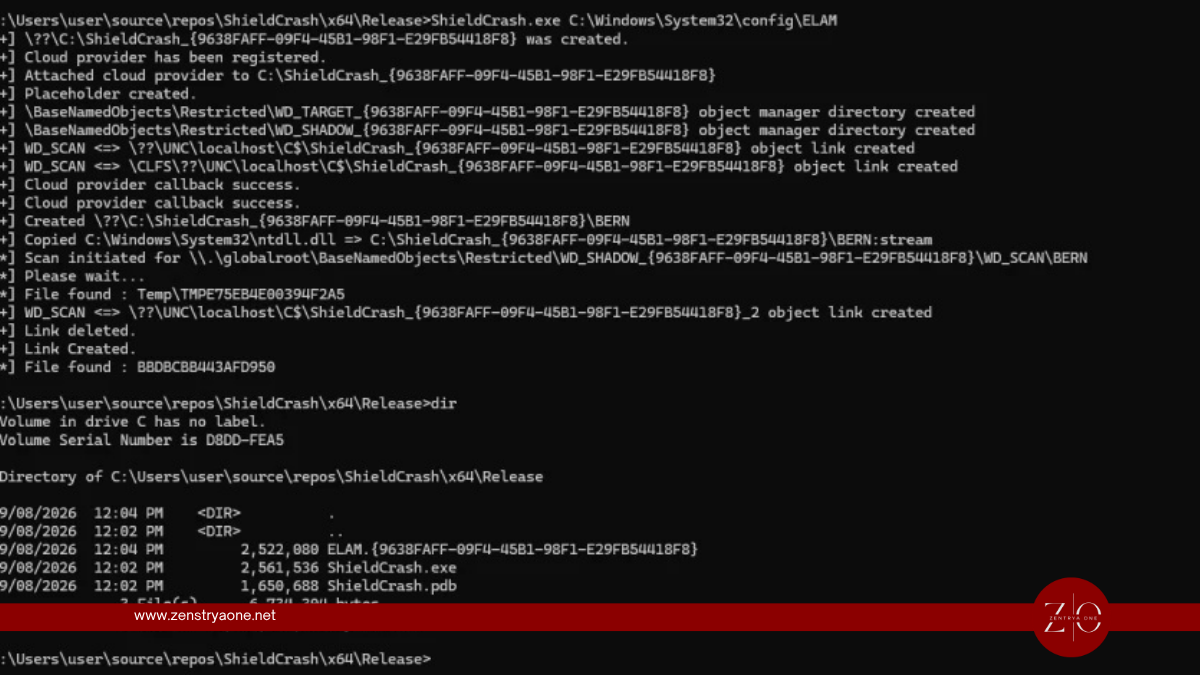
Microsoft Defender Patch Bypassed Again as New ShieldCrash PoC Emerges

A security researcher has released a new proof-of-concept (PoC) demonstrating that Microsoft's recent fix for a Microsoft Defender vulnerability known as **ShieldBreak** can reportedly be bypassed.

The Daily Brief

Stay informed. Stay prepared. Stay one step ahead.

One brief each morning: the advisories that matter, the noise removed.

Double opt-in. One-click unsubscribe in every email. We never sell addresses.